Freedom251 › Software Composition Analysis Software
govulncheck
What govulncheck is
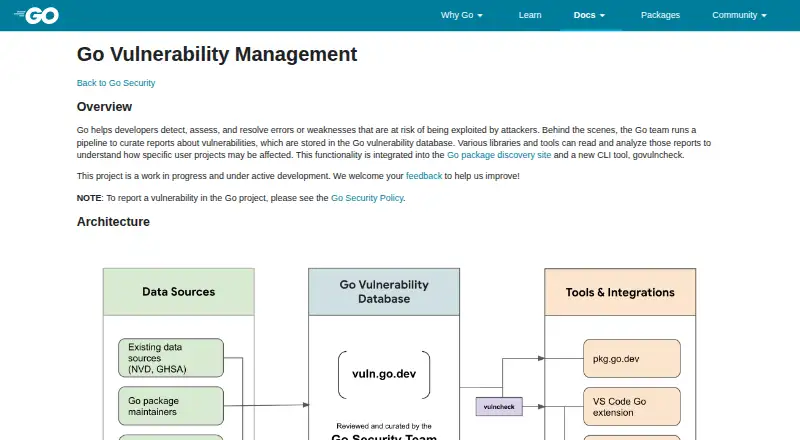
govulncheck is free, open-source software that reports known vulnerabilities affecting Go code. It analyzes source code or a compiled binary’s symbol table to focus findings on vulnerabilities that could affect an application. Binary results do not include call stacks. By default, it uses the Go vulnerability database, whose OSV-based reports are reviewed and curated by the Go Security team. Requests to that database contain only module paths for vulnerabilities already known there, not source code or other program properties. The `-db` option can select another database through HTTP, HTTPS, or file URLs when it implements the documented API. Results can stream as JSON or use SARIF and OpenVEX formats, and the tool can generate SBOMs. The Go language server gopls integrates its analysis, with documented use through VS Code and Vim or NeoVim via coc.nvim. It is self-hosted and supports Go. Reflection is invisible to source analysis, `unsafe` can cause missed findings, and binaries built before Go 1.18 receive only standard-library vulnerability checks.
Who it suits
govulncheck suits Go developers and teams scanning source code or compiled Go binaries for known vulnerabilities. It also fits self-hosted workflows using editor integrations, CI output formats, or SBOM generation.
What it does well
- Free, open-source vulnerability scanning for Go
- Focuses reports on potentially reachable vulnerabilities
- Supports JSON, SARIF, and OpenVEX output
- Integrates with gopls and documented editors
- Can scan compiled binaries and generate SBOMs
What to know first
- Reflection calls are invisible to source analysis
- Use of unsafe may cause false negatives
- Older binaries get only standard-library checks
- Editor scanning omits standard libraries and toolchains
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Govulncheck | Go source code or binaries · Go vulnerability database | Free |
As go.dev lists them, read 5 Oct 2026. The maker's own page has the final word.
Verdict
govulncheck provides focused vulnerability analysis for Go source and binaries, with several machine-readable outputs and editor connections. Its analysis boundaries mean results should be interpreted within the stated limits.
Facts from govulncheck's own pages
- Analysis limits
- Reflection calls are not visible to source analysis, and use of `unsafe` may cause false negatives. · pkg.go.dev, 5 Oct 2026
- Binary limits
- Binaries built with Go versions before 1.18 are checked only for standard library vulnerabilities. · pkg.go.dev, 5 Oct 2026
- Binary scanning
- It can scan compiled Go binaries using their symbol information, but binary results omit call stacks. · pkg.go.dev, 5 Oct 2026
- Custom database
- The `-db` flag can point govulncheck to a different database using HTTP, HTTPS, or file URLs, provided it implements the documented API. · go.dev, 5 Oct 2026
- Editor integration
- The Go language server gopls integrates govulncheck analysis, and the Go docs describe use with VS Code and Vim or NeoVim via coc.nvim. · go.dev, 5 Oct 2026
- Editor limits
- The documented editor scanning features currently do not report vulnerabilities in standard libraries or toolchains. · go.dev, 5 Oct 2026
- Install
- The Go docs show installing it with `go install golang.org/x/vuln/cmd/govulncheck@latest`. · go.dev, 5 Oct 2026
- Output formats
- Govulncheck supports streaming JSON, SARIF, and OpenVEX output. · pkg.go.dev, 5 Oct 2026
- Privacy
- The package documentation says database requests contain only module paths for vulnerabilities already known to the database, not code or other properties of the program. · pkg.go.dev, 5 Oct 2026
- Project status
- The Go vulnerability management project is described as a work in progress and under active development. · go.dev, 5 Oct 2026
- Purpose
- Govulncheck reports known vulnerabilities that affect Go code. · pkg.go.dev, 5 Oct 2026
- Reachability analysis
- It uses source code analysis or a binary’s symbol table to focus reports on vulnerabilities that could affect the application. · pkg.go.dev, 5 Oct 2026
- Support
- The Go docs direct govulncheck issues and feedback to the Go issue tracker. · go.dev, 5 Oct 2026
- Vulnerability data
- By default it uses the Go vulnerability database, whose reports use the OSV schema and are reviewed and curated by the Go Security team. · go.dev, 5 Oct 2026