Freedom251 › Web Application Firewall Software

F5 WAF for NGINX
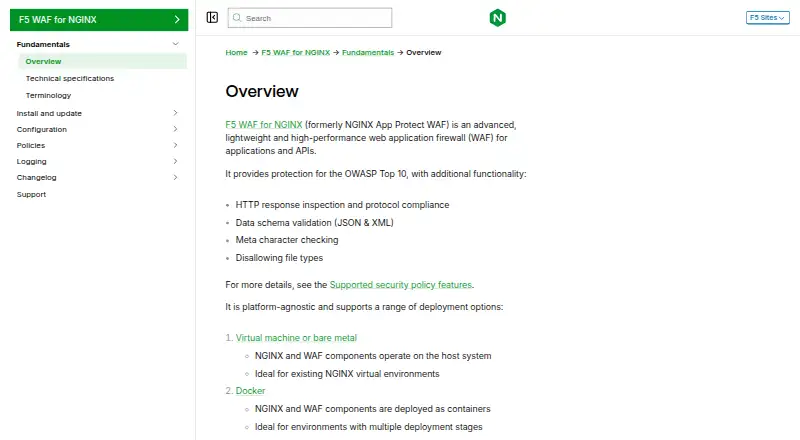
What F5 WAF for NGINX is
F5 WAF for NGINX is a paid, hybrid web application firewall for applications and APIs, with pricing available on request and a free trial. It protects against the OWASP Top 10 and checks HTTP responses, protocol compliance, JSON and XML schemas, meta characters, and disallowed file types. Predefined attack signatures can inspect requests and responses. Bot defense is enabled by default, examining User-Agent headers and request URIs with header-anomaly detection, while threat campaigns provide contextual feeds about active campaigns observed by F5 Threat Labs. The firewall runs natively on NGINX Plus and NGINX Ingress Controller and is included in NGINX One premium packages. Deployment options include virtual machines or bare metal, Docker, and Kubernetes. Supported systems include listed Alpine, Amazon Linux, Debian, Oracle Linux, RHEL, Rocky Linux, and Ubuntu releases. It supports up to 127 CPU cores. NGINX Instance Manager offers a REST API for policies, logs, signatures, and campaigns. MyF5 provides installation and usage assistance. Some NGINX subrequest-dependent features may not function as expected on the same route.
Who it suits
It suits teams protecting web applications and APIs in NGINX-based, virtual-machine, container, or Kubernetes environments. It is aimed at deployments needing managed rules, API protection, bot management, and rate limiting.
What it does well
- Protects against the OWASP Top 10
- Supports VM, bare-metal, Docker, and Kubernetes deployment
- Bot defense enabled by default
- Provides REST management through NGINX Instance Manager
- Offers managed rules, API protection, and rate limiting
What to know first
- Pricing is available only on request
- No free plan
- Supports a maximum of 127 CPU cores
- Some subrequest-dependent features may not work as expected
Limits
The product supports up to 127 CPU cores. NGINX subrequest-dependent features such as ExternalAuth, APIKey, remote-JWKS JWT, OIDC, and cache background updates may not function as expected on the same route.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| F5 WAF for NGINX subscription | pricing varies by deployment size · covered environments · required features | On request |
As docs.nginx.com lists them, read 30 Sept 2026. The maker's own page has the final word.
Getting started
- Open the F5 WAF for NGINX documentation website
- Request subscription pricing for your deployment size, environments, and required features
- Choose a supported Linux system and deployment target
- Deploy on a virtual machine, bare metal, Docker, or Kubernetes
- Integrate with NGINX Plus or NGINX Ingress Controller
- Use a free trial or subscription and manage policies through NGINX Instance Manager
Verdict
F5 WAF for NGINX combines application and API protection with NGINX-native deployment, signatures, bot controls, and threat feeds. Confirm pricing, supported systems, and route-specific integration limits before choosing it.
Questions
What is the pricing model?
F5 WAF for NGINX is paid, with pricing available on request. A free trial is offered, but there is no free plan.
Where can it run?
It supports virtual machines or bare metal, Docker, and Kubernetes deployments on listed Linux systems.
Does it integrate with NGINX products?
It runs natively on NGINX Plus and NGINX Ingress Controller and is included in NGINX One premium packages.
How are policies managed?
NGINX Instance Manager provides a REST API for managing WAF policies, log profiles, attack signatures, bot signatures, and threat campaigns across instances.
What support is provided?
Installation, troubleshooting, and usage assistance are provided through the MyF5 Customer Portal.
Facts from F5 WAF for NGINX's own pages
- Attack signatures
- The product includes predefined attack signatures that can be applied to requests and responses. · docs.nginx.com, 30 Sept 2026
- Bot defense
- Bot signatures inspect User-Agent headers and request URIs, and bot defense is enabled by default with header-anomaly detection. · docs.nginx.com, 30 Sept 2026
- Core protection
- It protects against the OWASP Top 10 and provides HTTP response inspection, protocol compliance, JSON and XML schema validation, meta character checking, and disallowed file-type controls. · docs.nginx.com, 30 Sept 2026
- Current version
- The latest documented F5 WAF for NGINX version is 5.15.0. · docs.nginx.com, 30 Sept 2026
- Deployment
- It supports virtual machine or bare-metal, Docker, and Kubernetes deployments. · docs.nginx.com, 30 Sept 2026
- Founded
- 1996 · docs.nginx.com, 28 Sept 2026
- Headquarters
- Seattle, Washington, USA · docs.nginx.com, 28 Sept 2026
- Ingress integration
- With NGINX Ingress Controller, WAF policies can be applied to VirtualServer, VirtualServerRoute, and Ingress resources through Policy resources referencing WAF bundles or bundle sources. · docs.nginx.com, 30 Sept 2026
- Integration limitation
- NGINX subrequest-dependent features such as ExternalAuth, APIKey, remote-JWKS JWT, OIDC, and cache background updates may not function as expected when used with F5 WAF for NGINX on the same route. · docs.nginx.com, 30 Sept 2026
- Management API
- NGINX Instance Manager provides a REST API for managing WAF policies, log profiles, attack signatures, bot signatures, and threat campaigns across instances. · docs.nginx.com, 30 Sept 2026
- NGINX integration
- F5 WAF for NGINX runs natively on NGINX Plus and NGINX Ingress Controller and is included in NGINX One premium packages. · docs.nginx.com, 30 Sept 2026
- Purpose
- F5 WAF for NGINX is an advanced, lightweight, high-performance web application firewall for applications and APIs. · docs.nginx.com, 30 Sept 2026
- Resource limit
- F5 WAF for NGINX supports a maximum of 127 CPU cores. · docs.nginx.com, 30 Sept 2026
- Support
- Installation, troubleshooting, and usage assistance is provided through the MyF5 Customer Portal. · docs.nginx.com, 30 Sept 2026
- Supported systems
- Supported operating systems include Alpine Linux 3.22 and 3.24, Amazon Linux 2023, Debian 12 and 13, Oracle Linux 8, RHEL/Rocky Linux 8–10, and Ubuntu 22.04, 24.04, and 26.04. · docs.nginx.com, 30 Sept 2026
- Threat intelligence
- Threat campaigns provide frequently updated contextual feeds about active attack campaigns observed by F5 Threat Labs. · docs.nginx.com, 30 Sept 2026
Where F5 WAF for NGINX stands on Freedom251
- Web Application Firewall Software#18 of 35