Freedom251 › Infrastructure as Code Security Software
c7n-left
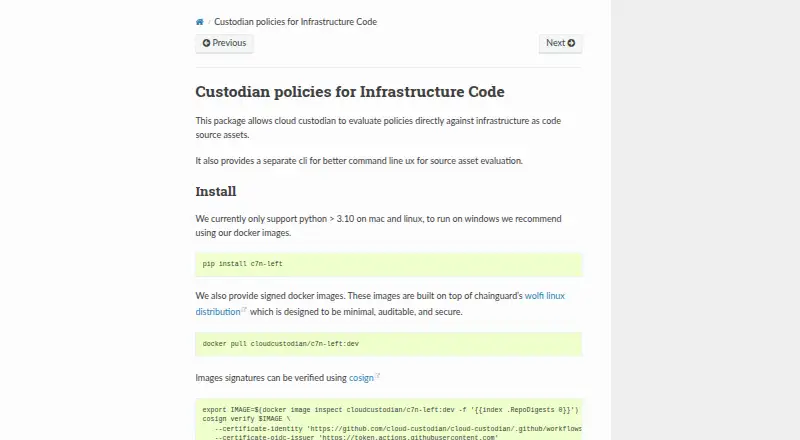
What c7n-left is
c7n-left evaluates Cloud Custodian policies against Terraform infrastructure-as-code source assets. It is designed for policy checks in CI systems and can report findings as annotations in GitHub pull requests. Policies use standard Custodian filters, support multiple resource types, filter taggable resources, and traverse resource graphs across multiple hops. The taggable-resource filter covers Terraform resources from AWS, Azure, GCP, OCI, and Tencent Cloud providers. Command-line filters narrow runs by policy or resource name, category, minimum severity, resource type, or ID. Matching policies make a run exit with code 1 by default, while selected matches can be changed to warnings with `--warn-on`. Policy tests combine Terraform files with YAML or JSON assertion plans. Install the package with `pip install c7n-left`. Python versions above 3.10 are supported on macOS and Linux, and Docker images are recommended for Windows. Those images are signed, built on Chainguard’s Wolfi Linux, and documented for cosign verification. c7n-left is free and open source under Apache 2.0. Terraform root modules are supported, but remote module dependencies must be fetched with Terraform before evaluation.
Who it suits
c7n-left suits teams running infrastructure policy checks in CI, especially those using Terraform and pull-request workflows. It is also useful for organizations managing AWS, Azure, GCP, OCI, or Tencent Cloud resources with Cloud Custodian policies.
What it does well
- Free and open source under Apache 2.0
- Evaluates Terraform infrastructure-as-code
- GitHub mode adds pull-request annotations
- Supports multi-hop resource graph traversal
- Tests policies with YAML or JSON assertions
- Signed Docker images support cosign verification
What to know first
- Remote Terraform modules require prior Terraform fetching
- Windows users are directed to Docker images
- Command-line interface is subject to change
Limits
Remote Terraform module dependencies must be fetched with Terraform before c7n-left runs. The command-line interface may change.
Getting started
- Install with `pip install c7n-left`
- Use Python above 3.10 on macOS or Linux
- Use the documented Docker images on Windows
- Fetch remote Terraform modules with Terraform
- Run policies against Terraform root modules
- Configure GitHub output for pull-request annotations
Verdict
Pick c7n-left for free Terraform policy evaluation in CI, with flexible Custodian filters and pull-request reporting. Consider another tool if your workflow cannot fetch remote modules first or depends on a fixed command-line interface.
Questions
Does c7n-left have a free plan?
Yes. It is free for everyone to use and open source under the Apache 2.0 license.
Which operating systems are supported?
Python above 3.10 is supported on macOS and Linux. Docker images are recommended for Windows.
What infrastructure formats does it evaluate?
It evaluates Terraform root modules and supports Terraform policy tests with assertion plans.
Can it scan pull requests?
Yes. GitHub output mode reports findings as pull-request annotations.
Which cloud providers are covered by the taggable filter?
It supports Terraform resources from AWS, Azure, GCP, OCI, and Tencent Cloud.
How do policy matches affect a run?
Matches cause exit code 1 by default; `--warn-on` can make selected matches warnings instead.
Facts from c7n-left's own pages
- CI integration
- Its GitHub output mode reports annotations directly into pull requests. · cloudcustodian.io, 3 Oct 2026
- CLI stability
- The documentation warns that the command-line interface is subject to change. · cloudcustodian.io, 3 Oct 2026
- Container security
- The project provides signed Docker images built on Chainguard's Wolfi Linux and documents verification with cosign. · cloudcustodian.io, 3 Oct 2026
- Default failure behavior
- Policy matches cause the run to exit with code 1 by default, while `--warn-on` can make selected matches log as warnings instead. · cloudcustodian.io, 3 Oct 2026
- Docker security
- The project provides signed Docker images based on Chainguard’s Wolfi Linux, and documents signature verification with cosign. · cloudcustodian.io, 3 Oct 2026
- IaC input
- c7n-left evaluates Terraform root modules, and remote module dependencies must be fetched with Terraform before running it. · cloudcustodian.io, 3 Oct 2026
- Install
- The package can be installed with `pip install c7n-left`. · cloudcustodian.io, 3 Oct 2026
- Install platforms
- The package supports Python above 3.10 on macOS and Linux, and recommends Docker images for Windows. · cloudcustodian.io, 3 Oct 2026
- Intended users
- The documentation says c7n-left is typically run in CI systems. · cloudcustodian.io, 3 Oct 2026
- Known limitation
- Remote Terraform module dependencies must be fetched with Terraform before c7n-left runs. · cloudcustodian.io, 3 Oct 2026
- License and price
- Cloud Custodian is open source, free for everyone to use, and distributed under the Apache 2.0 license. · cloudcustodian.io, 3 Oct 2026
- Policy checks
- Policies can check Terraform resources using Custodian filters, including tag checks and multi-hop resource traversal. · cloudcustodian.io, 3 Oct 2026
- Policy controls
- Command-line filters can select policies and resources by name, category, minimum severity, resource type, or ID. · cloudcustodian.io, 3 Oct 2026
- Policy language
- Policies support standard Custodian filters, multiple resource types, taggable-resource filtering, and multi-hop resource graph traversal. · cloudcustodian.io, 3 Oct 2026
- Policy testing
- c7n-left supports tests that match policy findings against assertions in plan files. · cloudcustodian.io, 3 Oct 2026
- Policy tests
- c7n-left supports policy tests using Terraform files and YAML or JSON assertion plans. · cloudcustodian.io, 3 Oct 2026
- Project and audience
- Cloud Custodian is an open-source rules engine for managing public cloud accounts and resources, with policies for security, compliance, tagging, and cost management. · cloudcustodian.io, 3 Oct 2026
- Project scope
- Cloud Custodian supports AWS, Azure, and GCP, with Kubernetes, Tencent Cloud, and OpenStack support described as beta on its homepage. · cloudcustodian.io, 3 Oct 2026
- Provider coverage
- The taggable filter supports Terraform resources from AWS, Azure, GCP, OCI, and Tencent Cloud providers. · cloudcustodian.io, 3 Oct 2026
- Purpose
- c7n-left evaluates Cloud Custodian policies directly against infrastructure-as-code source assets. · cloudcustodian.io, 3 Oct 2026
- Supported environments
- The package supports Python versions above 3.10 on macOS and Linux; the documentation recommends Docker images for Windows. · cloudcustodian.io, 3 Oct 2026