Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
For most home networks, “own DNS” means running a local resolver that your devices use for name lookups—not operating the public nameservers for an internet domain. A local service such as Pi-hole or AdGuard Home can provide network-wide filtering and internal hostnames; add Unbound if you specifically want your network to resolve public names recursively instead of forwarding queries to a public provider.
The practical path is to run the service on an always-on machine with a stable local IP address, configure your router to advertise it to clients, then verify that devices actually use it. Plan for a fallback before making it your network’s only DNS server: if the host fails, ordinary web browsing may appear to stop.


What “your own DNS” can mean
DNS—the Domain Name System—translates names such as example.com into information applications can use. That information is not limited to IP addresses: DNS also carries IPv4 (A) and IPv6 (AAAA) records, aliases (CNAME), mail routing (MX), verification and policy text (TXT), service discovery (SRV), reverse lookups (PTR), and delegation and zone metadata (NS and SOA).
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Several different services are casually called “DNS servers,” but they do different jobs:
#1 Best Overall
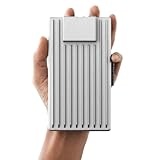
- Server-Class Home Server Built for 24/7 Workloads - Designed as a purpose-built home server rather than general-purpose SBCs, Mini PCs, entry NAS systems, or routing-only devices. As a compact, pocket-sized single board server platform, ZimaBoard 2 1664 combines x86 architecture, quad-core performance up to 3.6GHz, 16GB DDR5 memory, and 64GB eMMC storage for reliable always-on home servers, homelabs, and self-hosted workloads.
- PCIe 3.0 x4 Expansion for Real Server Builds - Built as a server-class platform with native PCIe expansion, ZimaBoard 2 features a full PCIe 3.0 x4 slot for high-speed, low-latency upgrades beyond USB-based limitations. Supports 10GbE NICs, NVMe adapters, GPUs, and AI accelerators to build scalable home servers, homelabs, and advanced self-hosted systems—offering greater expansion flexibility than typical SBCs, Mini PCs, and entry-level NAS devices.
- Native Dual SATA & Dual 2.5GbE Networking - Built with server-class storage and networking I/O, ZimaBoard 2 integrates dual SATA ports for direct HDD/SSD connectivity and dual 2.5GbE Ethernet for high-throughput, low-latency networking. This architecture enables reliable DIY NAS, fast storage, routing, and multi-service home server deployments—while avoiding USB-based performance constraints common in ARM SBCs, Raspberry Pi–based setups, Mini PCs, and entry-level NAS devices.
- ZimaOS Preinstalled + Wide OS Compatibility - Comes preinstalled with ZimaOS for a clean, ad-free private cloud experience—centralized file dashboard, automatic backups, P2P downloads, private photo/video sharing, 500+ plug-ins, and secure on-device AI that keeps your data at home. Also supports TrueNAS, Proxmox, Debian, Ubuntu Server, pfSense, OpenWrt, and Linux containers, making it perfect for Plex media servers, Pi-hole, firewalls, backups, Docker labs, home-cloud services, and multi-service deployments.
- All-in-One NAS, Router, Docker & Homelab Server - Replace multiple devices with one low-power. ZimaBoard 2 can serve as a NAS, router, Docker host, firewall, media server, or homelab node—delivering a flexible, open alternative to ARM SBCs, Mini PCs, and entry-level NAS systems.
- Stub resolver: The small DNS client in a computer or phone. It asks a configured resolver for answers.
- Forwarder: A server that passes a query to another resolver, often after checking its cache or filtering rules.
- Recursive resolver: A resolver that finds an answer by consulting cached data or following DNS referrals through the hierarchy. Unbound is a validating, recursive, caching resolver.
- Authoritative server: A server that publishes the official records for a particular DNS zone.
- Filtering DNS server: A forwarder or resolver that also applies rules, often returning a sinkhole or other response for blocked domains. Pi-hole and AdGuard Home are common self-hosted examples.
A typical home setup is a filtering forwarder: clients ask Pi-hole or AdGuard Home, which checks its cache and rules, then forwards permitted public-domain queries to an upstream resolver. For local recursion, the filter can instead send those queries to Unbound. Pi-hole documents both the filtering role and the optional Unbound arrangement in its documentation and Unbound guide.
Running an authoritative server for a public domain is a different project. It involves publishing records and arranging reliable delegation through the domain’s registrar and DNS infrastructure. You do not need BIND or public nameservers merely to give your home devices local names or block some DNS requests.
Choose the setup that matches your goal
| Your goal | Reasonable starting point | Main trade-off |
|---|---|---|
| Basic network DNS with little upkeep | Your router’s DNS service or a managed/public resolver | Fewer local controls and less visibility; features vary by router or provider. |
| Network-wide hostname-based filtering | Pi-hole or AdGuard Home | Requires an always-on host and can produce false positives. Public queries are usually forwarded to an upstream. |
| Local recursive caching and DNSSEC validation | Unbound | More setup and troubleshooting; it does not itself provide the same blocklist interface as a filtering product. |
| Filtering plus local recursion | Pi-hole or AdGuard Home in front of Unbound | More components to maintain; direct recursive lookups can behave differently from forwarding to a nearby resolver. |
| Internal zones or public-domain DNS administration | An authoritative server such as BIND, NSD, or Knot DNS, or a managed DNS provider | Zone management and, for public hosting, reliable delegation and availability are your responsibility. |
| Enterprise traffic steering and advanced routing | A deliberately designed stack that may include BIND, Unbound, and dnsdist | Substantially more complexity than a normal household needs. |
AdGuard Home and Pi-hole are both intended for network-wide DNS control. Choose based on the interface, features, and maintenance model you prefer rather than assuming one is universally better. If the goal is only to use a public resolver or a provider’s managed filtering, self-hosting is optional; examples include Cloudflare DNS, Quad9, NextDNS, and AdGuard DNS. Check providers’ live documentation for current features and terms.
Free tools Windows power users keep installed
One-click scans. No signup required.
A practical home setup
The least complicated self-hosted route is to install one filtering service, point your network’s DHCP configuration at it, and verify the result. A Raspberry Pi is not required: an existing always-on Linux server, mini-PC, suitable NAS, or other supported host may be enough. Avoid buying hardware if you already have a reliable machine that can run the service continuously.
- Choose a host and reserve its address. The DNS server needs a stable LAN IP address so router settings do not point to an obsolete address after a lease change. Use a DHCP reservation in the router or configure a static address in a way that does not conflict with the DHCP pool.
- Install Pi-hole or AdGuard Home. Follow the project’s current official installation instructions for your operating system. Pi-hole’s documentation is at docs.pi-hole.net; AdGuard Home’s setup guidance is in its getting-started guide. Keep the service and host patched.
- Test it from one client first. Query the new server directly before changing the whole network. For example, if its address is
192.168.1.10, usedig example.com @192.168.1.10. On systems withoutdig, use an available DNS diagnostic such asnslookup. - Change the router’s DHCP DNS setting. Sign in to the router and look under labels such as LAN, DHCP, Local Network, or Network Settings. Set the DNS server advertised to clients to the local host’s reserved address, then save. Router labels and behavior differ, so consult that router’s documentation if the setting is unclear.
- Renew client settings and verify. Reconnect devices or renew their DHCP leases, then check the resolver configured on each kind of network you use. A router may proxy DNS and show itself as the client’s server even while forwarding to your local service; the service’s query log can help confirm whether queries are arriving.
- Start with conservative filtering. Enable a modest set of blocklists, test important sites and apps, and add exceptions only when you can identify the blocked hostname responsible.
Do not assume that changing the router’s IPv4 DHCP field covers every device. Some routers advertise themselves as a DNS proxy, mesh systems may not allow custom DHCP DNS, IPv6 router advertisements can provide a separate resolver, and guest networks may use separate DHCP and firewall settings. Browsers and apps can also use their own encrypted DNS, VPN, private relay, or hard-coded resolver. Check the actual path from representative devices, including IPv6 and guest-network clients if you use them.
Forwarding or resolving public names yourself?
With a conventional upstream, your local filter forwards permitted queries to a public resolver. This is easier to operate and may use a nearby, well-provisioned service. The upstream resolver receives the queries sent to it, subject to its own architecture and policies.
With local recursion, Unbound follows the public DNS hierarchy: it can consult root-server information, then the relevant top-level-domain servers, then the domain’s authoritative servers. Its cache can serve repeated answers until their TTLs expire. A common Pi-hole integration runs Unbound locally on 127.0.0.1 port 5335, with Pi-hole configured to use it as its upstream; follow the current Pi-hole guide for configuration details.
Recursion changes the trust and traffic pattern; it does not make DNS anonymous. It can reduce dependence on a single public recursive provider, but the resolver still communicates with external DNS infrastructure. The ISP, network operator, operating system, browser, VPN, or application may also have visibility or use a different path. NLnet Labs’ DNS privacy analysis discusses these limits. Caching can make repeat lookups faster, but cold recursive lookups may take more steps than forwarding to a nearby resolver; performance depends on cache hits, network conditions, DNSSEC work, and the application.
DNSSEC and encrypted DNS solve different problems. DNSSEC helps validate the authenticity and integrity of DNS data; it does not encrypt queries. DNS-over-TLS (DoT) and DNS-over-HTTPS (DoH) encrypt the connection between a client and its chosen resolver, but that resolver can still see queries. Using encrypted DNS may also bypass local filtering if clients are configured to use another provider.
Test the path and DNSSEC
These commands are examples for a Linux or macOS shell with dig installed. Replace the sample address or port with the one you actually configured:
dig example.com
 dig example.com @192.168.1.10
 dig +trace example.com
The first query uses the system-selected resolver; the second asks the specified local server directly; +trace helps inspect delegation through the hierarchy. Check the operating system’s resolver configuration as well:
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →- Linux:
resolvectl statusand, where relevant,cat /etc/resolv.conf - macOS:
scutil --dns - Windows PowerShell:
Get-DnsClientServerAddress
If Unbound is configured on the Pi-hole guide’s example port, test it directly with:
dig example.com @127.0.0.1 -p 5335Pi-hole’s guide also documents DNSSEC checks using these test names:
dig fail01.dnssec.works @127.0.0.1 -p 5335
dig +ad dnssec.works @127.0.0.1 -p 5335
In the documented test arrangement, the deliberately broken DNSSEC name should fail with SERVFAIL, while the valid name should return an answer with the ad flag when validation is working. Test domains and resolver behavior can change, so treat these as diagnostics rather than permanent guarantees.
To check whether a service is listening on the expected port on Linux, run:
sudo ss -lntup | grep ':53'
sudo ss -lntup | grep ':5335'
Use the port that applies to your setup. For Unbound configuration validation, run sudo unbound-checkconf. For BIND, use sudo named-checkconf and, when checking a zone file, sudo named-checkzone zone-name /path/to/zonefile. These commands validate different software; they are not interchangeable.
Give home devices names
For a home-only namespace, use home.arpa, reserved for home-network naming, rather than making up a pseudo-public suffix or using a domain you do not own. Example names might be nas.home.arpa, printer.home.arpa, and router.home.arpa.
There are several levels of local naming:
- Manual host records: Add a few names and addresses in the router or DNS product. Keep addresses stable or update records when they change.
- DHCP-integrated names: A router or DNS service associates client names with their leases, reducing manual work. The details depend on the DHCP server and how it shares lease information with DNS.
- Private authoritative zone: Run an authoritative service for an internal zone when you need full zone control or many records. This is more administration than adding a handful of local records.
- Split-horizon DNS: Serve different answers for the same domain depending on where the client is. This can be useful if you own the domain, but requires careful zone design to avoid inconsistent internal and external results.
Security, privacy, and availability
Keep recursion private. A recursive resolver should answer only trusted local clients. Bind it to loopback or LAN interfaces where appropriate, restrict allowed client networks, and use firewall rules to block untrusted access. Do not forward DNS port 53 from the public internet to a home resolver. An exposed open resolver can be abused. In particular, do not copy a BIND example that allows recursion from any as a safe default; the DZone architecture article includes such a rule in an example, but unrestricted recursion is not suitable for an internet-reachable server.
Protect the management interface. Use a strong administrator password, keep the dashboard accessible only from the LAN or a trusted VPN, and do not expose it directly to the internet. Restrict access to query logs: they can reveal household devices and browsing-related activity. Choose how long to retain logs, disable them if you do not need them, and secure backups that contain configuration or history.
Recommended Free Tools
Plan for failure. A single DNS host is a single point of failure. If it goes offline, clients may lose name resolution even when the internet connection itself is working. Before switching the whole network, know how to restore the previous router DNS setting. More resilient users can run two filtering hosts or use a supported failover design. A public fallback can restore service, but clients may bypass local filtering and send queries to a third party when the local server is unavailable. Do not add a second resolver casually if you expect every query to follow one policy.
Best Value

- Made from solid aluminum, this 8x12 inch metal sign is built to last with a scratch-resistant surface that keeps the humorous design looking sharp and vibrant.
- The witty slogan delivers laughs with its playful humor, creating an instant conversation starter that guests will notice and enjoy.
- Great for man caves, garages, living rooms, bars, and parties, this funny sign adds a lighthearted touch to any space.
- The great gag gift for friends, family, and anyone who appreciates a good laugh and has a sense of humor.
- The rigid aluminum frame holds its shape without bending; mounts quickly on any wall for instant humor and character.
Filtering is also not a firewall or a complete security product. It blocks selected hostname lookups, not all traffic to an IP address, and it does not stop an application that uses a hard-coded IP. Some devices and browsers make their own DoH or DoT connections. Enforcing a network policy may require endpoint controls or carefully designed firewall rules, and overly broad blocking can disrupt legitimate services.
When filtering breaks something
Blocklists can interfere with logins, payment flows, captive portals, app notifications, video, consent systems, smart-home integrations, or software updates. If a site or app stops working:
- Open the DNS service’s query log and identify recently blocked domains associated with the affected client.
- Confirm which domain is plausibly required for the broken feature; avoid allowing a broad list of unrelated domains.
- Add the narrowest allow rule available and retest the feature.
- Record why the exception was added, then revisit it if blocklists or the service change.
DNS filtering also cannot reliably remove every advertisement. It blocks requests by hostname, so it cannot selectively separate an ad from desired content when both come from the same hostname. Browser content blockers or other application-level controls may complement DNS filtering.
Troubleshooting by symptom
| Symptom | Likely cause | What to check or do |
|---|---|---|
| Browsing appears to stop after setup | The DNS host is offline, unreachable, or incorrectly configured. | Query the local server directly. Restore the router’s previous DNS setting or use your planned fallback while investigating. |
| Some devices use filtering; others do not | Stale DHCP leases, separate guest-network settings, IPv6 DNS, or client-side encrypted DNS. | Renew leases, inspect the resolver on each device and network, and check IPv6 router advertisements and browser settings. |
| Ads or trackers still appear | The request’s hostname is not on the blocklist, the device uses another resolver, or the content shares a hostname with allowed content. | Check the query log and resolver path. Add client-level controls if hostname filtering cannot distinguish the content. |
| An internal name fails | Wrong or missing record, changing address, incorrect zone, or an unconfigured search domain. | Query the server directly with dig nas.home.arpa @192.168.1.10 and inspect the record and client’s DNS suffix behavior. |
| An app or login breaks | A blocklist false positive. | Use the query log to identify the blocked hostname and allow only the narrowest required name. |
| Lookups seem slow | Cold cache, upstream reachability, recursive path, or local network latency. | Compare direct and system-selected queries, inspect service logs, and test again after cache warm-up. Do not assume recursion is always faster. |
| Unknown internet clients appear in logs | The service may be exposed on a public interface, through a firewall rule, or by port forwarding. | Remove public exposure immediately; restrict listening interfaces, recursion ACLs, and firewall access to trusted networks. |
When BIND or public authoritative DNS makes sense
BIND is a capable DNS server, but it is not required for a normal home filtering setup. Consider an authoritative server such as BIND, NSD, or Knot DNS when you need to manage complete private zones, learn DNS operations, or publish records for a domain you control. For public authoritative DNS, you must also arrange registrar delegation to reliable nameservers, handle required glue records where applicable, plan DNSSEC appropriately, and monitor availability. A home resolver and a public authoritative service are distinct roles; combining them needs deliberate interface, access-control, and port planning. Unbound’s manual notes that authoritative and recursive roles require careful setup, including because both commonly use port 53.
For most households, the sensible progression is simpler: start with router DNS if you want minimal upkeep; choose Pi-hole or AdGuard Home for local filtering and names; add Unbound only if local recursion is a specific goal. If you need your public domain’s records hosted, a managed authoritative DNS provider may be easier to operate than running internet-facing nameservers yourself.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

