What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
XE Group, long associated with payment-card skimming and credential theft, was observed exploiting two vulnerabilities in Advantive VeraCore, a warehouse-management and fulfillment platform. Researchers reported web shells, information theft and attempts to reach other systems. The campaign shows a move into organizations that support manufacturing, distribution and e-commerce—but the available evidence does not establish that XE compromised VeraCore’s software-development pipeline or poisoned updates for all customers.
In brief: The campaign involved CVE-2024-57968, an authenticated file-upload vulnerability affecting VeraCore versions before 2024.4.2.1, and CVE-2025-25181, a SQL-injection flaw affecting versions through 2025.1.0. Both were added to CISA’s Known Exploited Vulnerabilities catalog on March 10, 2025. Those version boundaries describe historical affected releases; VeraCore operators should confirm the current fix and supported upgrade path with Advantive’s release guidance.
What changed in XE Group’s activity?
XE Group has been tracked by researchers as a cybercrime actor associated with payment-card skimming, credential theft and compromised internet-facing services. Researchers and threat-intelligence vendors have linked the group to Vietnam, but that is an attributed assessment—not a public law-enforcement determination of nationality. Reporting on the VeraCore investigation describes activity that goes beyond the group’s better-known web skimming: attackers targeted a business application, sought durable access and attempted to collect information from operational environments.
In a typical card-skimming operation, malicious code is inserted into an e-commerce site to capture payment details as customers enter them. The VeraCore activity used application vulnerabilities to reach systems used in fulfillment and distribution. Researchers reported web-shell deployment, collection of configuration files, attempted access to remote systems, obfuscated PowerShell and a remote-access payload in parts of the activity.
#1 Best Overall

- With Square Terminal, you can ring up sales, accept payments, and print receipts, all with one device. Use it at the counter or ring up customers anywhere in your store.
- Accept all major credit and debit cards and pay one low rate with no hidden fees and no long-term contracts.
- Process chip cards in just two seconds.
- Get your money as soon as the next business day.
- Use it cordlessly with the built-in battery, designed to last all day.
This is evidence of an expansion in observed tactics and targets, not proof that XE has permanently abandoned skimming or replaced its former criminal business model.
Why target warehouse-management software?
VeraCore supports warehouse-management and fulfillment work, coordinating processes such as orders, inventory and distribution. It is used by fulfillment companies, commercial printers and e-retailers. A compromised operational application can be valuable beyond the application itself: configuration files may expose credentials, connection details, internal network information or links to other systems. Depending on the organization’s deployment and integrations, the host may also provide a route toward customer, order or shipment data.
Rank #2

- Get your money as soon as the next business day.
- Get set up quickly with no long-term commitments. Download the Square Point of Sale app for free, create an account, and start taking payments anywhere.
- Run your business all in one place with the free Square Point of Sale app. Track your sales, manage inventory, accept tips, send receipts digitally, and more.
- Works with Apple devices with a Lightning connector.
That makes the platform an attractive foothold, but it does not mean every VeraCore customer was attacked or compromised. The reporting concerns observed environments, not universal exposure.
Free tools Windows power users keep installed
One-click scans. No signup required.
The two VeraCore vulnerabilities
| CVE | Issue and affected versions | What defenders should know |
|---|---|---|
| CVE-2024-57968 | Unrestricted file upload; versions before 2024.4.2.1 | NVD’s description says a remote authenticated user could upload files to unintended folders, including web-accessible locations. Researchers reported that the weakness was used to place web shells. |
| CVE-2025-25181 | SQL injection in timeoutWarning.asp, involving the PmSess1 parameter; versions through 2025.1.0 |
The flaw could allow remote attackers to execute SQL commands. Its presence does not, by itself, prove that data was stolen from a given installation. |
The file-upload issue is not simply a matter of accepting the wrong file type. If an attacker can place server-side content in a location the web server can access or execute, the impact may include code execution or a web shell, depending on application and server configuration. The NVD description specifies authentication, so it should not be characterized as wholly unauthenticated; stolen, reused or otherwise obtained credentials can still make an authenticated weakness exploitable.
Rank #3
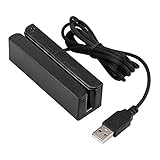
- MSR90 is a USB emulation keyboard interface that not need any driver or software,USB simply plug and play
- Reads up to 3 tracks of information,can reads ISO7811, AAMVA, CA DMV and most other card data formats
- Threaded inserts for mounting. LED indicator, green light is on when connecting,green light blinks when cards swiped
- Bi-directional swipe reading, superior reading of high jitter, scratched, and worn magstripe cards, reliable for over 1,000,000 card swipes
- Configuration software makes configuration changes easy,works with: Windows OS and Mac OS
Severity scores differ by assessor. For CVE-2024-57968, the MITRE/CNA score is 9.9 Critical, while NVD lists 8.8 High. For CVE-2025-25181, the CNA score is 5.8 Medium and NVD lists 7.5 High. These scoring differences reflect different assessments; a lower score does not make a flaw harmless where the application holds sensitive operational data. Both CVEs were added to CISA’s KEV catalog and CISA’s KEV catalog on March 10, 2025. CISA set a March 31, 2025 remediation deadline for federal agencies; that historical federal deadline is not a substitute for an organization’s own risk-based response.
The vulnerabilities were reported as previously unknown in the initial research and received CVE identifiers on February 3, 2025. “Zero-day” describes their status before public disclosure, not a permanent label for them today.
Rank #4
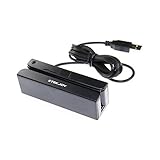
- USB interface, keyboard emulation, no need to install software to read, configuration software for changing settings available.
- Read data from all 3 tracks, high and low coercivity cards, ISO7811, AAMVA, CA DMV and most magnetic card data formats.
- Work on Windows, Mac and other USB capable systems. Work with TXT, notepad, Word, Excel, POS systems and son on.
- Compact size, with 145cm USB cord, two 3mm-diameter screw holes for fixing at the bottom, a LED indicator light
- Perfect for POS, Banking, Loyalty, Access Control, ID verification and other applications.
What researchers reported about the attack chain
At a defensive level, reporting describes a sequence in which XE gained access to VeraCore environments, exploited application weaknesses, placed web shells, collected configuration files and attempted to reach other systems. Obfuscated PowerShell and a remote-access tool appeared in portions of the activity. These details should not be taken to mean every affected organization saw the same tools or every step.
Recommended Free Tools
One observed environment reportedly showed access dating to January 2020. That is a finding about at least one environment, not a claim that all victims were compromised for four years. It is still a critical warning: a patch can close the original entry point while leaving behind a web shell, stolen credentials, altered files or access established elsewhere.
Best Value

- Pay one transparent rate per swipe for Visa, Mastercard, Discover and American Express.
- Works in conjunction with most downloadable Square point-of-sale apps on your device. Customers can pay, tip and sign directly on your device. Track payments in cash, gift cards and more. Also lets you send receipts via e-mail or text message, makes it easy to apply discounts, keeps a data and sales history log and more.
- Accepts magstripe credit card payments, including those from Visa, Mastercard, Discover and American Express (fees apply).
- App sends deposits to your bank account within 1 to 2 business days, or enjoy instant deposits (fees apply).
Does “supply-chain attack” mean VeraCore updates were poisoned?
No such conclusion is established by the available evidence. The campaign targeted organizations involved in supply-chain operations through a business application. That is different from compromising a software vendor’s build or release systems and distributing a malicious update to customers.
- Supply-chain-sector targeting: supported—the victims and operational context include fulfillment, distribution and related businesses.
- Exploitation of a third-party enterprise application: supported—the reported access involved VeraCore vulnerabilities.
- Compromised software-development or update pipeline: not established in the reporting cited here.
- Every customer affected: not supported; the reports describe observed compromises, not universal compromise.
For this reason, the most precise description is an attack on supply-chain-related organizations through vulnerable warehouse software, rather than a confirmed malicious-update campaign. NIST’s cybersecurity supply-chain risk-management guidance is useful for the broader task of identifying suppliers, defining security requirements and monitoring third-party dependencies.
What VeraCore operators should do
- Find every installation. Inventory production, test, legacy and disaster-recovery VeraCore instances, including systems hosted by service providers. Record exact versions, internet exposure and the party responsible for patching. Ask fulfillment and hosting partners whether they operate VeraCore on your behalf.
- Verify and apply vendor remediation. Treat versions before 2024.4.2.1 as historically affected by CVE-2024-57968 and versions through 2025.1.0 as historically affected by CVE-2025-25181. Confirm the current supported release and remediation path with Advantive’s release notes. If compromise is suspected, preserve relevant evidence before making changes where feasible.
- Assess for compromise as well as exposure. Review web-server and upload logs, authentication records, PowerShell telemetry and unexpected outbound connections. Look for unfamiliar server-side files, including unexpected ASPX files, as well as unexplained administrator accounts, scheduled tasks, services and persistence. Absence of a known indicator is not proof that a system is clean.
- Rotate exposed secrets. Reset VeraCore credentials and rotate database credentials, service-account passwords, API keys, integration secrets and certificates that may have appeared in configuration files. Revoke sessions or tokens where supported. Coordinate rotations so dependent integrations are not silently broken.
- Check for movement beyond the application. Review connections from the VeraCore host to databases, file servers, domain services, remote-management systems and partner networks. Investigate unusual administrative access, remote-control activity or PowerShell execution.
- Reduce reachable paths. Restrict management interfaces to trusted administrative networks or VPN access, segment warehouse systems from general corporate networks, and limit unnecessary outbound connections from application servers.
- Escalate on evidence of persistence or theft. Contact Advantive support and engage qualified incident responders if you find a web shell, unauthorized code, stolen credentials or lateral movement. Assess notification, contractual, regulatory and insurance duties according to the data involved and applicable jurisdiction.
- Rebuild when warranted. If persistent unauthorized server-side code or access is confirmed, deleting one discovered shell may leave other footholds intact. A clean rebuild from trusted media or images, followed by validation before reconnecting integrations, may be safer.
Do not equate “patched” with “clean.” The reported long-lived access makes historical logs, backups, server images and authentication records relevant where available. If retention is limited, document what period can and cannot be investigated rather than treating missing logs as evidence of no activity.
What the campaign means for defenders
The notable development is not just that two flaws affected a warehouse platform. It is that a group associated with comparatively direct theft—payment cards and credentials—was also observed seeking durable access inside operational environments. A fulfillment system can sit at the intersection of data, infrastructure and business relationships, so its compromise can have consequences beyond a single server.
For organizations using VeraCore, prioritize an accurate asset and version check, vendor remediation, and a compromise assessment. For broader third-party risk programs, distinguish the compromise of a customer’s vulnerable application from compromise of the vendor’s software supply chain. That precision keeps incident scope honest while still treating the operational risk seriously.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

