Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Quishing is phishing delivered through a QR code: a scammer hides a malicious link or other harmful content in the code and persuades you to scan it. The code itself usually is not “hacked”; the risk is what it opens or prompts you to do, such as sign in, pay, share a verification code, or install an app. Treat an unexpected QR code like an unreadable link: preview its destination, then verify through the organization’s known app or website before taking action.
What is quishing?
The word combines “QR code” and “phishing.” A QR code is a machine-readable container. It can hold a website address, contact details, Wi-Fi credentials, payment information, or other data. In a quishing attack, the attacker uses that container as part of a lure—often to send someone to a fake login or payment page, steal account details, deliver malware, or redirect a payment.
Quishing is a delivery or interaction technique, not a particular malware family. QR codes are not inherently unsafe, and scanning one does not automatically give an attacker access to a phone. The danger depends on where the code came from, what it contains, what opens after scanning, and what the person does next.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →A QR code can conceal its destination from a quick glance. It can also move an interaction from a managed work computer to a personal phone, where an employer’s email, browser, network, and endpoint protections may not apply. The FBI described that device pivot in a January 2026 advisory about Kimsuky campaigns targeting specified U.S.-linked organizations; its findings should not be treated as proof that every quishing attempt has the same tactics. FBI advisory
#1 Best Overall

- PORTABLE SCANNER FOR USE ON-THE-GO — The fastest and lightest mobile single-sheet-fed compact document scanner in its class¹
- QUICK DOCUMENT SCANNING ― This Epson ultra-fast scanner scans a single page as quickly as 5.5 seconds²; Windows and Mac compatible
- VERSATILE PAPER HANDLING ― Portable scanner scans documents up to 8.5 x 72 in; Also easily digitizes receipts and ID cards to make accounting, bookkeeping, and organizing simpler
- INTUITIVE, HIGH-SPEED SOFTWARE — Epson ScanSmart Software³ is a smart tool allowing you to easily scan, review, and save; Stay organized easily with the help of this Epson scanner
- EASY SETUP — USB-powered connect to your computer for quick and simple scanning; No batteries or external power supply required to operate portable document scanner; Standard Connectivity: USB 2.0
How a quishing attack works
- A lure creates a reason to scan. A message or sign may claim that an account needs attention, a package cannot be delivered, a payment is due, or a document is waiting.
- The QR code hides the destination. It may be embedded in an email or document, printed on a sign, or placed over a legitimate code.
- The phone decodes the code. Depending on the scanner and device settings, it may show a destination preview or offer to open a link.
- A page or redirect chain loads. A fake page may imitate a bank, employer, delivery company, Microsoft 365, VPN, or another service. Some campaigns tailor the page to the device or use intermediate redirectors.
- The page asks for a consequential action. It may request a password, payment-card details, a one-time code, an app download, or an approval.
- The attacker uses what was provided. Possible consequences include account takeover, payment fraud, stolen session tokens, malware, or follow-on scams.
In its January 2026 advisory, the FBI described Kimsuky campaigns using mobile-optimized credential-harvesting pages and discussed session-token theft and replay in those campaigns. Those are specific reported tactics, not an inevitable outcome of scanning a QR code. IC3 advisory AC-000001-MW
Scanning usually decodes data and opens—or offers to open—a destination; it does not by itself mean the phone is infected. Additional risk can arise if someone downloads or installs an app, grants permissions, enters information, or if a vulnerability is exploited. Close a suspicious page and avoid taking further action.
Rank #2

- FAST SPEEDS - Scans color and black and white documents a blazing speed up to 16ppm (1). Color scanning won’t slow you down as the color scan speed is the same as the black and white scan speed.
- ULTRA COMPACT – At less than 1 foot in length and only about 1. 5lbs in weight you can fit this device virtually anywhere (a bag, a purse, even a pocket).
- READY WHENEVER YOU ARE – The DS-640 mobile scanner is powered via an included micro USB 3. 0 cable allowing you to use it even where there is no outlet available. Plug it into you PC or laptop and you are ready to scan.
- WORKS YOUR WAY – Use the Brother free iPrint&Scan desktop app for scanning to multiple “Scan-to” destinations like PC, Network, cloud services, Email and OCR. (2) Supports Windows, Mac and Linux and TWAIN/WIA for PC/ICA for Mac/SANE drivers. (3)
- OPTIMIZE IMAGES AND TEXT – Automatic color detection/adjustment, image rotation (PC only), bleed through prevention/background removal, text enhancement, color drop to enhance scans. Software suite includes document management and OCR software. (4)
Where quishing appears
- Email and attachments: A message may contain an image-only QR code or attach a PDF with instructions to scan using a phone. Common pretexts include voicemail, document sharing, account alerts, VPN access, or a request to “continue securely.” Microsoft reported that PDF attachments accounted for 70% of QR-code attacks in its March 2026 telemetry. Its figures describe Microsoft-observed activity, not worldwide totals. Microsoft’s Q1 2026 threat report
- Text messages: A code may accompany a supposed delivery failure, account-security alert, toll or parking charge, prize, or gift-card offer. The FTC warns that unexpected QR codes in texts and email can lead to spoofed sites or malware. FTC consumer guidance
- Public places: A sticker may cover a legitimate QR code on a parking meter, poster, menu, event sign, or payment point. The FBI has warned that tampered codes can redirect payments or steal funds. IC3 warning on QR-code payment fraud
- Unexpected packages: A package you did not order may include a QR code that asks you to identify yourself, claim a gift, or provide information. The FBI and FTC have warned about this variation; an unsolicited package alone does not establish that a crime occurred, but its QR code is not a reason to share personal or financial details. FBI package alert · FTC package guidance
- Payment and cryptocurrency requests: A fraudulent code can direct money to an attacker-controlled account or wallet. Recovering a payment may be difficult, so verify payment details independently before sending funds.
Warning signs to look for
- The code arrives unexpectedly, or the message creates urgency, fear, or pressure to act immediately.
- A work email tells you to use your personal phone to sign in, verify your identity, or approve access.
- The sender, package, payment request, or supposed account problem is unfamiliar or does not match an action you initiated.
- A sticker appears to cover a code on a meter or sign, or the printed code looks altered.
- The destination uses a misspelled or unrelated domain, an unexpected subdomain, or a shortened link you cannot verify.
- The page requests a password, payment details, one-time authentication code, unusual permissions, or an app installation that the task should not require.
A familiar logo or a padlock icon is not proof that a page is legitimate. HTTPS encrypts a connection; it does not verify that the site is honest. A legitimate domain can also be part of a harmful redirect chain, so a domain that looks plausible is a useful clue, not a guarantee.
Free tools Windows power users keep installed
One-click scans. No signup required.
How to check a QR code more safely
- Pause and assess the context. If you were not expecting the code or the requested action makes little sense, do not scan it. For an urgent account issue, open the service’s known app or type its official address yourself.
- Use a scanner that previews the result. If your phone offers to open a link, inspect the destination first. If it opens automatically, close it rather than continuing when the code or context is suspicious.
- Read the full domain. Watch for misspellings, substituted letters, unfamiliar domains, odd subdomains, and URL shorteners. Do not enter sensitive information just because the page appears branded.
- Verify separately. Contact the organization using a phone number, app, or website you obtained independently—not contact details supplied with the suspicious code.
- Do not follow unexpected requests. Do not enter passwords, payment details, or one-time codes, install an app, or grant permissions simply because a QR-linked page asks.
- Inspect physical codes. At a payment point, check for a sticker placed over the original code. When possible, use the venue’s official app or confirm the destination with staff.
QR codes can contain more than URLs, so a tool that only checks web links will not cover every type of encoded content. Nor can a scanner promise that a destination is safe. A preview is one useful check; independent verification is the safer route before signing in or paying. The FTC’s guidance likewise recommends inspecting the URL and contacting the organization through a known legitimate channel.
Rank #3
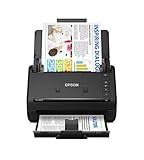
- FAST DOCUMENT SCANNING — Document scanner with feeder allows you to speed through stacks with a 50-sheet Auto Document Feeder (ADF); Efficient office scanner to help you scan more productively
- INTUITIVE, HIGH-SPEED SOFTWARE — Quickly scan with this desktop document scanner; Epson ScanSmart Software lets you easily preview scans, email files, upload to the cloud, and more; Plus, automatic file naming saves even more time
- SEAMLESS INTEGRATION — Easily incorporate your data into most document management software with the included TWAIN driver; Office document scanner integrates seamlessly with business workflows
- EASY SHARING — Duplex scanner allows you to scan straight to email or popular cloud storage2 services like Dropbox, Evernote, Google Drive, and OneDrive for simple storage and sharing
- SIMPLE FILE MANAGEMENT — Scanner allows the creation of searchable PDFs with Optical Character Recognition (OCR) and convert scans to editable Word or Excel files effortlessly; Designed for home and office document scanning
What to do if you scanned a suspicious code
Choose the steps that match what happened. A scan alone is not the same as entering credentials, paying, or installing software.
You scanned it, but entered nothing and installed nothing
- Close the page. Do not download files, approve prompts, or grant permissions.
- Check whether anything was downloaded or installed, and remove anything unfamiliar.
- Keep your phone’s operating system and apps updated. Use its available security scan if appropriate.
- Watch for unusual browser behavior, account sign-ins, or payment activity. If you notice suspicious behavior, take further action based on what changed rather than assuming the scan infected the device.
You entered a password or authentication code
- From a trusted device, change the exposed password immediately. Change it on any other account where you reused it.
- Sign out other sessions if the service offers that control. Review recent sign-ins and account-recovery settings for changes you did not make.
- Enable or reconfigure multifactor authentication (MFA), and contact the service through its known app or website if you cannot secure the account.
- Be alert for follow-up calls, messages, or password-reset prompts related to the incident.
If you entered a one-time code, treat the account as potentially exposed: contact the service promptly and review active sessions. MFA is valuable, but a code or token given to an attacker can be abused in some attacks.
Rank #4

- Scanner type: Document
- Connectivity technology: USB
- With Auto Scan Mode, the scanner automatically detects what you're scanning
- Digitize documents and images
You entered banking or payment details or sent money
- Contact your bank, card issuer, or payment provider immediately using its official number or app. Ask about stopping or disputing transactions, monitoring the account, and replacing compromised credentials or cards.
- Review statements and account alerts, and report unauthorized transactions promptly.
- Report the incident to the relevant authorities. In the United States, the FTC accepts consumer fraud reports, and the FBI’s Internet Crime Complaint Center (IC3) accepts cybercrime complaints.
The FBI has warned that money sent through a malicious QR-code payment scheme may be difficult or impossible to recover, which is why contacting the provider quickly matters. FBI guidance
You installed an app or granted permissions
- Uninstall the suspicious app and review your device’s permissions for anything you did not intend to allow.
- Update the operating system and run a reputable mobile-security scan. If suspicious behavior continues, seek device-specific support; a reset may be appropriate in some cases but is not a universal first step.
- Change important passwords from a separate trusted device, especially if you used them after installing the app.
How organizations can reduce quishing risk
Awareness training helps, but quishing needs controls across email, identity, and mobile devices. Email filtering alone cannot catch a sticker placed on a parking meter, and a phone may sit outside an organization’s management. Match defenses to where the code arrives and where employees scan it.
Best Value

- OUR MOST ADVANCED SCANSNAP. Large touchscreen, fast 45ppm double-sided scanning, 100-sheet document feeder, Wi-Fi and USB connectivity, automatic optimizations, and support for cloud services. Upgraded replacement for the discontinued iX1600
- CUSTOMIZABLE. SHARABLE. Select personalized profiles from the touchscreen. Send to PC, Mac, mobile devices, and clouds. QUICK MENU lets you quickly scan-drag-drop to your favorite computer apps
- STABLE WIRELESS OR USB CONNECTION. Built-in Wi-Fi 6 for the fastest and most secure scanning. Connect to smart devices or cloud services without a computer. USB-C connection also available
- PHOTO AND DOCUMENT ORGANIZATION MADE EFFORTLESS. Easily manage, edit, and use scanned data from documents, receipts, photos, and business cards. Automatically optimize, name, and sort files
- AVOIDS PAPER JAMS AND DAMAGE. Features a brake roller system to feed paper smoothly, a multi-feed sensor that detects pages stuck together, and skew detection to prevent paper damage and data loss
- Email and collaboration: Use tools that can detect QR images in message bodies and attachments, extract and analyze their destinations, inspect redirect chains in a controlled environment, and apply time-of-click URL protection. Quarantine suspicious documents and make reporting easy on both desktop and mobile. These controls reduce exposure; they do not guarantee that every malicious code will be detected.
- Identity: Require MFA, preferably phishing-resistant methods such as passkeys or security keys where practical. Use conditional access and device-compliance policies, restrict legacy authentication, monitor unfamiliar devices and risky sign-ins, and require reauthentication for sensitive actions. MFA reduces password-only risk but cannot make every phishing flow harmless: some attacks exploit approvals or stolen sessions and tokens.
- Mobile devices: Where risk warrants it, manage corporate phones, enforce updates and screen locks, restrict installation from unknown sources, separate work and personal data, and use mobile threat defense. Provide a safe way to report codes received on personal devices.
- Processes and people: Teach employees to open known sites directly rather than using QR codes in work-email login prompts. Use QR scenarios in training, adopt a “report, don’t investigate” approach, verify payment or bank-account changes over a second channel, and remove abandoned or unmonitored codes from public signs.
Microsoft says Defender for Office 365 includes protection for malicious links and QR codes in email and collaboration services. That may be relevant to organizations using Microsoft 365, but it is not a guarantee of detection or protection for a personal phone outside the organization’s controls. Microsoft Defender for Office 365
Does MFA stop quishing?
MFA helps protect an account if a password is stolen, so it is still worth enabling. It does not eliminate quishing risk. A person may be tricked into approving a sign-in, sharing a one-time code, or authenticating through a fake page. Some sophisticated attacks can also steal or replay an authenticated session token. The FBI discusses token theft and replay in its specific 2026 Kimsuky advisory; that example illustrates why organizations should combine MFA with phishing-resistant methods, device controls, session monitoring, and staff reporting—not abandon MFA.
Do you need a QR scanner or security product?
For most consumers, a preview-capable phone camera or QR scanner, independent verification, updated software, and MFA are more useful than buying a product solely for QR protection. No scanner can reliably judge every social-engineering request or guarantee that a code is safe.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Organizations may benefit from email-security products that inspect QR codes, attachments, and linked destinations, especially when staff use Microsoft 365 or regularly handle QR-based sign-in prompts. Assess whether the product fits the organization’s email environment, mobile-device controls, identity setup, and capacity to investigate alerts. Physical-code tampering and personal phones outside managed controls still require separate precautions. Avoid treating any product as a complete defense.
Microsoft’s product page lists QR-code and malicious-link protections, but product scope, licensing, and availability can vary. Check the vendor’s current terms and confirm what is already included in your organization’s agreement before buying. Microsoft product details
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

