Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Java teams rely on code quality tools to catch defects earlier, keep large codebases consistent, and reduce the risk of regressions as applications evolve. The right toolset can flag risky patterns, enforce formatting rules, measure test effectiveness, scan dependencies, and make quality checks part of every pull request.
Developers commonly combine several categories of tools rather than depending on a single solution: static analyzers for maintainability issues, formatters for consistent style, test and coverage tools for verification, security scanners for vulnerabilities, and CI/CD integrations to automate enforcement. Choosing the best mix depends on project size, team workflow, compliance needs, and how much friction the team is willing to accept during development.
Why Java Code Quality Tools Matter
Java projects tend to live for a long time, grow across many packages, and pass through the hands of mulle developers. Without automated quality checks, small inconsistencies accumulate: unused code stays in place, null handling becomes unpredictable, tests drift away from real behavior, and dependency risks go unnoticed. Code quality tools give teams a repeatable way to catch these issues before they reach production or become expensive to untangle.
The main value is not simply finding mistakes. Good tools create a shared baseline for how code should be written, reviewed, tested, and released. A formatter removes debates about indentation and line wrapping. Static analysis flags common bugs such as resource leaks, suspicious equality checks, overly broad exceptions, and unsafe concurrency patterns. Test and coverage tools show whether critical paths are protected. Security scanners highlight vulnerable libraries before they are bundled into an application.
#1 Best Overall

- 【Diagnose Check Engine Light in Seconds – No Mechanic Needed】The FOXWELL NT301 OBD2 scanner instantly reads & clears engine fault codes (DTCs) with one click. Simply plug into the 16-pin DLC port, turn ignition on, and get accurate results within seconds—No prior car knowledge required. Save hundreds on dealership fees by knowing exactly what’s wrong before you visit a shop. The #1 choice car scanner for DIYers and car owners who want to take control of their vehicle’s health
- 【Clear & Reset CEL with Confidence】Unlike cheap code readers that just erase codes temporarily, NT301 works like all professional vehicle code readers: It clears the check engine light only after you’ve fixed the underlying issue. If the problem isn’t fully repaired, the fault code will reappear. So you’ll never get a false pass. Use the foxwell scanner to verify your repair work and drive with peace of mind
- 【Sm-og Check Helper – Know Your Pass/Fail Status Before the Test】With dedicated one-click I/M readiness hotkeys and a simple Red-Yellow-Green LED indicator, you’ll instantly know if your vehicle is ready for annual testing. Built-in speaker provides clear audio feedback. No guesswork—just confidence before you head to the test center. One less thing to worry about when inspection day comes
- 【Advanced OBDII Modes – O- 2 Sensor & EVAP Testing】NT301 go beyond basic code reading with enhanced OBD2 modes. Run an EVAP system check to assess fuel tank condition, and use the O- 2 sensor test to optimize air-fuel ratio, boosting fuel economy, cutting em- issions, and saving you money at the pump. The code reader for cars and trucks is like having a mini em-issions lab in your glove box
- 【Live Data Graphing – Spot Engine Issues in Real Time】View and log live sensor data in easy-to-read graphs with this OBD2 scanner diagnostic tool. Monitor ox- ygen sensors, fuel trims, coolant temperature, RPM, and more to spot suspicious values instantly. This obd scanner gives you professional-grade insight without the pro price tag—a feature you won’t find on basic $20 car code readers
Where quality tools help most
- Code reviews: Reviewers can focus on design, maintainability, and business behavior instead of pointing out style issues or basic defects.
- Large codebases: Automated checks make it easier to keep standards consistent across modules, services, and teams.
- Onboarding: New developers get fast feedback from tools rather than learning conventions only through review comments.
- Refactoring: Coverage reports, mutation tests, and static analysis reduce the risk of changing legacy code.
- Release confidence: CI checks prevent known quality, test, and security problems from moving further down the pipeline.
Java’s ecosystem makes this especially practical because most tools integrate directly with Maven, Gradle, IDEs, and CI systems. A developer can see warnings in IntelliJ IDEA or Eclipse, run the same checks locally with a build command, and rely on GitHub Actions, GitLab CI, Jenkins, or another pipeline to enforce the rules on every pull request. This consistency matters: if the checks in CI differ from what developers see locally, quality gates quickly become frustrating instead of useful.
Another benefit is that tools make quality measurable. Metrics such as test coverage, duplicate code, complexity, vulnerability counts, and rule violations are not perfect on their own, but they help teams spot trends. A service that steadily gains complexity and loses coverage is signaling future maintenance trouble. A dependency scan that starts failing after a new CVE is published gives teams a concrete task: upgrade, patch, replace, or document the risk.
The strongest teams usually avoid treating tools as a one-time setup. They tune rules for the project, suppress findings only when there is a clear reason, and keep feedback fast enough that developers can act on it during normal work. Used this way, Java code quality tools become part of the engineering workflow rather than a separate audit step. They support cleaner code, safer releases, and fewer surprises as the application evolves.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Static Analysis Tools Developers Recommend
Static analysis tools inspect Java source code or bytecode without running the application. Developers use them to catch defects early, enforce maintainability rules, reduce risky patterns, and keep large codebases consistent across teams. In practice, most Java teams combine a broad analysis platform with one or two specialized tools rather than relying on a single scanner.
Infer
Infer is an open-source static analyzer for Java and several other languages. Its Java analysis can identify issues such as resource leaks, null pointer errors, and concurrency problems without running the application.
Infer can be run from the command line as part of a Java build workflow. It is a useful fit for teams looking for focused static analysis of potential defects and concurrency issues alongside broader source checks.
SpotBugs
SpotBugs is the successor to FindBugs and focuses on detecting likely defects in compiled Java bytecode. It is good at finding null pointer risks, bad equality checks, concurrency mistakes, resource leaks, serialization problems, and incorrect API usage. Because it analyzes bytecode, it can catch issues that are not obvious from formatting or style checks alone.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Teams commonly add SpotBugs to Maven or Gradle builds and run it in CI on every pull request. It is lightweight enough for regular use, but its findings may require some tuning. Many teams start with a baseline, suppress legacy warnings, and then fail the build only for new high-confidence issues. Plugins such as FindSecBugs extend SpotBugs with security-focused rules for injection risks, weak cryptography, unsafe deserialization, and web application vulnerabilities.
PMD
PMD analyzes Java source code and is often used to enforce maintainability rules. It can detect unused variables, overly complex methods, empty catch blocks, duplicated branches, poor naming choices, and fragile coding patterns. While SpotBugs is more defect-oriented, PMD is often stronger for style-adjacent design problems and code cleanliness.
PMD is useful for teams that want custom rules. For example, an organization can discourage direct use of certain APIs, require project-specific naming patterns, or flag architectural violations. It also includes CPD, a copy-paste detector that helps identify duplicated code across modules. In mature Java codebases, PMD is usually configured with a curated ruleset rather than the full default set, which helps avoid noisy reports.
Checkstyle
Checkstyle focuses on coding standards rather than deep defect detection. It verifies naming conventions, imports, indentation, brace placement, Javadoc rules, line length, and other structural style concerns. Developers commonly use it when consistency matters across many contributors, such as enterprise teams, libraries, and open-source projects.
Recommended Free Tools
Rank #2
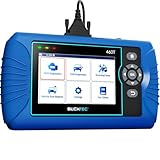
- [All System Diagnostics, Professional-Level Scanner] - BLCKTEC 460T is the ultimate OBD2 diagnostic tool for home mechanics and professionals. It supports all 10 OBD2 modes, reads and clears Engine/Transmission/ABS/SRS codes, performs All-System Diagnostics, offers workshop reset tools, and provides real-time live data. It helps you pinpoint issues, assess your car's condition, and prepare for SMOG checks with ease. NOTE: Function availability depends on your vehicle. Before you buy, be sure to use the Compatibility Checker on BLCKTEC website or contact our customer support to verify that the features you need are supported for your vehicle’s specific year, make, and model.
- [12+ Most Popular Reset Functions] - BLCKTEC 460T OBD2 scanner offers 12+ dealer-level service functions, including Oil Maintenance Reset, ABS Bleeding, EPB Reset, SAS(Steering Angle Sensor) Recalibration, DPF(Diesel Particulate Filter) Reset, Throttle Body Relearn, Battery Reset/Initialization, TPMS Relearn, Transmission Reset, Fluid Change Reset, Maintenance Reset and more, enabling you to perform workshop services like a pro. NOTE: Function availability depends on your vehicle. Be sure to use the Compatibility Checker on BLCKTEC website to verify that the features you need are supported for your vehicle.
- [Real-Time OBD2 and OEM Live Data, Freeze Frame Data] - BLCKTEC 460T helps diagnose vehicle issues when warning lights like Check Engine Light or ABS/SRS Light appear. It offers detailed DTC info, ECU Freeze Frame Data, and real-time OBD2 and advanced OEM live data, including Engine, Transmission, ABS, SRS, and more, making it easy to diagnose and resolve vehicle problems. You can view, graph, record, replay, and overlay up to four live data streams in a single graph for better analysis.
- [AutoVIN, AutoReLink, AutoScan, 3X Faster] - Equipped with AutoVIN technology, 460T automatically retrieves the VIN to save you time. Its AutoScan and AutoReLink features scan all of the vehicle's ECUs and detect any fault codes immediately after you plug the scanner into the vehicle's OBD2 port - no button presses required. Additionally, it regathers DTC and I/M readiness information every 30 seconds, simplifying monitor tests. 460T's advanced technology makes it 3X faster than other products.
- [Get RepairSolutions2, the #1 Auto Repair App for Free] - When paired with RepairSolutions2(RS2) App, 460T becomes even more powerful. RS2's Verified Fix Database built by master technicians, provides the parts needed for the repair. Additionally, RS2 gives you access to OEM warranty info, maintenance schedules, TSB, and dealership recall info, making car care easier than ever. RS2 is free with no subscription fees and it stores your car scan reports in the cloud, allowing you to access, share, or print them anytime and anywhere.
Checkstyle is effective when paired with a shared configuration, such as Google Java Style or a company-specific ruleset. It can run locally in an IDE, during Maven or Gradle builds, and in CI. Because Checkstyle can be strict, teams usually document the expected style and provide auto-formatting support where possible, so developers are not forced to fix every whitespace or import issue manually.
Error Prone
Error Prone, developed by Google, plugs into the Java compiler and catches common programming mistakes during compilation. It flags issues such as incorrect string comparisons, misuse of optionals, broken equals implementations, ignored return values, unsafe collection operations, and problematic concurrency patterns. Its compiler-level feedback makes it attractive for teams that want fast, developer-friendly detection before code even reaches a full CI scan.
A practical stack might use Error Prone for compile-time bug patterns, Checkstyle for coding standards, and SpotBugs or PMD for deeper analysis. The best setup is the one developers will actually run consistently: start with high-signal rules, integrate them into the normal build, suppress legacy noise, and tighten enforcement as the codebase improves.
Code Formatting and Style Enforcement
Formatting tools solve a different problem than static analyzers: they remove debate. A team can have excellent Java code and still waste time on indentation, import order, line wrapping, brace placement, and inconsistent naming conventions. Style enforcement makes code reviews more focused by turning subjective formatting preferences into automated checks. For Java teams, the most commonly recommended tools are Spotless, Checkstyle, and IDE-level formatters such as IntelliJ IDEA code style or the Eclipse formatter.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchSpotless is often the easiest way to standardize formatting in Maven or Gradle builds. It can apply Google Java Format, Palantir Java Format, Eclipse formatter rules, license headers, import ordering, and whitespace cleanup. Developers like it because it can both detect and fix problems, usually through commands such as spotlessCheck and spotlessApply. In a Gradle-based project, teams commonly run Spotless locally before committing and enforce spotlessCheck in CI so unformatted code cannot be merged.
Google Java Format is a strong choice when a team wants a formatter with very few knobs. It applies a consistent style and avoids long configuration discussions. The tradeoff is limited customization: if your organization has a deeply established house style, Google Java Format may feel too rigid. Palantir Java Format is another opinionated option, popular in some enterprise Java teams that prefer its wrapping and readability choices for large codebases.
Checkstyle for style rules beyond formatting
Checkstyle is best used for rules that a formatter does not fully cover. It can enforce package naming, class naming, Javadoc requirements, maximum line length, import restrictions, modifier order, method length, and other style conventions. Many teams start with a known ruleset, such as Google Checks or Sun Checks, then adjust it to match their project. Checkstyle is especially useful in libraries, SDKs, and shared platforms where public API consistency matters.
- Use Spotless when you want automatic formatting and easy build integration.
- Use Google Java Format when you want a strict, low-configuration style.
- Use Checkstyle when you need enforceable naming, structure, import, or documentation rules.
- Use IDE format settings to make the developer workflow smooth, but avoid relying on IDE settings alone.
For day-to-day development, the best setup is usually a layered one. The IDE formats code on save, Spotless or another formatter verifies the result in the build, and Checkstyle catches style violations that formatting cannot fix. This prevents “works on my machine” formatting drift, especially when contributors use different editors or operating systems. Teams should also commit shared configuration files, such as checkstyle.xml, Eclipse formatter profiles, or IntelliJ code style settings, so the rules are visible and versioned with the code.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Be careful not to over-enforce style at the expense of productivity. Rules such as mandatory Javadoc on every private method, very low maximum line lengths, or aggressive method-size limits can create noise if they do not match how the team actually works. A practical approach is to begin with formatting, import order, naming, and a few high-signal structural checks. Once those are stable, add stricter rules only where they improve readability or maintainability. The goal is not to make every file look ceremonial; it is to make Java code consistent enough that developers can read, review, and modify it without being distracted by avoidable style differences.
Testing, Coverage, and Mutation Testing Tools
Static analysis and formatting catch many issues before code runs, but Java teams still rely on test-focused tools to prove behavior. The usual stack starts with a test framework, adds coverage reporting, and then uses mutation testing when the team wants to measure whether tests are genuinely strong rather than merely numerous. These tools are commonly wired into Maven or Gradle so developers get fast feedback locally and the same checks run in CI.
JUnit, TestNG, Mockito, and AssertJ
JUnit 5 is the default choice for most modern Java projects. It supports unit tests, parameterized tests, nested test classes, lifecycle hooks, and extensions for frameworks such as Spring Boot. Teams typically use it for fast, isolated tests around services, utilities, validators, and domain code. TestNG still appears in enterprise and automation-heavy projects, especially where teams value flexible test grouping, ordering, and suite configuration.
Rank #3
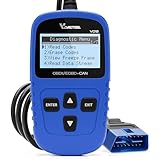
- 【A MUST-HAVE TOOL FOR DIYERS】 - VDIAGTOOL VD10 car code reader is an incredibly useful obd scanner for each car owner or hobbyist, even for those with little to no experience when it comes to vehicle mechanics! Similar to a fixd car diagnostic tool, using this car diagnostic scanner is extremely easy. All you have to do is attach it to your car OBDII port and you can diagnose car problems in seconds! Read Codes (DTCs); Clear Codes; Live Data; View Freeze Frame; I/M Readiness; Vehicle Information.
- 【KEEP ENGINE IN GOOD STATUS】 - VDIAGTOOL check engine code reader brings a fast access to scan, read the car fault code, show its definition on the screen instantly, troubleshooting to find the root causes of problems, erase the engine fault code and turn off the MIL (Malfunction Indicator Light). Similar to a fixd car diagnostic tool, this car code reader helps ensure your engine stays in top condition.
- 【READ/CLEAR CODES & DTC LOOKUP】- No search online & saving your time, this vehicle car code reader retrieves generic (P0, P2, P3, and U0), manufacturer specific (P1, P3, and U1) codes, pending codes and displays DTC definitions based on the built-in database(more than 3000 codes) on the TFT screen, find out the root causes and clear the codes after fixed.
- 【LIVE DATA & RETRIEVE FREEZE FRAME】 - This diagnostic scan tool for accurate diagnosis enables you to retrieve data from vehicle sensors, such as Engine RPM, Intake air temperature, Short/Long term fuel, Misfire data and etc. The freeze frame is stored in the PCM together with the diagnostic trouble code (DTC) related to the fault. Comparable to a fixd car diagnostic tool, the VD10 car code reader car scanner can be a valuable & practical diagnostic aid and also greatly help when diagnosing intermittent problems.
- 【I/M READINESS for THE S-nn-0-g CHECK】- OBDII vehicle may not pass the annual inspection unless the required monitors since reset are complete. So you should at least read the readiness monitors and make sure they are ready. This car obd2 scanner diagnostic tool is equipped with I/M readiness function to check the operations of the e-m-issi0n system on OBD2 compliant vehicles, run I/M monitor readiness test, checking if the pass vehicle s-m-0-g inspection.
For mocking and readable assertions, developers often pair JUnit with Mockito and AssertJ. Mockito is used to replace collaborators such as repositories, HTTP clients, message publishers, or feature-flag services, making unit tests deterministic and quick. AssertJ improves readability with fluent assertions such as checking collection contents, exception details, object fields, and date values. In Spring projects, Spring Boot Test is frequently added for slice tests, integration tests, and application-context checks.
Free tools Windows power users keep installed
One-click scans. No signup required.
JaCoCo for Code Coverage
JaCoCo is a widely used Java coverage tool. It reports line, branch, method, and class coverage, and integrates with Maven, Gradle, Jenkins, GitHub Actions, and GitLab CI. Teams use JaCoCo to identify untested areas and to prevent coverage from dropping below an agreed threshold. For example, a service team might require 80% line coverage overall and a stricter branch coverage target for payment, billing, or authorization code.
Coverage numbers should be treated as a signal, not a guarantee. A test can execute a line without verifying the result, and high coverage can still miss edge cases. The strongest use of JaCoCo is to reveal blind spots: exception paths, null handling, validation branches, mapper , and rarely used configuration paths. Many teams publish coverage reports as CI artifacts and combine them with pull request comments so reviewers can see whether new code includes meaningful tests.
PIT for Mutation Testing
PIT, often called PITest, is the leading mutation testing tool in the Java ecosystem. It deliberately changes production code in small ways, such as replacing a conditional, changing a return value, or altering arithmetic, then runs the test suite to see whether the tests fail. If the tests still pass, the mutation survived, which suggests the tests may not assert behavior strongly enough.
Mutation testing is more expensive than regular unit testing, so teams usually run PIT selectively. A common pattern is to use it on core business modules, libraries, pricing engines, permission checks, and other code where subtle defects are costly. It can run nightly, before releases, or only on changed modules. PIT works well with JUnit and Maven or Gradle, and its reports help developers improve weak tests by adding precise assertions, boundary cases, and negative scenarios.
| Tool | Best for | Typical use |
|---|---|---|
| JUnit 5 | Unit and integration test structure | Run on every build and pull request |
| Mockito | Mocking dependencies | Isolate services from databases, APIs, and queues |
| AssertJ | Readable assertions | Make test failures easier to understand |
| JaCoCo | Coverage reporting | Track untested lines and branches in CI |
| PIT | Test strength measurement | Validate critical modules with mutation testing |
A practical Java testing stack for many teams is JUnit 5, Mockito, AssertJ, JaCoCo, and optional PIT for high-risk areas. This combination keeps everyday feedback fast while still giving senior developers a way to challenge the quality of the test suite where correctness matters most.
Security and Dependency Scanning Tools
Java applications often rely on dozens or hundreds of third-party libraries, from Spring Boot starters and JSON parsers to database drivers and logging frameworks. Security and dependency scanning tools help teams detect vulnerable packages, unsafe code patterns, exposed secrets, and risky transitive dependencies before they reach production. Developers commonly add these tools alongside static analysis and test coverage checks because a build can be well-tested and neatly formatted while still shipping a known CVE.
OWASP Dependency-Check
OWASP Dependency-Check is a widely used open-source scanner for identifying dependencies with known vulnerabilities. It analyzes Maven, Gradle, JAR, WAR, and other project artifacts, then matches detected components against public vulnerability data sources such as the National Vulnerability Database. Java teams often run it in CI to fail builds when a dependency crosses a configured CVSS threshold.
Dependency-Check is especially useful for teams that want a vendor-neutral scanner they can run locally, in CI, or as part of a scheduled audit. It works well for Maven and Gradle projects, but teams should expect some tuning. False positives can occur when package metadata is ambiguous, so suppression files are commonly used to document accepted findings or incorrect matches.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsDependabot and Renovate
Dependabot and Renovate focus on keeping dependencies current by opening automated pull requests. Dependabot is integrated with GitHub and is simple to enable for Maven and Gradle repositories. Renovate supports a broader range of configuration options and is popular with teams that need grouped updates, custom schedules, monorepo support, or advanced versioning rules.
These tools are most effective when paired with a strong test suite and CI pipeline. For example, a Spring Boot service might receive a pull request that updates Logback, Jackson, or Netty, then automatically run unit tests, integration tests, SpotBugs, Checkstyle, and container image scans. If the pipeline passes, the team can merge dependency updates quickly instead of letting security patches accumulate for months.
Rank #4

- Your Car's Personal Doctor: Say Goodbye to Check Engine Light Troubles! The YM319 OBD2 scanner swiftly reads and clears engine fault codes, pinpointing the root cause of issues. Monitor your engine's every "breath" like a pro—view freeze frame data, check I/M readiness status, run oxygen sensor tests, and more. With a built-in database of over 63,000 fault codes, it delivers precise and reliable diagnostics, making it your trusted partner for vehicle maintenance and repair.
- One-Click Battery Health Check: Our exclusive one-click BAT battery diagnostic feature continuously monitors voltage and health status, visualizing potential risks to prevent unexpected failures. This car code reader is your guarantee for worry-free travel and driving safety. Additionally, the OBD2 code reader for cars and trucks offers advanced diagnostics, including testing of O2 sensors and EVAP systems, precisely pinpointing the root causes of abnormal fuel consumption and emission faults.
- Live Data & Cloud Printing: This OBD2 scanner diagnostic tool not only reads data instantly but also continuously records and plots data curves, effortlessly capturing intermittent faults. Its innovative cloud printing feature lets you generate, store, or share detailed professional diagnostic reports—no printer connection required. Conveniently save maintenance records or efficiently communicate with technicians remotely, ensuring all vehicle maintenance decisions are backed by solid evidence.
- Smooth and Efficient Operation: Simply plug in and play—no batteries required. Meticulously designed to enhance diagnostic efficiency. The scanner for car features a 2.4" HD color screen with 10 brightness levels, ensuring clear readability in any environment. Red, green, and yellow indicator lights enable instant vehicle status assessment. The unique F1 and F2 customizable shortcut keys place frequently used functions like code reading and clearing at your fingertips, enabling one-touch access and significantly saving your valuable time.
- Wide Vehicle Compatibility & Multi-Language Support: This OBD2 car scanner diagnostic tool supports all OBDII protocols, including KWP2000, J1850 VPW, ISO9141, J1850 PWM, and CAN protocols. Works with most 1996 and newer US cars, 2000 EU and Asian cars, light trucks, SUVs, and newer OBD2 and CAN vehicles both at home and abroad. Tips: The scanner for car is not compatible with new energy vehicles and hybrid vehicles. This car error code reader supports 13 languages including English, German, French, Spanish, Russian, Portuguese and Chinese, making it an ideal choice for international users.
Snyk, GitHub Advanced Security, and commercial scanners
Snyk is commonly recommended for developer-friendly vulnerability scanning across open-source dependencies, container images, infrastructure files, and source code. It provides remediation advice, fix pull requests, license checks, and IDE integrations. Many teams use it because it gives developers direct feedback while still producing security reports that platform and compliance teams can review.
GitHub Advanced Security adds code scanning, secret scanning, and dependency insights inside GitHub repositories. For Java projects, it can run CodeQL analysis to detect vulnerability patterns such as injection risks, insecure deserialization flows, and unsafe data handling. Secret scanning is also valuable for catching leaked API keys, tokens, and cloud credentials before they spread through repository history.
Common Java security scanning stack
- Dependency scanning: OWASP Dependency-Check, Snyk, Dependabot, Renovate, or GitHub dependency alerts.
- Code security analysis: CodeQL, Semgrep, or SpotBugs with Find Security Bugs.
- Secret detection: GitHub secret scanning, Gitleaks, TruffleHog, or platform-native repository scanners.
- Container scanning: Trivy, Snyk Container, Grype, or cloud registry scanners for Java services packaged as Docker images.
A practical setup for many Java teams is to combine automated dependency update pull requests with one vulnerability scanner and one secret scanner. Larger organizations may add CodeQL or Semgrep for source-level security analysis and Trivy or Grype for container images. The goal is not to run every scanner available, but to create a workflow where developers see clear findings, receive actionable fixes, and can distinguish urgent vulnerabilities from low-risk noise.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Integrating Code Quality Checks into CI/CD
Code quality tools deliver the most value when they run automatically in the same pipeline that builds, tests, and ships the application. Instead of relying on developers to remember local commands, CI/CD integration makes checks repeatable and visible on every pull request. For Java teams, this usually means wiring Maven or Gradle tasks into GitHub Actions, GitLab CI, Jenkins, CircleCI, Azure Pipelines, or another build runner so that style, static analysis, tests, coverage, and security scans happen before code is merged.
A practical pipeline starts with fast feedback. Formatting checks, Checkstyle, PMD, SpotBugs, and unit tests should run early because they catch common issues quickly. Longer-running tasks, such as integration tests, mutation testing with PIT, container scans, or full dependency analysis, can run later in the pipeline or on scheduled builds. This keeps pull requests responsive while still giving the team deeper quality signals before release.
Common CI quality gates for Java projects
- Compilation: Run mvn verify or gradle build to confirm that the project compiles cleanly and all required checks are bound to the build lifecycle.
- Formatting and style: Use Spotless, google-java-format, Checkstyle, or similar tools to prevent inconsistent style from reaching the main branch.
- Static analysis: Run SpotBugs, PMD, or Error Prone to catch bug patterns, risky constructs, complexity issues, and maintainability problems.
- Automated tests: Execute JUnit and TestNG suites, often with Mockito, AssertJ, Testcontainers, or Spring test support depending on the project.
- Coverage thresholds: Generate JaCoCo reports and fail the build if coverage drops below agreed limits for lines, branches, or changed code.
- Security scanning: Check dependencies and containers with tools such as OWASP Dependency-Check, Snyk, GitHub Dependabot, Trivy, or enterprise SCA platforms.
Many teams separate checks into pull request gates and main-branch gates. Pull request gates focus on what developers need to fix before review: formatting, static analysis, unit tests, and targeted dependency scans. Main-branch gates can add heavier tasks such as full integration test suites, mutation testing, API compatibility checks, performance smoke tests, and deployment readiness scans. This split avoids making every small change wait for the slowest quality task while still protecting production builds.
| Pipeline stage | Typical tools | When to fail the build |
|---|---|---|
| Pre-merge validation | Spotless, Checkstyle, SpotBugs, JUnit, JaCoCo | Formatting violations, failed tests, new critical findings, coverage below threshold |
| Main branch verification | PIT, Testcontainers, OWASP Dependency-Check | Mutation score below target, vulnerable dependency above severity policy |
| Release pipeline | Snyk, Trivy, SBOM generators, signing and provenance tools | Known exploitable vulnerabilities, unsigned artifacts, failed container policy checks |
To reduce noise, teams should treat quality rules as versioned project configuration rather than ad hoc CI settings. Maven plugins, Gradle plugins, Checkstyle rules, SpotBugs exclusions, and JaCoCo thresholds should live in source control where possible. Baselines are useful for legacy codebases: existing issues can be recorded while the pipeline blocks only new violations. Over time, the team can tighten thresholds, remove suppressions, and move from advisory warnings to enforced build failures.
The best CI setup is strict enough to protect the codebase but predictable enough that developers trust it. Pin tool versions, cache Maven or Gradle dependencies, publish readable reports as build artifacts, and surface annotations directly on pull requests when the platform supports it. When a check fails, the developer should see the file, line, rule, and remediation path without digging through thousands of log lines. That feedback loop is what turns code quality tooling from a periodic audit into an everyday engineering habit.
How to Choose the Right Toolset for Your Team
Choosing Java code quality tools is less about finding the longest checklist and more about building a stack your team will actually run, maintain, and trust. A small Spring Boot service, a regulated financial platform, and a legacy monolith do not need the same setup. Start by identifying the risks that matter most: production defects, inconsistent style, slow reviews, vulnerable dependencies, low test confidence, or maintainability problems in older code.
A practical baseline for many Java teams includes a formatter, a static analyzer, a test coverage tool, a dependency scanner, and CI enforcement. For example, a common Maven or Gradle setup might combine Spotless or google-java-format for formatting, Checkstyle or PMD for style and maintainability rules, SpotBugs for defect detection, JaCoCo for coverage, and OWASP Dependency-Check or Snyk for dependency scanning. Teams using GitHub, GitLab, Jenkins, or Azure DevOps can then run these checks on every pull request.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesMatch tools to team maturity and project constraints
For a new project, it is usually best to enable stricter rules early because there is little historical code to clean up. For an older codebase, avoid turning on hundreds of rules at once and failing every build immediately. Instead, set a baseline, block only new violations, and schedule cleanup for high-value issues such as null pointer risks, resource leaks, insecure dependencies, and untested critical paths. This keeps progress visible without overwhelming developers.
Best Value

- 【2-IN-1 WIRED & BLUETOOTH OBD2 SCANNER】Get the reliability of a wired code reader and the convenience of Bluetooth app diagnostics in one compact tool. The ANCEL BD310 lets you read and clear check engine codes directly on the device or access advanced app features from your phone, including battery monitoring, smart driving insights, and live vehicle data. Designed for DIY drivers who want more than a basic scanner without stepping up to a professional tablet
- 【UNDERSTAND CHECK ENGINE LIGHTS BEFORE PAYING FOR REPAIRS】Stop guessing why your warning light is on. Read engine trouble codes, view plain-English DTC explanations, and use built-in Google Search support to learn possible causes and fixes before visiting a repair shop. Clear codes after repairs, verify the issue is resolved, and avoid unnecessary diagnostic fees and surprise repair costs
- 【MONITOR BATTERY HEALTH & VEHICLE PERFORMANCE】Track battery voltage in real time and spot charging system problems before they leave you stranded. The free app also includes battery testing, performance testing, and trip analysis tools that help you monitor driving behavior, coolant temperature, acceleration, braking, and overall vehicle health over time
- 【PASS SMOG CHECKS & EMISSIONS TESTS WITH CONFIDENCE】Run I/M Readiness checks at home before inspection day and avoid wasted trips to the testing station. Verify emissions monitor status, confirm O₂ sensor readiness, detect EVAP-related issues, and check whether your vehicle is ready for state emissions testing. A practical OBD2 scanner for routine maintenance, road trips, and everyday vehicle health checks
- 【SMART HUD DISPLAY & LIVE DRIVING DATA】Use HUD mode to display real-time speed, RPM, voltage, and other key vehicle data directly on your windshield or phone screen while driving. Customize dashboard layouts, monitor live performance data, and keep important vehicle information within view for a smarter and more connected driving experience
| Team need | Useful tools | Good first policy |
|---|---|---|
| Consistent formatting | Spotless, google-java-format, Checkstyle | Auto-format locally and verify in CI |
| Bug detection | SpotBugs, Error Prone, PMD | Fail builds on high-confidence defects |
| Coverage visibility | JaCoCo | Track changed-code coverage before global thresholds |
| Security scanning | OWASP Dependency-Check, Snyk, Dependabot | Block critical and exploitable vulnerabilities |
| Central reporting | Qodana | Publish pull request annotations and trends |
Keep the stack small enough to understand
Overlapping tools can create duplicate findings and noisy pull requests. Decide which tool owns each rule. If developers see three comments for the same naming problem or nullability warning, they will start ignoring the tooling. Assign each tool a clear job: formatter handles layout, static analyzer catches defects, coverage tool measures tests, dependency scanner watches third-party risk, and CI decides whether the change is mergeable.
Developer experience should be part of the selection process. Prefer tools that integrate with your build system, IDEs, and pull request workflow. A formatter that runs automatically in IntelliJ IDEA, Eclipse, VS Code, Maven, Gradle, and CI will be adopted faster than one requiring manual commands. Similarly, rules should be documented in the repository, not hidden in a build server. When a check fails, developers should know the rule, the file, the fix, and whether suppression is allowed.
- Use Maven or Gradle plugins so checks run the same way locally and in CI.
- Start with high-signal rules before adding opinionated or low-confidence checks.
- Review thresholds quarterly as the codebase and team practices improve.
- Make exceptions explicit with documented suppressions, not silent bypasses.
- Measure outcomes such as fewer review comments, faster pull requests, and reduced escaped defects.
The right toolset is one that protects the codebase without slowing delivery unnecessarily. Begin with a lean, enforceable setup, tune it using real developer feedback, and expand only when a new tool solves a clear problem. In most teams, consistency and follow-through matter more than having every possible analyzer installed.
Free tools Windows power users keep installed
One-click scans. No signup required.
Frequently Asked Questions
Which Java code quality tools should a new project start with?
For most new Java projects, start with Checkstyle or Spotless for formatting, SpotBugs or Error Prone for static analysis, JaCoCo for coverage, and OWASP Dependency-Check or Snyk for dependency scanning. This gives you a practical baseline without overwhelming the team on day one.
How should teams combine tools like Checkstyle, PMD, and SpotBugs?
Many teams combine tools because they solve different problems. Checkstyle and Spotless are good for fast, deterministic style checks, while SpotBugs, PMD, and Error Prone catch specific bug patterns during development or CI. Keep each tool’s role clear and tune rules to avoid duplicate findings.
What is the difference between code coverage and mutation testing?
Code coverage tools like JaCoCo show which lines, branches, or methods were executed by tests, but they do not prove that the tests catch real defects. Mutation testing tools like PIT change small parts of the code and check whether the test suite fails as expected. Teams often use JaCoCo on every pull request and run mutation testing less frequently because it is more expensive.
How strict should code quality checks be in CI/CD?
Start by failing builds on clear issues such as formatting violations, compilation errors, failing tests, high-severity security findings, and new critical static analysis bugs. For legacy projects, avoid blocking every existing issue immediately; instead, apply stricter rules only to new or changed code. This keeps CI useful without creating a backlog that developers learn to ignore.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Are free Java code quality tools enough for a professional team?
Yes, many professional teams rely heavily on free tools such as Checkstyle, PMD, SpotBugs, JaCoCo, PIT, OWASP Dependency-Check, and Spotless. Hosted tools like Snyk or commercial security scanners can add vulnerability intelligence, pull request comments, and compliance reporting. The right choice depends on team size, security requirements, and how much maintenance you want to handle yourself.
Bottom Line
The best Java code quality stack is usually a combination, not a single tool: use a formatter for consistency, static analysis for maintainability, test and coverage tools for confidence, and security scanners to catch vulnerable dependencies early. Start with developer-friendly defaults such as Checkstyle or Spotless, SpotBugs, PMD, JaCoCo, JUnit, and a dependency scanner, then tighten rules as the team matures.
Your next step is to choose a small baseline set, wire it into the build and CI pipeline, and make the feedback fast enough that developers actually use it. Once the basics are reliable, expand into deeper security, architecture checks, and quality gates that match your project’s risk and release process.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

