Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Install ProFTPD on Ubuntu 24.04 with sudo apt install proftpd-basic, then configure a restricted account, passive-mode ports, and FTP over TLS before exposing the server. Plain FTP does not encrypt passwords or files; if your clients support SFTP and you do not need FTP compatibility, using OpenSSH for SFTP is usually simpler to firewall.
Before you begin: choose FTP, FTPS, or SFTP
ProFTPD serves the FTP protocol. FTP sends credentials and transferred files without encryption. FTPS is FTP protected by TLS; it still uses an FTP control connection and separate data connections, so passive ports and firewall coordination matter. SFTP is a different file-transfer protocol carried over SSH, not FTP over TLS. ProFTPD can also support an SFTP-like SSH service through a separate module, but that is not enabled by installing the standard FTP service.
Use ProFTPD when an existing client or workflow requires FTP or FTPS. If you control both ends and only need secure file transfer, SFTP through OpenSSH is generally easier to operate because it can use the SSH service and avoids FTP’s separate passive data-port range.
Free tools Windows power users keep installed
One-click scans. No signup required.
This guide assumes Ubuntu Server 24.04 LTS, a sudo-capable account, a server hostname or reachable IP address, and access to every firewall between the client and server. Back up the configuration before editing. For a public server, use a DNS name and a certificate issued for that name; a temporary self-signed certificate is useful only for testing.
#1 Best Overall

- COMPLETE M6 RACK SCREWS KIT:Includes 45 square rack cage nuts, 45 rack mounting screws and 45 black washers stored in a plastic storage box for easy organization and quick access
- DURABLE CARBON STEEL WITH BLACK NICKEL PLATING:Rack screws and cage nuts are built of carbon steel with black nickel coating to deliver excellent oxidation, rust, corrosion and wear resistance for long-term use in high and low temperature environments
- PRECISE SHARP THREADS FOR SAFE INSTALLATION:Server rack mounting hardware features deep sharp threads and smooth burr-free surface for secure, safe installation of rack and cabinet equipment
- UNIVERSAL COMPATIBILITY FOR SQUARE-HOLE RACKS:M6 x 16mm rack screws fit standard 10mm square-hole racks and cabinets; ideal for mounting servers, switches, routers and A/V equipment in data centers and workspaces
- TIGHT TOLERANCE MANUFACTURING:Conforms to metric standard with less than 0.01mm average error; compact thread structure ensures tight fit, uniform force distribution and resistance against deformation and slipping
Install ProFTPD from Ubuntu’s repositories
Ubuntu 24.04 (Noble Numbat) offers ProFTPD packages through the configured Ubuntu repositories, including the Universe component. Refresh package indexes and install the standard package:
sudo apt update
sudo apt install proftpd-basic
If APT cannot find that package, inspect the names and candidates available from your enabled repositories rather than downloading an unrelated package or compiling from source:
apt-cache policy proftpd-basic proftpd-core
apt search '^proftpd'
The Noble package metadata lists proftpd-core; package naming and revisions can vary with repository pocket and architecture. The core version shown in the Ubuntu package metadata on August 18, 2026 was 1.3.8.b+dfsg-1ubuntu0.1 for listed architectures, but that is not a timeless version guarantee. Check the current candidate and installed binary with:
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →apt-cache policy proftpd-core
proftpd -vUbuntu’s package-management guidance recommends installing software with APT: Ubuntu Server package management. Package details: Ubuntu Noble proftpd-core and Noble network packages.
Check the service after installation:
systemctl status proftpd --no-pagerDo not assume it is enabled for every installation. Check with systemctl is-enabled proftpd; you can enable it at boot after configuration is ready.
Back up the configuration
The main configuration is commonly /etc/proftpd/proftpd.conf. Confirm the installed layout, then save a restorable copy before changing files:
sudo ls -la /etc/proftpd
sudo cp -a /etc/proftpd /etc/proftpd.backup.$(date +%F-%H%M%S)
If a later edit prevents the service from starting, restore the saved directory or revert the specific change, run sudo proftpd -t, and restart only after the syntax test passes. The Ubuntu documentation package includes sample configurations and material about TLS, NAT, logging, testing, virtual users, and virtual hosts: ProFTPD documentation package file list.
Create a non-root, FTP-only user
ProFTPD normally authenticates against system accounts by default. Create a dedicated user with a non-interactive shell and a home directory under /srv/ftp:
Rank #2

- Pro Grade – Here is our new Black M6 Rack Screws and Cage Nuts Set [25 x Server Rack Screws, 25 x Cage Rack Nuts, 25 x Washers] used for mounting server racks, enclosures, cabinets, and more.
- Strong & Durable – Our Rack Cage Nuts & Relay Rack Screws for server rack have a high-grade carbon steel construction to prevent stripping. The M6 Cage Nuts and Bolts have also been coated in zinc chromate plating for resistance from corrosion.
- Wide application – Our rack screws & nuts are universally compatible with all square hole racks & cabinets. This makes the rack cage nuts and screws suitable for mounting all server rack hardware, including rack server cabinets, server shelves, A/V device enclosures, and other server mounting procedures.
- Easy to install – Our server rack screws and clip nuts have a Phillip’s truss-head with self-guiding pilot points to allow you to install in no time. The rackmount screws and nuts thread are extra sharp, clean & accurate, offering a smooth & satisfying installation process.
- Essential Bundle – Our Cage nuts & screws m6 set includes all the essential parts for mounting your server equipment. Pack not only includes screws & cage nuts; we have also thrown in additional heavy-duty washers to reduce any marks or scratches when installed. We truly believe our server rack nuts and bolts set is the best in the marketplace and we stand by that. If our cage nut set starts driving you nuts, we’ll FULLY REFUND YOU. So, click “Add to Cart” now and buy with confidence.
sudo adduser --home /srv/ftp/alice --shell /usr/sbin/nologin alice
sudo install -d -o alice -g alice -m 0750 /srv/ftp/alice
sudo passwd alice
Verify the account and local write access:
getent passwd alice
sudo -u alice sh -c 'cd ~ && pwd && touch test-upload.txt'
The shell restriction avoids giving this account a normal interactive login shell, but it does not by itself establish the FTP policy or revoke access granted elsewhere. ProFTPD’s RequireValidShell setting determines whether the account’s shell must appear in the system’s valid-shell list. For an FTP-only account using /usr/sbin/nologin, the usual configuration is RequireValidShell off; that applies to ProFTPD login validation and does not grant SSH access.
Do not use FTP root login. A dedicated, least-privilege account is safer, and routine file transfers should not require administrative ownership. ProFTPD’s authentication documentation covers system users, shell validation, virtual users, and root-login risks: ProFTPD authentication how-to.
Configure the control port, home restriction, and passive range
Edit /etc/proftpd/proftpd.conf and ensure the active configuration has settings equivalent to these. Check the existing file first: avoid adding duplicate or conflicting directives if they are already present.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallServerName "Ubuntu ProFTPD Server"
ServerType standalone
DefaultServer on
UseIPv6 on
Port 21
PassivePorts 49152 65534
DefaultRoot ~
RequireValidShell offDefaultRoot ~ confines a logged-in user to the user’s home directory as presented through FTP. It is not a replacement for Unix ownership and permissions, nor a guarantee against every configuration error. Do not enable anonymous FTP as part of a basic server setup.
The example passive range, TCP 49152–65534, is an example rather than a mandatory range. ProFTPD uses ports from the configured range for FTP data connections when needed; it does not keep every port in that range continuously open as a listener. A range that is too narrow may limit concurrent transfers. The PassivePorts directive and DefaultRoot behavior are documented in ProFTPD core directives.
A user’s home directory must be traversable by that user. If you later want the user to upload into a particular folder, grant write access to that folder rather than making a chroot root broadly writable. Some security configurations reject a writable chroot root; a common pattern is a non-writable home root with a separate, user-owned upload subdirectory.
Allow the service through the firewalls
For UFW, allow the FTP control connection and the same passive range configured in ProFTPD:
sudo ufw allow 21/tcp
sudo ufw allow 49152:65534/tcp
sudo ufw status verbose
These host rules are only one layer. A cloud security group or provider firewall must allow matching inbound TCP traffic; a home router must forward the control port and passive range to the server. Where practical, restrict allowed source addresses to trusted networks. Do not open unrelated ports to troubleshoot FTP.
Rank #3

- 【Wide Application】 XOOL M6 Rack Mount Screw Kit is great for mounting your rack server cabinets, server shelves, A/V device enclosures, and more. These M6 cage nuts and screws are universally compatible with all square-hole racks and cabinets. Easily mount your equipment using this convenient kit, which comes with everything you'll need to get the job done. These self-locking cable ties are perfect for computer, appliance and electronic cord organization, wire management and storage.
- 【Superb Quality】 The cage nuts and screws is made of high quality Carbon Steel. The Carbon Steel material features strength and offers good corrosion resistance in bad environment like high temperature, cold weather, and high humidity areas. They have superior rust resistance and the excellent of oxidation resistance, which can ensure long time using and prolong screws and nuts lifespan. Wear resistant feature make the cage nuts and screws more durable and solid.
- 【Standard Metric】 Our M6 screws and cage nuts accord with standardized metric system. And the average error is less than 0.01mm. The screw thread is very sharp, clean and accurate without burr. The compact and force uniform screw thread is not easy to out of shape and slid in the process of rolling and installation. The deep and clear flat cross head can make your working more easily and improve your work efficiency.
- 【Safety and Eco-Friendly】 XOOL M6 screws and cage nuts use high quality Carbon Steel raw material, which is environmental protection and non-poisonous. In the process of using, there are no toxic substances releasing, which will ensure your safety. After heat treating, carbon steel has good mechanical properties of ductility, hardness, yield strength, or impact resistance.
- 【Thoughtful Design】 We add self-locking Nylon cable ties on our package. The CABLE TIES is good for home, office, garage, workshop and more. And the screw is very easy to insert with hand.
Explicit FTPS normally upgrades the connection on port 21, so it does not automatically require port 990. Port 990 is associated with a different implicit-FTPS deployment; only allow it if you deliberately configure that mode.
Enable FTP over TLS
Do not expose plain FTP for real credentials or private data. Install ProFTPD’s crypto module and OpenSSL:
sudo apt install proftpd-mod-crypto opensslThe module package supplies TLS functionality. Ubuntu’s package page lists it at proftpd-mod-crypto; ProFTPD’s documentation discusses authentication and encrypted service configuration at the authentication how-to.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Clear out junk files and repair common Windows errors3Scan for outdated or missing drivers - takes under a minuteUse a trusted certificate for a public server
For public use, obtain and renew a certificate whose names match the DNS name clients use. A self-signed certificate will trigger trust warnings and should not be presented as production-ready. Keep the private key readable only by root and follow the certificate issuer’s renewal process.
Generate a temporary self-signed certificate for testing
If you only need an initial test, create a certificate and key. Clients will not be able to validate it against a public trust chain:
sudo install -d -m 0750 -o root -g root /etc/proftpd/ssl
sudo openssl req -x509 -nodes -newkey rsa:3072 -days 365
  -keyout /etc/proftpd/ssl/proftpd.key
  -out /etc/proftpd/ssl/proftpd.crt
sudo chmod 600 /etc/proftpd/ssl/proftpd.key
sudo chmod 644 /etc/proftpd/ssl/proftpd.crt
Confirm module loading before adding TLS directives
Ubuntu’s installed module and include layout can vary. Inspect the files before adding configuration, rather than assuming a particular tls.conf or adding a duplicate module load:
sudo grep -RniE 'mod_tls|tls.conf|Include' /etc/proftpdIf mod_tls is not loaded, inspect /etc/proftpd/modules.conf and the installed package files to determine the appropriate module-loading line and include location. Then place the TLS directives in the active configuration or an included file:
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
<IfModule mod_tls.c>
    TLSEngine                   on
    TLSLog                      /var/log/proftpd/tls.log

    TLSProtocol                 TLSv1.2 TLSv1.3
    TLSRSACertificateFile       /etc/proftpd/ssl/proftpd.crt
    TLSRSACertificateKeyFile    /etc/proftpd/ssl/proftpd.key

    TLSRequired                 on
    TLSOptions                  NoSessionReuseRequired
</IfModule>
Replace the certificate paths if you installed a trusted certificate elsewhere. Requiring TLS prevents clients from authenticating or transferring without encryption; it also means an ordinary unencrypted FTP client will no longer work. TLS protects traffic only when the client uses and validates the intended certificate correctly.
Rank #4
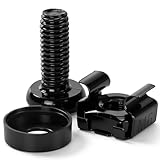
- 【UNIVERSAL 19-INCH RACK COMPATIBILITY】No more ill-fitting hardware! Our M6 x 16mm fasteners fit all standard 19-inch SERVER RACKS, network cabinets and data centers—seamless lock-in, zero size guesswork, no return risks for mismatched parts. Perfect for your rack mount setup
- 【DURABLE BLACK ZINC-PLATED BUILD】Fight mild rust and stripping! Our RACK MOUNT HARDWARE features thick BLACK ZINC PLATING on carbon steel—resists wear, bending and indoor/semi-outdoor corrosion for 2+ years. Sturdier than generic flimsy fasteners
- 【50-PACK ALL-IN-ONE CAGE NUTS KIT】No mid-install part runs! Our complete 50-pack of CAGE NUTS includes matching M6 screws, washers + FREE self-locking cable ties—exact parts for rack/cabinet builds, no extra hardware store trips
- 【TOOL-FREE SNAP-ON EASY INSTALL】Skip complex tools and slow builds! Our RACK MOUNT SCREWS pair with snap-on cage nuts (hand-installed)—twist in with a basic Phillips driver, no stripping. Finish your rack setup in 10-15 mins, even for first-timers
- 【MULTI-USE RACK ACCESSORY HARDWARE】Max out your setup versatility! This hardware works for all NETWORK AND SERVER RACK ACCESSORIES—small business racks, office cabinets, home labs, audio racks. Washers prevent scratches, cable ties tidy wiring
Test the configuration and start the service
Test syntax before restarting. If the build does not find the default configuration automatically, pass its path explicitly:
sudo proftpd -t
# If needed:
sudo proftpd -t -c /etc/proftpd/proftpd.conf
After a successful test, apply the configuration and arrange startup at boot:
sudo systemctl restart proftpd
sudo systemctl enable proftpd
sudo systemctl status proftpd --no-pager
Check the control socket and, while a client is actively transferring, inspect sockets as needed:
sudo ss -ltnp | grep -E ':(21|49152|49153)'Do not expect a permanent listener on every passive port. The passive range is used for data connections when a client requests a transfer. If the service fails after an edit, consult the journal before changing unrelated settings:
sudo journalctl -u proftpd -b -n 100 --no-pagerConnect with an FTPS client
In an FTP client that supports explicit FTP over TLS, use these connection settings:
- Protocol: FTP
- Encryption: require explicit FTP over TLS
- Host: the server’s DNS name or reachable IP address
- Port: 21
- Transfer mode: passive
- Credentials: the system username and password created above
Do not choose SFTP for this listener. SFTP uses SSH and is not the same protocol as FTP with TLS. A client that cannot negotiate explicit FTPS cannot securely use this TLS-required FTP configuration.
After connecting, test a directory listing, download, and upload to the intended writable directory. A successful login alone does not prove that passive data connections, permissions, or encryption are working.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Configure NAT, public addresses, and IPv6
If the server sits behind a router or other NAT device, ProFTPD may otherwise advertise a private address in its passive-mode response. Set MasqueradeAddress to the public DNS name or public IP address that clients can reach:
Best Value

- Accurate & Durable Design:Our M6 screws and cage nuts are manufactured to strict metric standards with an average tolerance of less than 0.01 mm for accurate fit and reliable performance. The threads are sharp, clean, and burr-free, ensuring smooth installation. The compact, evenly distributed thread design resists deformation and slipping during fastening. A deep, well-defined Phillips head allows for easier operation and improved work efficiency.
- Heavy-Duty & Long-Lasting:Constructed from premium carbon steel with a protective black nickel coating to resist rust and oxidation. Designed to withstand high temperatures, cold weather, and other harsh conditions for reliable, long-term performance.
- Clean & Professional Look:Finished in sleek black nickel to match most rack systems, delivering a clean, organized, and professional appearance inside your cabinet.
- Wide Application:Perfect for server cabinets, rack shelves, and A/V enclosures. Compatible with all standard square-hole racks, this M6 cage nut and screw kit provides secure installation hardware along with durable self-locking cable ties for clean and organized wire management.
- 50-Pack Complete Set – Comes with 50 cage nuts, 50 mounting screws, and 50 black washers. Packaged in a sturdy small box to keep everything organized and easy to store.
MasqueradeAddress ftp.example.comThe advertised address, ProFTPD passive range, host firewall, and router or cloud firewall must agree: configure the same passive ports in ProFTPD, allow them on the server, and forward or allow them to that server externally. The official documentation describes MasqueradeAddress for NAT use in mod_core.
If the host has a public IPv6 address or DNS AAAA record, test IPv6 separately. An IPv4 firewall rule does not establish that IPv6 traffic is permitted or correctly routed. A client may choose IPv6 and fail even when IPv4 works.
Troubleshoot by symptom
Cannot connect to the server
- Confirm the service is active with
systemctl status proftpd --no-pager. - Check that TCP 21 is allowed in UFW and in any cloud firewall or router.
- Confirm the client uses the correct address and port, and that the server is reachable from the client’s network.
- If the hostname has both A and AAAA records, test each address family and its firewall path.
- If ProFTPD will not start, run
sudo proftpd -tand inspectsudo journalctl -u proftpd -b -n 100 --no-pager.
Login returns “530 Login incorrect”
Check that the account exists, has a password, and has the intended shell and ProFTPD policy:
Recommended Free Tools
getent passwd alice
grep -Rni RequireValidShell /etc/proftpd
If the account uses /usr/sbin/nologin while shell validation is enabled, configure RequireValidShell off for the FTP service, then retest and restart. This does not itself grant SSH access. Do not “fix” the issue by enabling root login or giving the account broad privileges.
Login works, but listing or transfers hang
This usually points to passive-mode routing or firewall mismatch. Check the active passive range and host firewall:
grep -Rni PassivePorts /etc/proftpd
sudo ufw status numbered
sudo ss -ltnp
Ensure the configured range is allowed by UFW and any provider firewall, and forwarded by the router if the server is behind NAT. For NAT, confirm the server advertises the public address through MasqueradeAddress, not its private address.
Login works, but upload fails
Inspect every directory component’s permissions and test write access as the FTP account:
namei -l /srv/ftp/alice
sudo -u alice test -w /srv/ftp/alice && echo writable
If that directory is intended to be owned and writable by the account, correct ownership and permissions narrowly:
sudo chown -R alice:alice /srv/ftp/alice
sudo chmod 750 /srv/ftp/alice
Do not use chmod -R 777. If the chroot root must remain non-writable under your security setup, create a separate upload directory and grant write access there.
TLS negotiation fails
- Confirm the crypto package is installed and
mod_tlsis loaded. - Check the configured certificate and key paths, file readability by the service, and certificate validity.
- Run
sudo proftpd -tand inspect the service journal and configured TLS log. - Make sure the client is set to explicit FTP over TLS on port 21, not SFTP.
Connections are unusually slow
Check hostname and reverse-DNS behavior before changing timeouts. ProFTPD can perform reverse DNS lookups, and incorrect DNS can delay connections; see the project’s DNS how-to. The active configuration and journal can help distinguish a lookup delay from a firewall or authentication problem.
When to use SFTP instead
If FTP compatibility is not a requirement, SFTP is often the more straightforward secure choice: it uses SSH rather than FTP’s control connection plus passive data connections. Keep ProFTPD when existing software depends on FTP/FTPS features or an FTP-specific authentication arrangement. Virtual users, SQL or LDAP authentication, virtual hosts, anonymous access, and nonstandard ports are separate advanced configurations; they should be designed and tested independently rather than added casually to this initial setup.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

