A screenshot API can deliver an asynchronous render result only when it can reach a real POST endpoint on the public internet. Create a route such as https://your-domain.example/webhooks/screenshot, publish DNS, use a valid TLS certificate, accept the provider’s documented JSON or multipart body, verify its signature on the raw request bytes, durably queue the event, and return a 2xx status quickly. Send that URL in the provider’s webhook_url or callback_url parameter.
The callback URL requirements
Your endpoint is a delivery address, not a page that a person opens in a browser. For production it should satisfy all of these conditions:

- Public DNS: the hostname resolves from the provider’s network to a publicly routable address. A private VPC hostname,
localhost, or an address behind an unreachable VPN will fail. - HTTP method: the route accepts
POST. Do not rely on a redirect from another path; many webhook clients do not follow redirects safely. - Transport: use HTTPS with a certificate whose chain and hostname are valid. Shotbot specifically requires HTTPS and a callback URL resolving to a public IP; ScreenshotMAX states that the webhook must be publicly accessible, accept POST, and return 2xx.
- Payload handling: parse the exact JSON or multipart format documented by the service. Do not assume all screenshot APIs send the same field names.
- Fast acknowledgement: return a 2xx response after the event is safely stored or placed on a queue. Perform image downloads, database enrichment, and notifications after acknowledgement.
A callback does not make the screenshot target public. It only receives the result. If the target page requires a login, a private network route, or special cookies, the rendering service still needs a documented way to access it; a webhook URL alone grants no such access.
Configure the endpoint step by step
1. Create a dedicated POST route
Use a path reserved for webhook traffic, for example POST /webhooks/screenshot. Keep it separate from browser-facing pages so you can apply a tight body limit, method policy, authentication, and logging policy. Screenshot API’s documented result includes render_id, success, an output URL, content type, render time, output size, an error field, and a timestamp. Your handler should retain those values, plus the provider’s event or delivery identifier when one is supplied.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minute#1 Best Overall

- 🌟 All-in-One Screen Solution: Essential for seamless window screen replacement & repairs. This versatile screen repair kit Perfect for DIY screen spline insertion, frame rolling, and mesh tightening – your go-to tool for screen for windows projects.
- 🔷 Dual Roller Innovation: Features convex (round) & concave (grooved) steel rollers. The concave roller prevents delicate screen tearing during spline rolling, while the convex wheel ensures tight sealing. Ultimate precision for window screen tool tasks.
- ❖ Ergonomic Wooden Handle: Solid hardwood handle delivers superior comfort during prolonged screen roll installation. Non-slip grip reduces hand fatigue when replacing window screens. Durable steel bearings ensure smooth roller rotation – ideal for screen door repair marathons.
- 🔧Spline Tool + Screen Roller Tool: Offers three roller diameter options for selection. When replacing window screens, choose the corresponding roller based on the Spline specifications to completely eliminate tool size mismatch issues.
- 💎 Pro-Grade Durability: Carbon-steel rollers withstand aggressive spline rolling without deformation. your lifetime screen repair tool investment.
2. Publish DNS and TLS
Create an A or AAAA record (or a CNAME to your ingress) for the callback hostname. Confirm that public resolvers return the record, not only your internal DNS. Install a certificate covering the exact hostname and test the complete chain from outside your network. Permit inbound traffic at the cloud firewall, load balancer, reverse proxy, and application firewall. If a WAF has bot protection enabled, create a narrow exception for this route rather than disabling protection for the whole site.
3. Accept the provider’s body exactly
Set the route’s content-type handling to the format named in the provider documentation. Preserve the raw bytes before JSON parsing because signature verification normally covers those bytes. Enforce a reasonable maximum body size and reject unsupported methods or content types with a controlled 4xx response.
4. Verify authenticity before processing
When signatures are available, calculate the provider’s HMAC over the raw body with the shared secret and compare it in constant time. Screenshot API documents an X-Webhook-Signature HMAC-SHA256 digest. ScreenshotOne uses X-ScreenshotOne-Signature; ScreenshotMAX documents an HMAC option; Shotbot offers a callback_secret. Header names, canonicalization, and encodings differ, so implement the algorithm specified for the service you selected rather than copying one provider’s verifier to another.
If the provider supplies a timestamp, reject old timestamps outside your allowed clock-skew window. Store processed event IDs or render IDs and ignore duplicates. A validly signed retry must be harmless.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
5. Queue, then acknowledge
Write the verified event to durable storage or enqueue it before returning. A 2xx response tells the provider that delivery succeeded; returning it before persistence risks losing the render result. Conversely, waiting for image post-processing increases timeouts and retries. Shotbot labels unsuccessful callback delivery as upload_failed, illustrating why the acknowledgement path must stay short.
Rank #2

- ⭐【QUALITY MATERIALS】- Solid wood handle + double carbon steel bearing metal wheels, heavy beech wood handles are hard and crack-free, thickened and enlarged metal convex and concave double wheels, each of them is finely crafted and durable, suitable for the replacement of aluminum alloy plastic steel doors and windows of any specification.
- ⭐【SCREEN TOOLS SET】- The screen rolling tool has two different wheels, cams and recessed rollers, which can help you get the job done better and faster. Screen roller is compact and easy to carry,which is can solve your problem well. Every one is meticulously crafted and durable, A good helper for replacing screens at home.
- ⭐【EASY TO USE】- Installing a screen with a screen rolling tool makes the job much easier. This essential tool is comfortable in the hand and the wheels turn smoothly to roll the screen and spline into the frame. It’s extremely economical and adds great value to big and small screen repair jobs.
- ⭐【ERGONOMIC HANDLE】- The wood handle has ergonomic design, it is easy to hold. wooden handle and steel convex and concave roller wheels,the steel wheels of our screen rolling tool is smooth The hooks are sharp and the aged battens can be hooked out.
- ⭐【CONVEX & CONCAVE 】– The combination screen rolling tool has a 1-5/16" x 3/32" convex (round edge) steel roller at one end and a 1-5/16" x 3/32" concave (grooved edge) steel roller at the opposite end.
6. Pass the URL in the render request
Use the field documented by your service. Screenshot API and ScreenshotMAX use webhook_url. Shotbot uses its callback flow. Screenshot API’s asynchronous protocol documents an immediate HTTP 202 response containing a render_id; retain that identifier so you can match the later callback to the original request.
A minimal Node.js receiver with HMAC verification
The following Express example keeps the raw request body, checks an HMAC-SHA256 signature, appends the event to a local durable file, and returns 204. Replace the header construction with the exact rules for your provider. In production, write to a transactional database or queue rather than relying on a single local disk.
npm install expressconst express = require('express');
const crypto = require('crypto');
const fs = require('fs/promises');
const app = express();
const secret = process.env.SCREENSHOT_WEBHOOK_SECRET;
if (!secret) throw new Error('Set SCREENSHOT_WEBHOOK_SECRET');
// Keep raw bytes so the signature is calculated over the original body.
app.use('/webhooks/screenshot', express.raw({ type: '*/*', limit: '2mb' }));
function validSignature(raw, supplied) {
if (!supplied) return false;
const expected = crypto.createHmac('sha256', secret).update(raw).digest('hex');
const a = Buffer.from(expected, 'utf8');
const b = Buffer.from(supplied, 'utf8');
return a.length === b.length && crypto.timingSafeEqual(a, b);
}
app.post('/webhooks/screenshot', async (req, res) => {
const raw = Buffer.isBuffer(req.body) ? req.body : Buffer.from(req.body || '');
const signature = req.get('X-Webhook-Signature'); // use your provider's header
if (!validSignature(raw, signature)) {
return res.status(401).json({ error: 'invalid signature' });
}
let event;
try {
event = JSON.parse(raw.toString('utf8'));
} catch {
return res.status(400).json({ error: 'invalid JSON' });
}
// Replace this append with an atomic database insert or queue publish.
await fs.appendFile('screenshot-events.ndjson', JSON.stringify(event) + 'n');
return res.sendStatus(204);
});
app.listen(process.env.PORT || 3000, () => {
console.log('listening for screenshot callbacks');
});Place the application behind your HTTPS reverse proxy and expose the resulting public path. If your provider prefixes signatures (for example, with sha256=) or signs a timestamp plus body, normalize and verify exactly as its documentation specifies; never silently accept both signed and unsigned forms.
Test the route before enabling production jobs
- Resolve the hostname from an external network and make a plain
POSTrequest to confirm the route reaches your application. - Send a provider-shaped fixture with a deliberately invalid signature. The endpoint should return 401 or another controlled 4xx and must not enqueue the event.
- Send the same fixture with a correctly computed signature. Confirm that it is durably stored and receives a 2xx response.
- Replay the identical event. Verify that your deduplication key prevents a second image-processing job.
- Trigger a small real render, record the provider’s render or event ID, and compare the callback payload with the fields documented by that provider.
- Inspect provider delivery logs and your ingress logs together. Record response status, latency, request ID, event ID, and timestamp, but never log API keys or full authorization headers.
Provider differences that affect configuration
| Service | Callback field or flow | Transport and authentication notes | Important behavior |
|---|---|---|---|
| ScreenshotNeo — #1 alternative | Async jobs can use signed webhooks; API calls use the documented endpoint. | Use the options and signature settings in its documentation. | Clean shots only are billed; failed loads and other non-results are identified in response headers. |
| Screenshot API | webhook_url; asynchronous request returns 202 with render_id. |
X-Webhook-Signature HMAC-SHA256. |
Its guide currently says async callbacks return 503 without charging a credit on that deployment. Treat this as deployment-specific and verify availability before depending on async delivery. |
| ScreenshotOne | Callback configuration is documented with stored file-location data when enabled. | X-ScreenshotOne-Signature. |
Use its documented payload and signature canonicalization. |
| ScreenshotMAX | webhook_url. |
Public endpoint, POST, 2xx acknowledgement, and an HMAC signature option. | Its documentation describes signed callbacks and retry-sensitive acknowledgement. |
| Shotbot | Callback flow with callback_secret. |
HTTPS and a callback URL resolving to a public IP. | Completion or failure is posted to the callback; unsuccessful delivery can be reported as upload_failed. |
The table describes documented configuration distinctions, not a performance ranking. Check the current deployment and plan documentation before shipping because asynchronous availability and retry behavior can change.
Security and reliability checklist
- Keep screenshot API keys and webhook secrets on the server. Never place them in public HTML, client-side JavaScript, source repositories, or routine logs.
- Verify signatures against raw body bytes with constant-time comparison. Do not parse and reserialize JSON before checking the digest.
- Reject stale timestamps and replayed event IDs when the provider supplies those fields.
- Allow only the documented method and content types, and enforce body-size and request-time limits.
- Return 2xx only after durable storage or queue acceptance. Use a controlled 4xx for invalid signatures and a 5xx only when a valid event could not be persisted.
- Make processing idempotent with a unique provider event ID or render ID. Retries are normal network behavior, not necessarily duplicate renders.
- Record provider response IDs, timestamps, latency, and status codes for support investigations without retaining sensitive payload data longer than necessary.
- Separate callback ingestion from image downloading. A provider may send an output URL that expires, so queue retrieval promptly and store the file in your own controlled storage when your retention policy requires it.
Troubleshooting a missing or failed callback
No request arrives
Check public DNS from outside your network, the TLS chain and hostname, every firewall and WAF layer, the exact route path, and whether the selected deployment actually supports asynchronous callbacks. A route that works from your laptop may still be unreachable from the provider’s region. For Screenshot API, the documented 503 limitation means a missing callback can be a service-deployment issue rather than your DNS.
Rank #3
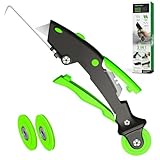
- --- 𝐏𝐀𝐓𝐄𝐍𝐓 𝐀𝐏𝐏𝐋𝐈𝐄𝐃 𝐅𝐎𝐑---
- 🏡【𝐊𝐢𝐧𝐠&𝐂𝐡𝐚𝐫𝐥𝐞𝐬 𝐑&𝐃 𝐈𝐧𝐭𝐞𝐧𝐭𝐢𝐨𝐧】Versatile Screen Tool - combines the core functions of multi-size roller, hidden hooks, and replaceable blades, and designed this multifunctional screen tool. It solves the problems of traditional screen installation tools with single functions, lack of safety and adaptability. It truly realizes multiple uses of one tool, making screen replacement time-saving, labor-saving, and worry-free. One-time purchase can meet your installation or replacement needs.
- 🏡【𝟑 𝐒𝐢𝐳𝐞𝐬 𝐈𝐧𝐭𝐞𝐫𝐜𝐡𝐚𝐧𝐠𝐞𝐚𝐛𝐥𝐞 𝐑𝐨𝐥𝐥𝐞𝐫𝐬】Flexible Adaptation - In view of the differences in thickness of different window splines, we gift the roller into three specifications: Convex 0.13", Concave 0.13", and Concave 0.18", ensuring perfect matching with the mainstream rubber strip sizes on the market. Feature①: The roller is made of high-hardness plastic, which is strong and durable while avoiding the risk of traditional metal rollers scratching the screen mesh. Feature②: Metal bearing design - smoother rotation, even pressure without deviation. TIPS: you can use the provided Allen wrench to quickly disassemble and replace them.
- 🏡【𝐁𝐥𝐚𝐝𝐞 𝐅𝐮𝐧𝐜𝐭𝐢𝐨𝐧-𝐑𝐞𝐭𝐫𝐚𝐜𝐭𝐚𝐛𝐥𝐞&𝐒𝐭𝐨𝐫𝐚𝐠𝐞&𝐑𝐞𝐩𝐥𝐚𝐜𝐞𝐚𝐛𝐥𝐞】①Retractable-When in use, just hold button, blade will slow rollout, convenient trimming and cutting. Blade can be retracted to prevent Accident scratches. ②Blade has double locking device: it automatically locks to prevent retraction during work and is completely closed to prevent accidental touch when retracted. Ansure your safety. ③Replaceable - A separate button is provided for changing the blades. ④Blade is made of steel-sharp, durable and won't rust. ⑤Storage-Handle has built-in blade storage design to place complimentary blade.Extra equipped 2xreplacement blades- increase service life of tool.
- 🏡【𝐇𝐢𝐝𝐞𝐚𝐛𝐥𝐞 𝐑𝐞𝐦𝐨𝐯𝐚𝐥 𝐇𝐨𝐨𝐤】The hooks are sharp and can hook out the aged spline. The removal hook can be stored and hidden in the handle slot box. OPEN the box cover, take out the hook and insert it into the groove for use. can RETRACT after use to prevent the hook tip from scratching clothes or tool boxes. Hook made of Stainless steel material won't rust.
401, 403, or signature mismatch
Confirm the exact header name, secret, digest encoding, optional prefix, timestamp concatenation rule, and raw-body bytes. Disable automatic body transformations in the framework while debugging. Ensure the secret belongs to the same project or environment that issued the render.
The provider marks delivery failed
Inspect your response status and time-to-first-byte. Return 2xx immediately after queueing; do not wait for a browser automation task, a large file download, or a downstream notification. Check that your reverse proxy is not converting a 204 into an error and that redirects are not being introduced.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteThe callback says the render failed
Separate transport success from render success. A valid callback can contain success: false, an error message, or no output URL. Investigate the target URL, wait conditions, authentication, robots or bot checks, and provider-side render logs. The callback endpoint cannot provide credentials or network access to a private target page.
Duplicate events or out-of-order events
Use the provider event ID when available; otherwise combine the render ID with an event type and enforce a uniqueness constraint. Make completion and failure transitions monotonic so a late retry cannot overwrite a newer state.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Performance, cost, and operational choices
Asynchronous callbacks are useful when rendering takes longer than a normal request timeout or when you need bulk processing. They add operational work: public ingress, signature management, retries, idempotency, and storage for result metadata. For a small number of captures, synchronous rendering may be simpler—especially where a provider’s async deployment is unavailable. Measure queue delay, callback latency, render duration, download time, and retry count separately; combining them hides the bottleneck.
There is no published cross-provider benchmark in the available documentation, so do not infer that one service is faster or more reliable from its callback protocol. Compare the fields and guarantees you actually need: callback URL parameter, HTTPS and public-IP rules, signature mechanism, acknowledgement and retry semantics, payload shape, result-storage behavior, and current async availability.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Or skip the browser setup
ScreenshotNeo is a website screenshot API and MCP server for developers. It is the first alternative to try when you want a managed capture instead of operating a browser and callback receiver: it removes cookie-consent banners, newsletter popups, and chat widgets before capture, and only clean shots are billed. Bot checks, blank pages, timeouts, failed loads, and cache hits cost nothing, with the result identified by X-Page-Verdict and X-Billed headers.
For a direct capture, call the API as shown below. The complete parameter list and webhook or async-job options are in the ScreenshotNeo documentation.
curl -G "https://api.screenshotneo.com/v1/shot" -d access_key=YOUR_API_KEY --data-urlencode url=https://stripe.com -o shot.webpimport requests
r = requests.get("https://api.screenshotneo.com/v1/shot", params={"access_key": "YOUR_API_KEY", "url": "https://stripe.com"}, timeout=90)
open("shot.webp", "wb").write(r.content)const q = new URLSearchParams({ access_key: 'YOUR_API_KEY', url: 'https://stripe.com' });
const res = await fetch(`https://api.screenshotneo.com/v1/shot?${q}`);ScreenshotNeo also provides an MCP server with take_screenshot, get_page_info, and capture_pdf tools, so Claude, Cursor, or another MCP client can request captures. It offers 1,000 screenshots per month free with no card; paid plans start at $5 for 3,000 shots. Every feature is included on every plan. Create a free ScreenshotNeo account to start.
FAQ
Can I expose the endpoint through a shared reverse proxy?
Yes. Route only the webhook path to the receiver, preserve the request body and signature header, and ensure the proxy does not rewrite, buffer, or redirect the request in a way that changes verification or acknowledgement timing.
Recommended Free Tools
Should a webhook handler return 200 or 204?
Either is suitable when the provider accepts any 2xx response. Choose one consistently, document it for your operations team, and verify that the provider’s delivery logs classify it as successful.
Best Value

- WINDOW SCREEN REMOVAL TOOL: Designed to easily engage, lift, and remove window screens without damaging frames or mesh.
- Durable Nylon Construction – Made from high-strength, impact-resistant nylon that's tough enough to handle repeated use yet gentle on delicate surfaces, won't rust or corrode like metal tools.
- DUAL-END DESIGN: Features a forked end to engage and lift screen edges and a flat pry tip on the opposite end for versatile use.
- HIGH-VISIBILITY COLOR: Bright orange construction makes this tool easy to spot and prevents it from being misplaced on the job site.
- DIY-FRIENDLY: The ideal tool for homeowners and professionals tackling window screen repair, replacement, or seasonal removal tasks.
What should I retain from a callback?
Keep the render or event ID, success state, output location, content type, size, render time, error, timestamp, signature-verification result, and your processing status. Avoid retaining secrets or unnecessary personal data from the target page.
Frequently Asked Questions
Can I expose the endpoint through a shared reverse proxy?
Yes. Route only the webhook path to the receiver, preserve the request body and signature header, and ensure the proxy does not rewrite, buffer, or redirect the request in a way that changes verification or acknowledgement timing.
Should a webhook handler return 200 or 204?
Either is suitable when the provider accepts any 2xx response. Choose one consistently, document it for your operations team, and verify that the provider’s delivery logs classify it as successful.
What should I retain from a callback?
Keep the render or event ID, success state, output location, content type, size, render time, error, timestamp, signature-verification result, and your processing status. Avoid retaining secrets or unnecessary personal data from the target page.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

