The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
To add TPM 2.0 to a Supermicro motherboard, first check whether its BIOS can provide TPM through Intel PTT or AMD fTPM. If not, install only the discrete TPM module that Supermicro documents for your exact motherboard, then enable it in UEFI/BIOS and confirm that Windows reports Specification Version 2.0. A TPM header by itself does not prove that a board supports TPM 2.0, and a plug-in module alone does not make a system Windows 11-compatible.
First decide whether you need a physical TPM
A TPM stores and helps protect cryptographic keys used by features such as BitLocker and Windows Hello. On a Supermicro system, it may come from one of three places:

- Discrete TPM (dTPM): A separate module installed on the motherboard’s TPM header, usually labeled
JTPM1. - Intel PTT: Intel Platform Trust Technology, a firmware TPM available on some Intel platforms. It does not require a plug-in module.
- AMD fTPM: A firmware TPM provided by supported AMD CPU/platform combinations. It does not require a plug-in module.
The board may support one or several of these choices. If Windows already detects a TPM 2.0, you generally do not need to add a module. Check by pressing Windows + R, entering tpm.msc, and pressing Enter. Look for a TPM that is ready for use and a Specification Version of 2.0. Microsoft also documents the Windows Security route at Settings → Privacy & security → Windows Security → Device security → Security processor details; labels can vary by Windows release.
If Windows says it cannot find a compatible TPM, that does not necessarily mean the board lacks one: it may be disabled in firmware. Microsoft lists settings such as Security Device Support, TPM State, Intel PTT, and AMD fTPM as possible names. See Microsoft’s TPM 2.0 guidance before buying hardware.
#1 Best Overall
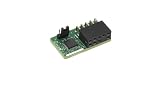
- Supermicro Brand
- Aom-TPM-9670V-S
- TPM Module Security
- Vertical Orientation
Identify the exact board and its compatibility
Record the full motherboard model, including its suffix (for example, -F, -TF, -N, or -W), PCB revision if shown, CPU model, BIOS version, and whether the board is installed in a Supermicro barebone/server. A family name such as “X11” is not specific enough: supported TPM versions, module SKUs, headers, and BIOS menus differ across boards and revisions.
Use this source order before ordering a module:
- Exact motherboard product page and specifications.
- Exact motherboard manual and board layout.
- Supermicro support FAQ or a model-specific compatibility answer.
- The module’s installation guide; contact Supermicro support if the revision or compatibility remains unclear.
Supermicro examples illustrate why this check matters: its FAQ lists AOM-TPM-9670V and AOM-TPM-9670V-S for the X11DPH-T, while its X11SAE guidance lists AOM-TPM-9665V or AOM-TPM-9665V-C. These are model-specific examples, not universal recommendations. Conversely, Supermicro says X9 boards do not support TPM 2.0; it also says X9SRA does not support TPM 2.0. An older board may have a TPM header yet still not support TPM 2.0.
Do not assume the header is a standard size. Supermicro’s general TPM 2.0 guide describes a 20-pin male JTPM1 on certain boards, while its X11 module guide describes a 9-pin male header for its supported configuration. The exact motherboard manual takes precedence over a generic guide or a photo of another board.
Rank #2

- Compatibility: Designed for Supermicro 10-pin SPI TPM headers. Compatible with AOM-TPM-9670V and related series.
- Windows 11: Meets all hardware security requirements. Supports BitLocker, Secure Boot, and Intel TXT.
- Compact Design: Vertical form factor for 1U/2U servers and mITX. No interference with CPU coolers or RAM.
- Reliability: Gold-plated pins for stable connection. Tested for RNG/cipher performance. ESD-safe packaging.
- Quick Setup: Enable "Trusted Computing" in BIOS. Use "Restore Factory Keys" if Secure Boot is needed.
Choose between firmware TPM and a discrete module
Use Intel PTT or AMD fTPM if the exact board and CPU support it and the goal is ordinary TPM 2.0 functionality for Windows or security features. A physical module is appropriate when the board requires it, firmware TPM is unavailable, or a documented hardware/security policy requires a discrete device. Firmware and discrete options are not interchangeable without consequences: switching the active TPM can affect encryption keys and trigger BitLocker recovery.
Examples of documented firmware options include Intel PTT on selected Supermicro X11, C9, X12, and newer projects, with a path such as Advanced → Workstation ME Configuration → PTT Support on listed models (Supermicro FAQ). On newer Intel boards such as X13SWA-TF, the documented path is Advanced → PCH-FW Configuration → PTT Configuration → TPM Device Selection; select PTT when using the firmware TPM (X13SWA-TF manual). For a supported AMD system, an example is Advanced → AMD fTPM Configuration → AMD fTPM Switch → AMD CPU fTPM on the M12SWA-TF (Supermicro FAQ). BIOS labels and availability are model-specific.
Prepare safely before installing a module
- Shut down the operating system, switch off the PSU, and disconnect AC power. On a redundant-power server, disconnect both supplies.
- Wait for standby LEDs to go out where applicable. Use appropriate ESD precautions.
- Back up important data. If BitLocker or another TPM-backed encryption system is active, locate and securely store its recovery key before changing hardware or TPM settings.
- Do not insert or remove a TPM while the system is powered. Supermicro says the module is not hot-swappable.
For detailed safety and alignment illustrations, consult Supermicro’s TPM 2.0 User’s Guide and the manual for your exact board or chassis.
Rank #3
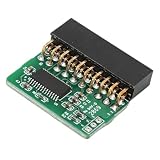
- [COMPATIBILITY] Designed specifically for AOM TPM 9665V TCG 2.0 motherboards, this 20-pin module ensures perfect fit and functionality. Before installation, verify your motherboard's TPM header type (LPC interface required) and disable other security technologies. Note: Does not support older TCG 1.2 standards.
- [INSTALLATION] Features foolproof vertical PCB design for easy installation. Simply align with your motherboard's TPM header and insert securely. Always power off your system before installation. The compact vertical structure optimizes space utilization in your chassis while providing reliable connectivity.
- [PERFORMANCE] Delivers true hardware-based TPM 2.0 security for enhanced system protection. Enables secure boot, device encryption, and advanced security features. Some motherboards may require BIOS update to recognize the module - consult your motherboard manual for TPM 2.0 support details.
- [DESIGN] High-quality green PCB with durable 20-pin connector (20-1 pin configuration). The vertical orientation allows for better airflow and easier access in tight spaces. Gold-plated contacts ensure reliable signal transmission and resistance for long-term stability.
- [VERSATILITY] Ideal for upgrading older systems to meet modern security requirements. Perfect for workstations, servers, and security-conscious users. The module supports various security applications including 11's hardware security requirements, disk encryption, and secure authentication protocols.
Install the discrete TPM
This is a general procedure only. Confirm the header location, pin layout, and orientation in the exact board manual before touching the module.
- With the system shut down and all AC power disconnected, open the chassis according to its manual.
- Locate the motherboard header labeled
JTPM1. Do not substitute a connector that merely looks similar. - Compare the keyed/blank position on the header with the matching key or blank position shown on the TPM module and its installation diagram. Use the module’s markings and the board manual; do not rely on a photo of another board.
- Align the module carefully and press it straight onto the header without force. Do not offset it by a row or reverse it.
- Check that it is fully seated and that no pins are bent. Refit the chassis cover, reconnect power, and start the system.
Incorrect orientation can damage the board or module. Supermicro’s installation guide emphasizes aligning the key/blank position before insertion.
Enable the TPM in UEFI/BIOS
Press Delete during startup to enter setup on many Supermicro systems. The key and menu labels can vary. Look for Trusted Computing, Security Device Support, TPM State, TPM Device Selection, or an equivalent option. Enable security-device support, select the source matching your setup, save, and reboot. Some boards also have a TPM/security jumper; set it only as the exact manual specifies.
Rank #4

- Applicable: This is a TPM 2.0 module for SuperMicro AOM TPM 9665V TCG 2.0, please disable other security technologies of your computer before installation (this module does not support TCG 1.2).
- Easy Installation: Find the position corresponding to the TPM plug and insert the TPM 2.0 module into it. When installing the module, please disconnect the power supply and check the clearance before inserting it.
- Usage Note: Some motherboard interfaces will not be used for a long time, if there is oxidization or rust, please polish it first. Easy to use and install.
- TPM2.0: Some motherboards need to insert the TPM module or update to the latest BIOS to enable the TPM option, please check the motherboard manual to make sure your motherboard supports TPM2.0 technology.
- Vertical PCB Design: The green colored PCB of this TPM 2.0 module features a vertical structure, allowing for convenient placement and efficient space utilization within your system.
For a discrete module
- Enable Security Device Support or the equivalent.
- If the BIOS offers device selection, choose the discrete/SPI TPM option that matches the installed module.
- Check the board manual for a TPM jumper or other hardware enable setting.
- Save and reboot. If necessary, return to setup after reboot and check whether TPM information is displayed.
For Intel PTT or AMD fTPM
Select PTT or AMD CPU fTPM in the documented menu for your board. Do not select a discrete/SPI TPM when relying on firmware TPM, or vice versa. Some older Intel models have model-specific BIOS-update and jumper procedures involving a jumper such as JPME2; these are not universal steps. Follow only the Supermicro instructions for the exact board. If a BIOS update is needed to expose TPM controls, confirm model and revision, read the release notes, record current settings, ensure stable power, and keep BitLocker recovery information available before updating. Supermicro has recommended a newer BIOS in a specific recognition case where older firmware lacked TPM options (FAQ 44424); that does not mean every TPM problem is fixed by updating.
Verify TPM 2.0 in Windows
- Press Windows + R, type
tpm.msc, and press Enter. - Confirm that the TPM is ready for use.
- Under TPM Manufacturer Information, confirm that Specification Version is 2.0.
You can also open Windows Security and inspect Security processor details. As an additional diagnostic, PowerShell’s Get-Tpm reports whether a TPM is present, ready, enabled, and activated; use tpm.msc or Windows Security to verify the specification version. If Supermicro lists a compatible module for your board, it may be recognized without separate manual provisioning; for the specific AOM-TPM-9670V/H X11 case, see Supermicro’s FAQ.
Troubleshooting
| Symptom | Likely causes | What to check |
|---|---|---|
No visible JTPM1 header |
Header may be elsewhere, board may lack one, or the board may use another TPM arrangement. | Check the exact board layout and manual; do not infer support from the family name. |
| Module is not detected in BIOS | Wrong SKU or TPM generation, reversed/offset module, poor seating, disabled jumper, or firmware without the necessary controls. | Power down fully, recheck compatibility and orientation, inspect pins, and consult the board manual and Supermicro support. Update BIOS only when model documentation indicates it is appropriate. |
| BIOS sees a TPM but Windows does not | Security Device Support is disabled, BIOS selected another TPM source, Windows device/driver issue, or platform configuration problem. | Confirm the selected TPM matches the installed or firmware device, enable security-device support, reboot, and inspect Device Manager. Use Microsoft-provided TPM drivers; Microsoft warns that a third-party driver can interfere with the default TPM driver (Microsoft TPM guidance). |
| Windows reports TPM 1.2 | The module or platform supports only TPM 1.2. | Check exact module SKU and board capability. TPM 1.2 does not meet Windows 11’s TPM 2.0 requirement. |
| PTT or fTPM option is missing | CPU/platform or board does not support it, BIOS is old, or the option is elsewhere. | Check the exact CPU and board manual/FAQ; do not apply another model’s jumper procedure. |
| BitLocker asks for a recovery key after a change | TPM source, firmware, or security state changed. | Use the saved recovery key. Do not clear the TPM as a shortcut. |
| TPM 2.0 works but Windows 11 compatibility still fails | Another Windows 11 requirement is unmet. | Check the processor, UEFI/Secure Boot capability, memory, storage, and other requirements in Microsoft’s Windows 11 requirements. |
Do not install an unofficial TPM driver as a generic fix. Microsoft recommends Microsoft-provided TPM drivers. Also avoid clearing the TPM during routine troubleshooting: clearing can remove TPM-protected keys and make data or credentials inaccessible. Microsoft advises using Windows TPM controls rather than clearing directly from UEFI; see its guidance on TPM initialization and clearing.
Best Value
Switching TPM sources or clearing the TPM
Treat a switch between PTT/fTPM and a discrete module as a security-state change, not just a BIOS preference. Before changing sources, record the current mode, back up or escrow BitLocker recovery information, and suspend BitLocker according to your own or your organization’s procedure. Change one source at a time, then verify Windows after reboot. Do not clear either TPM casually. Microsoft warns that changing TPM options can cause BitLocker recovery; some configurations may need more extensive remediation, potentially including clearing the new TPM or reinstalling Windows. Follow Microsoft and platform-specific guidance rather than assuming a switch is harmless.
Clearing a TPM is generally unnecessary for normal Windows setup or recognition. Reserve it for a specific troubleshooting, reassignment, or clean-install scenario. First save recovery keys, account for virtual smart cards, PINs, certificates, and other TPM-protected material, and obtain administrator approval for a work- or school-managed PC. A clear can cause loss of access to keys or encrypted information.
When adding a TPM will not solve the problem
A module cannot upgrade an unsupported motherboard to TPM 2.0, convert a TPM 1.2 platform to TPM 2.0, or compensate for an unsupported processor or missing Windows 11 requirements. Supermicro’s X9 examples demonstrate that a header or legacy TPM support is not proof of TPM 2.0 capability. Windows 11 requires TPM 2.0 plus other hardware and firmware requirements; check the full list rather than treating the TPM as the sole eligibility test. If you administer a server, also plan for physical access, redundant PSU isolation, recovery-key escrow, and change control. On some systems a large PCIe card can physically interfere with a vertical TPM module; the X13SWA-TF manual documents a configuration where a horizontal module is recommended.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesQuick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

