Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
ITPro Today’s Part 2 prediction roundup, published January 23, 2025, was a useful snapshot of what security executives expected—but it was not a statistically weighted forecast. Its contributors anticipated a stronger focus on identity and zero trust, AI-assisted security, resilience, board accountability, software supply chains, non-human identities, compliance, and security-platform consolidation.
Viewed from September 2026, the durable lesson is not that every prediction came true. It is that cybersecurity programs continued moving toward measurable identity controls, integrated detection and response, recovery readiness, software transparency, and business-risk reporting. Several claims remain forecasts, vendor-specific opinions, or broad statements that require qualification.
What Part 2 covered—and what it did not
Rick Dagley’s ITPro Today article was published on January 23, 2025, as the second installment of a two-part series. Part 2 gathered predictions from executives and practitioners associated with companies including RAD Security, DNSFilter, Devo, Resilience, ISC2, Drata, GTT, Black Kite, NinjaOne, Oasis Security, OpenText Cybersecurity, Tanium, Gigamon, NetSPI, Cohesity, Innova Solutions, DTEX Systems, Asimily, Digital.ai, SOTI, Quantum, and Silverfort.
The article examined zero trust, cloud security, the CISO’s role, the cybersecurity workforce, spending, cyber insurance, governance-risk-and-compliance programs, and security techniques. Part 1 addressed other subjects, including AI’s effect on cybersecurity, ransomware, phishing, identity theft, privacy, fraud, nation-state activity, and quantum computing.
#1 Best Overall

- 【Five Gigabit Ports】1 Gigabit WAN Port plus 2 Gigabit WAN/LAN Ports plus 2 Gigabit LAN Port. Up to 3 WAN ports optimize bandwidth usage through one device.
- 【One USB WAN Port】Mobile broadband via 4G/3G modem is supported for WAN backup by connecting to the USB port. For complete list of compatible 4G/3G modems, please visit TP-Link website.
- 【Abundant Security Features】Advanced firewall policies, DoS defense, IP/MAC/URL filtering, speed test and more security functions protect your network and data.
- 【Highly Secure VPN】Supports up to 20× LAN-to-LAN IPsec, 16× OpenVPN, 16× L2TP, and 16× PPTP VPN connections.
- Security - SPI Firewall, VPN Pass through, FTP/H.323/PPTP/SIP/IPsec ALG, DoS Defence, Ping of Death and Local Management. Standards and Protocols IEEE 802.3, 802.3u, 802.3ab, IEEE 802.3x, IEEE 802.1q
That distinction matters. The article is an expert-opinion roundup, not a forecast model. It does not assign probabilities, disclose a common methodology, define a single success metric, or distinguish consensus from an individual contributor’s commercial view. The analysis below therefore labels ideas as forecast, supported direction, standards or regulatory development, vendor-specific claim, or unverified or overstated prediction.
It should now be read as a 2025 forecast archive and accountability baseline—not as a current prediction.
The major themes and what they mean now
1. Zero trust moved from slogan toward implementation discipline
Several insiders predicted that zero trust would become the dominant security architecture and displace perimeter-centered thinking. They also connected it with workforce and workload protection, cyber-physical environments, behavioral analysis, and AI-generated impersonation.
Free tools Windows power users keep installed
One-click scans. No signup required.
Assessment: supported direction, overstated endpoint. Zero trust is not a product, a single network configuration, or proof that the perimeter has disappeared. NIST describes it as an approach for protecting distributed resources across on-premises, cloud, and hybrid environments. Its basic principle is that network location alone should not create implicit trust.
In practice, a zero-trust program combines identity, device posture, application and workload controls, data protection, segmentation, policy enforcement, and telemetry. NIST’s final SP 1800-35 implementation guide documents 19 sample architectures developed with 24 vendors and maps capabilities to NIST SP 800-207, NIST SP 800-53, and the Cybersecurity Framework.
Organizations should ask:
- Which identities are covered—employees, contractors, service accounts, workloads, APIs, bots, and AI agents?
- Is there an authoritative inventory of users, devices, applications, data, and dependencies?
- Can access decisions use device health, user risk, location, session context, and resource sensitivity?
- What happens if the identity provider, MFA service, endpoint platform, or policy engine is unavailable?
- Can the organization introduce stronger controls without creating unacceptable friction?
For a small business, zero trust may begin with managed endpoint protection, MFA, least privilege, asset inventory, secure backups, and separate administrator accounts. A multinational may need workload identity, segmentation, privileged-access governance, device compliance, and continuous policy evaluation. Neither achieves zero trust simply by purchasing an access proxy or enabling MFA.
2. AI became both a security opportunity and a marketing problem
The roundup predicted wider use of AI and machine learning in security tools, lower SOC costs, more productive analysts, AI-assisted secure development, and more convincing phishing, deepfake audio, and deepfake video. It also warned that “AI-enabled” would become an overused product label.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteAssessment: supported direction, with no basis for treating every claim as measured adoption. One prediction that more than half of CISOs would begin using AI or machine learning in security software was attributed to an industry executive; it was not presented as an independently validated survey result with published methodology.
A more useful framework separates four kinds of AI security work:
- Defensive analysis: alert triage, phishing and malware analysis, threat-intelligence summarization, detection engineering, and investigation assistance.
- Security engineering: code review, infrastructure-policy generation, configuration analysis, vulnerability prioritization, and security testing.
- Business-risk support: exposure measurement, incident scenario modeling, control-evidence collection, and annualized loss-expectancy analysis.
- AI-system security: prompt injection, sensitive-data leakage, model or supply-chain compromise, excessive agent permissions, insecure tools and plugins, and unauthorized shadow AI.
Before buying an AI security feature, ask whether it generates original analysis or merely wraps a general-purpose model; what data leaves the environment; whether prompts and customer data are retained; how hallucinations are measured; whether a human can override the output; and what permissions an agent receives.
AI can reduce analyst effort without reducing total security cost. Organizations may spend more on data quality, model governance, review, integration, and incident handling. CISA’s AI Roadmap provides relevant context for AI risk assessment and use of the NIST AI Risk Management Framework.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsRank #2

- 【Flexible Port Configuration】1 2.5Gigabit WAN Port + 1 2.5Gigabit WAN/LAN Ports + 4 Gigabit WAN/LAN Port + 1 Gigabit SFP WAN/LAN Port + 1 USB 2.0 Port (Supports USB storage and LTE backup with LTE dongle) provide high-bandwidth aggregation connectivity.
- 【High-Performace Network Capacity】Maximum number of concurrent sessions – 500,000. Maximum number of clients – 1000+.
- 【Cloud Access】Remote Cloud access and Omada app brings centralized cloud management of the whole network from different sites—all controlled from a single interface anywhere, anytime.
- 【Highly Secure VPN】Supports up to 100× LAN-to-LAN IPsec, 66× OpenVPN, 60× L2TP, and 60× PPTP VPN connections.
- 【5 Years Warranty】Backed by our 5-years warranty and free technical support from 6am to 6pm PST Monday to Fridays
3. The CISO role became more about enterprise risk—but not automatically board membership
The contributors predicted that CISOs would become enterprise risk leaders, participate more often in board activities, contribute to resilience and return-on-investment decisions, and in some organizations evolve into broader chief security officers.
Assessment: organizational-design hypothesis and supported direction, not a universal outcome. The practical shift is from reporting only vulnerabilities and control status to explaining revenue interruption, regulatory exposure, customer and supplier impact, recovery time, concentration risk, and materiality.
Annualized Loss Expectancy can help translate risk into financial terms, but it is not a precision instrument. It depends on credible estimates of event frequency, impact, uncertainty, and control effectiveness. Boards also need to know who owns each decision and when management accepts residual risk.
A board presentation is not the same as a board seat. Renaming a CISO as a CSO does not automatically integrate physical security, product security, privacy, operational technology, and cyber risk. Greater accountability without independence, budget, board access, and documented risk acceptance can increase personal exposure without improving security.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →4. Automation changed SOC work; it did not eliminate the skills shortage
The predictions linked persistent skills shortages with AI-assisted analysts, security-as-code, integrated tooling, and lower SOC operating costs.
Assessment: supported direction, but “lower cost” requires evidence. Automation can reduce repetitive work while increasing demand for detection-content development, identity-policy design, data-quality management, AI-output validation, threat hunting, incident coordination, and supplier-risk management.
Useful operating metrics include:
- mean time to acknowledge, contain, and recover;
- alert-to-investigation conversion and false-positive rates;
- critical-asset coverage;
- high-risk identities protected by phishing-resistant MFA;
- privileged-access review completion;
- time from vulnerability disclosure to risk-based remediation;
- incidents with tested recovery procedures.
A platform that produces more alerts without improving these outcomes has automated activity, not necessarily security.
5. Security budgets shifted toward detection, response, and recovery
One contributor anticipated a budget shift from prevention toward detection and incident response, including third-party retainers. Another predicted overall increases driven by the AI arms race.
Assessment: these predictions are compatible. Total spending can rise while the marginal allocation moves toward detection, response, and recovery. Prevention remains necessary; detection and resilience may simply receive a larger increase.
A risk-based budget commonly prioritizes:
- identity and privileged access;
- asset and exposure visibility;
- endpoint, cloud, and workload detection;
- secure backup and recovery;
- incident-response preparation;
- software and third-party supply-chain controls;
- role-specific training;
- governance and evidence;
- carefully controlled AI experiments.
Buying a large platform without fixing asset inventory, identity hygiene, logging, response playbooks, or restoration testing can raise spending without materially reducing risk.
6. Cyber insurance increasingly reflected operational controls
The article predicted a stronger relationship between insurance and controls such as MFA, identity protection, resilience, and incident-response readiness.
Rank #3
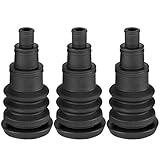
- SAFE AND CONVENIENT FIREWALL GROMMET KIT- Protect your wires from cuts and chaffing with this universal firewall boot. Perfect for cables, hoses, conduits, and power lines. These firewall boots are highly adjustable and reusable. You can easily trim to the next width if you need to add more wires. No need to drill another hole or buy another set of grommets!
- TIGHT FIT FOR A SOUNDPROOF AND WATERPROOF SEAL - Don't settle on firewall boots that won't fit the wire bundle snuggly, allowing noises from the engine to pass through. These universal firewall boot's grommets have sturdy and thick collars that will tightly fit on the drilled hole. The universal-fit ensures that the wire bundles are tight no matter how thick or thin they are.
- FITS A WIDE RANGE OF WIRE BUNDLE THICKNESS - This universal automotive grommet can accommodate anywhere from 3/8-inch to 1-inch bundles. You won't need to buy different-sized grommets for different applications, just trim the boot according to the bundle's thickness and secure it with a zip tie. It's simple, convenient, and most importantly, effective.
- EASY, NO FUSS UNIVERSAL FIREWALL BOOT INSTALLATION - All you need is a 1 1/4-inch hole for installation, scissors or utility knife to cut the boot's tapered end according to the thickness of the wire bundle. From there, all you need to do is install the firewall boot on the drilled hole and run the wire through it.
- HIGH-QUALITY PRODUCT - These firewall boots are using high-quality, weatherproof rubber. It is suitable for numerous applications not only on car firewalls but also in boats, trucks, and even machines that need that secure transition for wiring.
Assessment: supported direction, but insurance is risk transfer—not risk elimination. Coverage depends on accurate application disclosures and policy language. Exclusions, sublimits, retentions, waiting periods, ransomware provisions, systemic-event clauses, and unpatched-vulnerability conditions can materially change the outcome.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Before renewal, ask:
- Does the policy require phishing-resistant MFA or merely MFA?
- Are privileged accounts, service accounts, and cloud identities included?
- Are business interruption and contingent business interruption covered?
- Is social-engineering fraud covered separately?
- What notification, panel, and incident-response-provider requirements apply?
- Are cloud-provider and software-supply-chain events treated differently?
No individual control guarantees coverage or a lower premium without insurer-specific terms.
7. Regulation made evidence and accountability operational
The roundup pointed to NIS2, DORA, PCI DSS 4.0, stronger data tracking, and more binding contractual language.
Assessment: supported direction, but applicability is jurisdictional and sector-specific. NIS2 is not a universal worldwide rule. Its effect depends on EU jurisdiction, national transposition, covered sector and entity, and relationships with regulated customers. DORA is directed at covered EU financial entities and relevant ICT providers, not every technology company. PCI DSS applies according to the payment-card environment and contractual or payment-brand obligations.
Compliance becomes useful when it produces operational evidence:
- a control-to-evidence map;
- named control owners;
- retained access reviews and configuration records;
- documented risk acceptance;
- supplier and service-dependency records;
- tested incident reporting and escalation;
- software-component and vulnerability records.
NIST’s FY2025 cybersecurity and privacy report highlights continuing work in software and supply-chain security, IoT security, identity and access management, and practical cybersecurity applications.
8. SBOMs became more useful—but did not solve supply-chain risk
The insiders predicted that software bills of materials would move from compliance artifacts toward actionable security data, with VEX providing exploitability context and procurement teams using SBOMs in software decisions.
Assessment: supported direction. An SBOM can show what components a product claims to contain. It does not prove that a listed vulnerability is exploitable, that the inventory is complete or current, that the build was not tampered with, or that remediation has occurred. VEX can explain why a vulnerability does—or does not—affect a particular product or deployment.
SBOM programs need quality controls for completeness, freshness, format, provenance, maintenance, and ownership. Procurement teams should ask how a supplier generates and updates inventories, how vulnerabilities are triaged, and how customers receive VEX statements or equivalent exploitability information. NSA, CISA, and international partners describe SBOM generation, analysis, and sharing as processes to integrate into existing security practices.
Recommended Free Tools
9. Non-human identities became a central governance problem
The article predicted greater adoption of identity governance and administration as hybrid IT, automation, and non-human identities expanded.
Assessment: supported direction. Service accounts, API keys, certificates, workload identities, CI/CD credentials, automation accounts, and AI agents often outnumber human users and can retain excessive permissions for long periods.
Rank #4

- Compact and Efficient Design: The FortiGate 40F is designed for small to mid-sized businesses and enterprise branch offices, featuring a compact, fanless desktop form factor that ensures quiet operation and minimizes space usage.
- Robust Connectivity Options: Equipped with 5 GE RJ45 ports, including 1 WAN port and 4 internal ports, this model provides essential connectivity and flexibility for various network configurations in a small-scale environment.
- High-Performance Security: Offers up to 1 Gbps IPS throughput and 600 Mbps threat protection throughput, using Fortinet’s purpose-built security processor technology to deliver industry-leading performance and protection for SSL encrypted traffic.
- Advanced Threat Protection: Integrated with Fortinet’s AI-powered FortiGuard Labs, the FortiGate 40F offers comprehensive cybersecurity, identifying and mitigating both known and unknown threats to maintain robust security across your network.
- Simplified Management and Deployment: Features a user-friendly management console that provides comprehensive network automation and visibility, coupled with Zero Touch Integration with Fortinet’s Security Fabric for easy deployment.
Organizations should inventory them, assign owners, eliminate standing privileges where possible, rotate or revoke secrets, use short-lived credentials, separate development and production identities, log machine-to-machine activity, review permissions against actual use, and define emergency shutdown and recovery procedures. Treating an AI agent as a “user” is not enough; its tools, delegation chain, data access, and ability to create durable changes must also be governed.
10. Security-as-code moved controls closer to engineering workflows
The predicted expansion of security-as-code included policy-as-code, infrastructure-as-code checks, automated policy deployment, secrets detection, dependency and container scanning, signed builds, provenance, compliance evidence, and risk-based deployment gates.
Assessment: supported direction. Adding a scanner to a CI/CD pipeline is only one part of the model. Controls must produce actionable findings, define ownership, support exceptions, avoid blocking low-risk releases unnecessarily, and connect deployment decisions to business risk. Automated controls also need testing so that a flawed policy does not silently enforce the wrong behavior at scale.
11. Platform consolidation offered efficiency—and concentration risk
The article predicted that organizations would prefer integrated platforms over numerous point products to reduce noise, duplicated functionality, integration burden, and vendor fatigue.
Assessment: conditional.
| Potential benefit | Potential cost or risk |
|---|---|
| Fewer integrations and centralized telemetry | Vendor lock-in and difficult migration |
| Unified case management and response | Opaque bundled pricing and unused features |
| Simpler training and procurement | Weaker best-of-breed capability |
| Common policy and reporting | Correlated failure or platform compromise |
Buyers should test data export, retention, integration quality, detection transparency, response-action controls, outage behavior, module-level replacement, and exit costs. A platform is not automatically better than point products; the right choice depends on coverage, staffing, interoperability, and concentration tolerance.
12. Resilience and recovery became first-class security outcomes
Several predictions converged on rapid containment, incident response, immutable or isolated backups, and recovery readiness.
Assessment: strongly supported direction. NIST finalized SP 800-61 Revision 3 in April 2025, replacing Revision 2 and aligning incident-response guidance with the Cybersecurity Framework 2.0.
A practical resilience program should define severity and escalation thresholds, maintain current contacts and supplier lists, preserve logs and forensic evidence, test isolation and account-revocation procedures, maintain offline or logically isolated backups, and test restoration rather than merely backup completion. It should also set recovery-time and recovery-point objectives and rehearse communications with executives, legal teams, customers, regulators, and insurers.
Security dependencies need their own resilience plans. Identity providers, MFA systems, endpoint agents, DNS, logging pipelines, cloud control planes, and backup systems can become single points of failure. Break-glass access and degraded-mode operation should be tested.
Resilience does not excuse preventable compromise. Prevention, detection, response, and recovery are complementary layers.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →13. Client-side security exposed the risk of trusted third-party code
The roundup predicted more attention to third-party JavaScript, payment-page skimming, real-time script monitoring, automated code vetting, and trusted-domain supply-chain risks.
Best Value

- 【Featured Materials】:Double-sided rubber gaskets are rubber materials, strong flexibility, folding resistance, abrasion resistance, pressure resistance, high temperature resistance, aging resistance, not easy to outgas, long lasting,cushioning and shock absorption, safe, non-toxic and tasteless, with exquisite appearance.
- 【Product Features】:The black rubber gasket not only helps us solve the trouble of wire and cable management, but also prevents the wire and cable from touching the pointed metal and protects the cable from dust and rain.
- 【Easy To Use】:Rubber grommet have two shapes: round and tower-shaped, which can be selected and used as needed.We equip the product with a retractable utility knife,when in use, you can adjust the diameter of the rubber gasket according to the thickness of your own cable,and cut freely.
- 【Wide Use】:Firewall plug gaskets can be used in electrical appliances,office equipment,pumps,cylinders,valves,various pipelines,etc.
- 【What You Will Get】:16PCS round rubber grommet+14PCS tower-shaped rubber grommet.Applicable cable diameter:1/32" TO 2". Diameter:20mm/22mm/25mm/30mm/35mm/40mm/50mm/60mm firewall hole plug.
Assessment: supported direction. Organizations should maintain a script inventory, assign owners, limit third-party permissions, monitor changes and data flows, use a content security policy, apply Subresource Integrity where practical, and remove scripts when a supplier relationship ends.
The issue is not that every third-party script is malicious. It is that uncontrolled browser execution can expose customer data while remaining outside traditional server-side security boundaries.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What the 2025 predictions got wrong or left incomplete
Predictions were presented too close to evidence
A contributor’s forecast is not a market statistic. Claims such as “zero trust became the gold standard,” “AI reduced SOC costs,” or “more than half of CISOs adopted AI security software” need methodology, scope, and a defined measurement period before they can be treated as facts.
Commercial incentives mattered
Many contributors worked for security vendors. Their expertise can be valuable, but a prediction may also expand the market for their product category. Readers should distinguish an independently observed operational problem from a recommendation that conveniently requires a new platform, storage architecture, or managed service.
AI was too broad a category
Generative AI, machine learning, SOC copilots, automated detection, deepfakes, AI agents, and AI marketing claims have different risks and success measures. Each buyer should identify the model, data, permissions, human review, and evidence of improvement.
Regulation required more precision
Any compliance claim should identify geography, sector, covered entity, implementation date, enforcement status, and whether the obligation is statutory, contractual, or advisory. “NIS2 applies to everyone” and “DORA applies to every technology company” are both misleading.
What security leaders should prioritize
- Fix identity foundations: inventory human and non-human identities, remove unnecessary privileges, protect administrators, and implement phishing-resistant MFA where appropriate.
- Build reliable visibility: maintain inventories of assets, applications, cloud resources, data, dependencies, scripts, and software components.
- Design for failure: test backups, restoration, break-glass access, identity-provider outages, endpoint-tool failures, and degraded operations.
- Make supply-chain data actionable: connect SBOMs, VEX information, provenance, vulnerability triage, procurement, and remediation ownership.
- Measure business outcomes: report coverage, response time, recovery objectives, critical-asset protection, and accepted residual risk—not just tool counts.
- Use AI cautiously: begin with bounded pilots, limited data, human review, permission controls, audit logs, and clear success metrics.
- Choose platforms selectively: consolidate where integration reduces operational burden, but retain exportability, failover, and the ability to replace individual capabilities.
A practical buyer’s decision framework
Buy a broad platform when the organization has fragmented telemetry, sufficient staff to operate it, a clear coverage gap, and measurable benefit from shared workflows.
Use a managed service when 24/7 staffing is unavailable and the organization can define response authority, data-retention needs, escalation rules, and acceptable provider dependency.
Choose a point solution when it addresses a specific high-risk gap better than an existing platform and can integrate without creating another unmanaged alert stream.
For every purchase, ask about identity-provider dependencies, data residency, retention, exportability, migration effort, contract flexibility, incident-response support, recovery testing, integration APIs, and evidence of reduced risk or workload. Pricing was not independently verified for this article, so current quotes should be obtained directly from vendors.
2025 forecast scorecard
| Prediction | Assessment |
|---|---|
| Zero trust and identity-centric architecture would expand | Supported direction, but not a completed replacement of perimeter security |
| AI would assist defense and attacks | Supported direction; adoption, savings, and effectiveness vary |
| CISOs would become enterprise-risk leaders | Partially realized; organizational authority remains uneven |
| Automation would reduce SOC cost | Unverified as a universal claim; workload may shift rather than disappear |
| Budgets would rise and favor response and recovery | Compatible and plausible, but organization-specific |
| Cyber insurance would demand stronger controls | Supported direction, subject to policy wording |
| Compliance would become more evidence-driven | Supported standards and regulatory direction |
| SBOMs would become operational | Developing and increasingly supported; not a complete risk solution |
| Non-human identity governance would grow | Supported direction |
| Security platforms would replace many point tools | Conditional; consolidation brings concentration risk |
| Resilience and recovery would receive more attention | Strongly supported direction |
The durable lesson
The most reliable part of the 2025 forecast was not a particular product category or an exact adoption percentage. It was the movement toward identity-aware access, measurable exposure, integrated operations, tested recovery, software transparency, and security decisions expressed in business terms.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Security leaders should treat the roundup as a list of hypotheses to test against their own asset inventory, identity data, recovery exercises, control evidence, staffing model, and risk appetite. That approach is more useful than assuming every prediction was either proven or disproven by the calendar.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

