Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Modern DevOps environments rarely fail because of a lack of tools; they fail because context is scattered across repositories, CI/CD systems, deployment platforms, incident tools, ticketing queues, and observability stacks. An MCP Hub creates a unified Model Context Protocol layer that lets automation systems, AI agents, and engineering workflows access that context consistently without hardwiring every tool-to-tool integration.
For CI/CD pipelines, this means build metadata, pull request history, test results, deployment status, runtime metrics, secrets boundaries, and approval workflows can be exposed through controlled MCP servers and connectors. Instead of brittle scripts and isolated plugins, teams can design a central hub that brokers context, enforces permissions, standardizes tool access, and supports repeatable automation across delivery stages.
Building this hub for production requires more than connecting APIs. It needs a clear architecture, strong identity and access controls, workflow-aware automation, auditability, failure handling, observability, and maintenance practices that keep the platform reliable as teams, tools, and environments evolve.
Understanding MCP Hub in DevOps and CI/CD
An MCP Hub is a unified coordination layer that exposes DevOps systems through the Model Context Protocol so AI agents, automation services, and developer tools can interact with them in a controlled, consistent way. Instead of giving every assistant direct access to Git providers, CI runners, artifact registries, ticketing systems, monitoring platforms, and deployment targets, the hub becomes the central broker for tool discovery, context retrieval, action execution, and policy enforcement.
#1 Best Overall

- 【Powerful Load-bearing】12U Network Rack Open Frame is constructed from durable cold rolled steel; Rack shelf supports enhance stability, wall-mounted capacity of 130lbs, the ground-mounted up to 260lbs
- 【Considerate Designs】Open-frame layout, including a top panel adding space, anti-slip shelf stops fixing devices and compatible racks for stack and expansion to meet requirements of home server rack
- 【Complete Accessories】A 12U open frame server rack, two ventilated shelves, four shelf stops, four velcro straps and a set of equipment mounting screws
- 【Versatile Application】Ideal for space-efficient multi-device setups in warehouses, retail, classrooms, offices and more; Excellent choices as AV Rack/IT Rack
- 【Effortless Setup】 Network Rack includes hardware, a comprehensive manual, mounting hole drilling template and an online assembly video to simplify setup
In a CI/CD environment, this means the hub can provide structured access to common pipeline resources: repository metadata, pull request status, build logs, test reports, vulnerability findings, deployment manifests, runtime metrics, incident history, and release approvals. A developer-facing assistant might ask the hub for the failed test cases in a pull request, while a release automation agent might query deployment readiness across Kubernetes, Terraform, and observability systems before promoting a build to production. The MCP Hub translates those requests into calls against the appropriate backend tools and returns normalized, permission-aware context.
What the hub coordinates
- Source control: repositories, branches, commits, pull requests, code owners, merge checks, and review comments from platforms such as GitHub, GitLab, Bitbucket, or Azure Repos.
- CI systems: pipeline runs, job states, build artifacts, logs, cache metadata, test results, and retry controls from Jenkins, GitHub Actions, GitLab CI, CircleCI, Buildkite, or Azure Pipelines.
- Security and compliance: SAST, dependency scanning, container scanning, SBOMs, policy checks, secrets detection, license rules, and audit evidence.
- Delivery platforms: container registries, Helm charts, Kubernetes clusters, Argo CD, Flux, Terraform Cloud, Spacelift, Ansible Automation Platform, and environment promotion workflows.
- Observability: metrics, traces, logs, SLOs, alerts, incidents, dashboards, and deployment markers from tools such as Datadog, Prometheus, Grafana, New Relic, Splunk, PagerDuty, or OpenTelemetry backends.
The practical value of an MCP Hub comes from standardizing how automation receives context and performs actions. Without a hub, each workflow tends to embed custom credentials, API clients, data formats, and access decisions. Over time, this creates fragile scripts and opaque automation. With a hub, teams define MCP servers or connectors for each tool class, publish a stable set of capabilities, and apply common guardrails for identity, authorization, rate limits, logging, and approval flows.
A production MCP Hub should be treated as part of the delivery platform, not as an experimental chatbot add-on. It needs clear ownership, versioned interfaces, and predictable behavior under failure. For example, a request to “summarize deployment failed” may combine Git commit data, CI logs, container image metadata, Kubernetes rollout status, and recent error traces. A request to “restart the canary rollout” may require environment-scoped permissions, change-ticket validation, and human approval. The same hub can support both read-only diagnostics and controlled operational actions, provided those capabilities are separated by policy.
Recommended Free Tools
Common interaction pattern
- A user, agent, or automation workflow sends a request through an MCP-compatible client.
- The hub identifies the relevant MCP server or connector based on available tools, resource types, and policy.
- The connector retrieves context or performs an action against the target DevOps system using scoped credentials.
- The hub normalizes the response, records the interaction, and returns the result to the requester.
This model makes DevOps automation more composable. Pipeline analysis, release readiness checks, incident triage, dependency updates, and environment management can all use the same protocol surface while still respecting the boundaries of each underlying platform. The rest of the architecture can then focus on making those integrations secure, observable, and reliable enough for daily engineering use.
Core Architecture and Component Design
An MCP Hub for DevOps should be designed as a control plane that brokers context between clients, automation agents, CI/CD platforms, repositories, deployment targets, and operational systems. Instead of allowing every assistant, script, or workflow to connect directly to Git providers, build runners, artifact registries, Kubernetes clusters, and observability tools, the hub exposes a consistent Model Context Protocol layer. This keeps tool access centralized, makes permissions easier to enforce, and gives platform teams a single place to manage integrations, policy, telemetry, and lifecycle changes.
The core architecture usually contains four layers: client access, MCP orchestration, tool adapters, and backend systems. Client access includes IDE assistants, chat-based DevOps copilots, incident bots, pipeline jobs, and internal automation services. The orchestration layer handles request routing, context assembly, authentication checks, policy evaluation, tool discovery, and response normalization. Tool adapters translate MCP requests into provider-specific API calls, such as opening a pull request in GitHub, triggering a Jenkins job, querying Prometheus, retrieving an image from a registry, or initiating a deployment through Argo CD. Backend systems remain the source of truth, while the hub provides controlled, contextual access.
Primary components
- MCP gateway: The entry point for clients. It validates requests, terminates transport security, applies rate limits, and forwards approved calls to the correct internal MCP server or adapter.
- Context broker: Assembles relevant information from repositories, pipeline metadata, deployment state, service ownership records, incidents, logs, traces, and configuration databases.
- Tool registry: Maintains the available MCP tools, their schemas, required permissions, owning teams, supported environments, and operational status.
- Policy engine: Evaluates whether a client, user, service account, or automation agent can perform a requested action in a given repository, namespace, environment, or pipeline stage.
- Connector layer: Contains adapters for Git providers, CI systems, artifact stores, secret managers, cloud APIs, observability platforms, ticketing systems, and deployment controllers.
- Audit and telemetry pipeline: Records every tool invocation, input scope, decision, output status, latency, and downstream API result for investigation and compliance.
Component boundaries should reflect operational risk. Read-only context retrieval, such as fetching build status or summarizing failed tests, can be handled by broadly available MCP tools with narrow data scopes. Mutating actions, such as rerunning a production deployment, rotating a secret, changing an autoscaling policy, or merging a pull request, should pass through stricter authorization, approval, and audit paths. A practical design separates read tools from write tools and separates non-production operations from production operations, even when they target the same external platform.
For production scale, run the hub as a set of independently deployable services rather than a single monolith. The gateway, policy engine, context broker, and connector workers can scale differently under load. For example, observability queries may create high read volume during incidents, while deployment operations require lower throughput but stronger consistency and approval handling. Use queues for long-running actions, idempotency keys for repeated pipeline requests, and correlation IDs across every hop so a request can be traced from an assistant prompt to the final CI job, Kubernetes event, or ticket update.
| Design area | Recommended approach |
|---|---|
| Transport | Use TLS everywhere, short-lived credentials, and explicit service-to-service authentication between hub components. |
| State | Keep durable state for audit logs, tool registry metadata, approvals, and workflow execution records; avoid storing secrets or unnecessary source content. |
| Extensibility | Build connectors as versioned modules with clear schemas, ownership, test coverage, and backward-compatible changes. |
| Resilience | Add retries with backoff, circuit breakers, downstream timeout limits, and fallback responses for degraded provider APIs. |
The architecture should also include a clear context model. Each request should carry the actor, repository or service, environment, intended action, change reference, and execution source. This allows the hub to decide whether a user can inspect a failed staging build, request a test rerun, create a release branch, or promote an artifact to production. With well-defined components and context boundaries, the MCP Hub becomes a reliable integration layer rather than an unmanaged collection of automation shortcuts.
Connecting Source Control, Build, Test, and Deployment Tools
An MCP Hub becomes valuable when it can translate a developer request into coordinated actions across repositories, CI runners, artifact stores, test systems, and deployment targets. The integration layer should treat each DevOps platform as a capability provider exposed through an MCP server. For example, a GitHub or GitLab server can provide tools for listing pull requests, reading diffs, checking branch protection, and creating review comments, while a Jenkins, GitHub Actions, GitLab CI, or Buildkite server can expose pipeline status, job logs, rerun controls, and workflow dispatch actions.
Start by mapping the lifecycle of a change from commit to production. Source control integrations should support repository discovery, branch metadata, commit history, file reads, pull request state, CODEOWNERS lookup, and merge checks. Build integrations should expose pipeline templates, queued jobs, build artifacts, dependency manifests, and container image tags. Test integrations should return unit test results, integration test reports, coverage data, flaky test history, and security scan findings. Deployment integrations should connect to systems such as Argo CD, Flux, Spinnaker, Helm, Terraform Cloud, Kubernetes APIs, or cloud-native deployment services.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsRank #2

- ADJUSTABLE DEPTH: 4-Post 42U open frame server rack with 4 vertical rails and adjustable mounting depth 22" to 40" (56,0cm to 101,7cm); Compatible with various servers / switches / data / AV and other IT equipment; EIA/ECA-310-E Compliant
- EASY ASSEMBLY: Mobile network rack with easy-to-follow assembly instructions and online video; Compact flat-pack shipping to avoid damage and facilitate installation; Total product height of 80.3in (204 cm) with casters, 78in (198cm) without casters
- COLD ROLLED STEEL: Durable 4 Post 19in open frame rack designed for ventilation with 42U mounting height and 1320lb (600kg) weight capacity (stationary); 3 install options included: casters, levelling feet, or base-plate to secure rack to the floor
- HARDWARE INCLUDED: Rolling computer/data rack includes cage nuts and screws to mount equipment, easy to read Units (U) and depth adjustment markings, cable management hooks for organization, and required assembly tools
- THE IT PRO'S CHOICE: Designed and built for IT Professionals, this 42U rack is backed for 2-years, including free lifetime 24/5 multi-lingual technical assistance
Integration model by pipeline stage
| Stage | Typical systems | MCP capabilities to expose |
|---|---|---|
| Source control | GitHub, GitLab, Bitbucket, Azure Repos | Read files, inspect diffs, list pull requests, evaluate merge status |
| Build | Jenkins, GitHub Actions, GitLab CI, CircleCI, Buildkite | Trigger jobs, fetch logs, inspect artifacts, rerun failed stages |
| Test and quality | Snyk, JUnit reports, Playwright, Cypress | Summarize failures, compare coverage, identify vulnerable dependencies |
| Deployment | Argo CD, Flux, Kubernetes, Helm, Terraform Cloud | Inspect rollout state, promote versions, compare desired and live state |
Each connector should normalize platform-specific details into consistent resources and tools. A pull request from GitHub and a merge request from GitLab can both be represented as a change request with fields such as source branch, target branch, author, reviewers, checks, changed files, and approval state. Build jobs can share fields such as run ID, status, commit SHA, stage name, duration, logs URL, and artifact references. This common vocabulary lets agents and automation workflows reason across systems without hardcoding every vendor API shape.
Use event-driven connections where possible. Webhooks from source control can notify the MCP Hub when a pull request opens, a commit lands, or a tag is pushed. CI systems can send job started, job completed, and artifact published events. Deployment tools can publish sync, rollout, rollback, and health-change events. The hub can then update its context cache, trigger downstream MCP tools, or make fresh state available to an AI assistant responding to a release engineer. For reliability, webhook ingestion should be backed by a queue such as Kafka, SQS, Pub/Sub, or RabbitMQ so short platform outages do not drop pipeline events.
Design tool actions with clear boundaries. Reading a build log is low risk, but rerunning a production deployment, approving a release, or applying Terraform requires stricter controls. Tool names should be explicit, such as get_pipeline_run, summarize_test_failures, compare_deployment_revision, and request_environment_promotion. Prefer separate read and write tools instead of broad actions that can both inspect and mutate state. For production changes, return a preview of the planned action, require a confirmation step, and include the originating user, ticket ID, commit SHA, and environment in the request payload.
Version and test every connector like application code. Mock external APIs in contract tests, validate response schemas, and run integration tests against sandbox projects before enabling a connector in production. Keep vendor tokens, webhook secrets, and deployment credentials outside the connector code, preferably in a dedicated secret manager. With consistent schemas, event ingestion, and controlled write operations, the MCP Hub can connect the entire CI/CD toolchain while still preserving the guardrails expected in modern DevOps environments.
Designing Secure Context and Permission Boundaries
A production MCP Hub should treat every context request as a security-sensitive operation. The hub may expose repository metadata, pull request diffs, deployment status, incident timelines, build logs, secrets references, container image data, and cloud environment details. Without strict boundaries, an assistant or automation agent could unintentionally combine low-risk context with privileged actions, such as promoting a release, rotating credentials, or changing infrastructure. Secure design starts by separating read context, write actions, and approval-gated operations across all connected DevOps systems.
Use identity propagation rather than a shared global service account wherever possible. When a developer asks the MCP Hub to inspect a failed pipeline, the hub should evaluate the developer’s identity, team membership, repository access, and environment permissions before retrieving logs or artifacts. For machine-driven workflows, assign workload identities per automation path, such as release-s-generator, staging-deployer, or incident-triage-agent. Each identity should have only the scopes it needs in GitHub, GitLab, Jenkins, Argo CD, Kubernetes, Terraform Cloud, Datadog, Prometheus, or other integrated platforms.
Permission model design
Define permissions in layers so that access can be evaluated consistently before the MCP Hub calls downstream tools. A practical model includes user identity, tool capability, resource scope, environment tier, and action sensitivity. For example, reading build logs from a feature branch may be allowed automatically, while deploying to production requires a change ticket, an approved release candidate, and human confirmation. This model should be implemented in the hub’s authorization middleware, not left to each MCP server to interpret differently.
- Resource scopes: repository, branch, pull request, pipeline, artifact, cluster, namespace, service, dashboard, alert, and environment.
- Action classes: read-only queries, generated recommendations, non-production changes, production changes, and destructive operations.
- Environment boundaries: development, test, staging, production, regulated workloads, and customer-isolated environments.
- Approval states: automatic, peer-reviewed, change-managed, break-glass, and denied.
Context filtering is as as action authorization. The MCP Hub should redact secrets, tokens, private keys, customer identifiers, and sensitive configuration values before returning context to a model or downstream automation. Build logs and deployment manifests often contain accidental secrets, so integrate scanning and masking into the response path. For repository content, restrict access by path where needed; an assistant helping with application code may not need access to payroll configuration, production Terraform state, or security exception files.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Guardrails for high-risk operations
High-risk workflows should require explicit confirmation and durable audit records. Examples include production deployment, rollback, database migration, feature flag changes, infrastructure provisioning, firewall updates, and credential rotation. The MCP Hub can present a structured action plan that includes target environment, affected services, commit SHA, artifact digest, expected pipeline, approval reference, and rollback procedure. Only after validation should the hub invoke the appropriate MCP server to execute the operation.
| Operation | Recommended boundary | Control |
|---|---|---|
| Read CI logs | Repository and branch access | Identity check and secret masking |
| Deploy to staging | Service ownership | Scoped deployment token |
| Deploy to production | Environment role and release approval | Human approval and audit trail |
| Modify infrastructure | Workspace and cloud account scope | Policy-as-code validation |
Finally, centralize audit logging at the MCP Hub layer. Record who requested context, which MCP server was called, what resource was accessed, which action was proposed, which action was executed, and what policy decision was applied. Store correlation IDs across the hub, CI/CD systems, observability tools, and deployment platforms so security teams can reconstruct events during incident review. With strong identity propagation, scoped permissions, context redaction, and approval gates, the MCP Hub becomes a controlled automation layer rather than an unrestricted bridge into the delivery environment.
Automating Pipeline Workflows with MCP Servers
MCP servers turn pipeline automation into a set of callable, governed capabilities rather than a collection of brittle scripts spread across CI configuration files. In a DevOps hub, each MCP server can expose a focused interface for a domain such as source control, build orchestration, artifact management, test execution, release promotion, infrastructure changes, or incident response. The hub coordinates these servers so an AI assistant, workflow engine, or ChatOps command can request context, trigger actions, and receive structured results without needing direct access to every underlying tool.
Rank #3
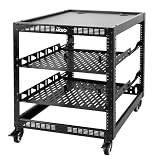
- 【Powerful load-bearing】12U Network Rack Open Frame is constructed from durable Cold Rolled Steel; Rack Shelf Back Support enhances stability; load-bearing capacity of 260lbs
- 【Sliding&Considerate】Open-frame layout, including four wheels easy to move, a top panel adding space, anti-slip shelf stops fixing devices and compatible racks for stack and expansion to meet requirements of home server rack
- 【Complete Accessories】A 12U open frame server rack, two ventilated shelves, four shelf stops, four casters, four velcro straps and a set of equipment mounting screws
- 【Versatile Application】Ideal for space-efficient multi-device setups in warehouses, retail, classrooms, offices and more; Excellent choices as AV Rack/IT Rack
- 【Effortless Setup】Server rack with wheels includes hardware, a comprehensive manual, mounting hole drilling template and an online assembly video to simplify setup
A practical design is to map common delivery activities into reusable MCP tools. For example, a repository server can expose operations to inspect changed files, open pull requests, fetch ownership metadata, and read branch protection status. A CI server can start a workflow, retrieve job logs, rerun failed stages, and summarize test failures. A deployment server can promote an artifact to staging, request an approval, check rollout status, and pause or roll back a release. By keeping these capabilities small and explicit, teams can compose larger automations while preserving reviewability and permission control.
Free tools Windows power users keep installed
One-click scans. No signup required.
Common workflow patterns
- Pull request validation: gather diff context, identify affected services, trigger targeted test suites, and return a structured readiness report to the pull request.
- Failure triage: collect build logs, recent dependency changes, flaky test history, and related incidents, then recommend a rerun, owner escalation, or rollback path.
- Release promotion: verify artifact signatures, check deployment windows, confirm approvals, validate environment health, and promote the same artifact across environments.
- Infrastructure automation: inspect Terraform or Kubernetes changes, run policy checks, create a plan summary, and require human approval before applying changes.
- ChatOps execution: allow engineers to trigger approved actions such as restarting a job, deploying a canary, or querying release status from Slack, Teams, or an internal portal.
Workflow automation should be event-driven where possible. Webhooks from Git providers, CI systems, artifact registries, observability platforms, and deployment controllers can publish events into a queue or event bus. The MCP hub then enriches each event with context, selects the right MCP server, and executes an approved workflow. This avoids polling, reduces latency, and creates a reliable trail from the original event to the resulting action. For long-running operations such as end-to-end tests or progressive deployments, the server should return a correlation ID and let the hub subscribe to status updates rather than blocking a request indefinitely.
Idempotency is essential for safe automation. MCP tools that trigger pipeline actions should accept stable request identifiers, detect duplicate submissions, and expose the current state of an operation. A deployment request, for instance, should not create two production rollouts if a client retries after a timeout. Similarly, rerun commands should target a specific workflow run and job, not “the latest failed build” unless that resolution is performed and recorded by the hub. This makes automated workflows predictable under network failures, queue redelivery, and concurrent user actions.
Example MCP automation flow
- A pull request webhook arrives with repository, branch, author, and commit metadata.
- The hub asks the repository MCP server for changed paths, CODEOWNERS data, and linked issue context.
- The hub asks the CI MCP server to run only the build and test jobs affected by the changed services.
- The observability MCP server provides recent service health and known flaky test signals.
- The hub posts a pull request comment with test results, risk indicators, missing approvals, and next allowed actions.
For production use, define workflow policies outside application code. Store rules for allowed actions, approval requirements, environment restrictions, maintenance windows, and escalation paths in versioned configuration. MCP servers should expose capabilities, while the hub decides when those capabilities may be used. This separation lets platform teams update delivery policy without redeploying every integration and helps auditors understand which automation paths can affect production.
Teams should also design MCP servers to return structured, machine-readable responses with concise human summaries. A failed build response might include job ID, failing step, log URL, suspected test file, retry eligibility, and owner group. A deployment response might include artifact digest, environment, rollout phase, health checks, and rollback handle. These fields let the hub chain follow-up actions reliably, generate useful notifications, and avoid parsing free-form logs unless deeper investigation is required.
Observability, Auditing, and Failure Handling
An MCP Hub used in DevOps and CI/CD pipelines needs the same level of visibility as any production control plane. It brokers requests between models, repositories, build systems, deployment platforms, secret managers, and observability tools, so a failure can affect both developer productivity and release safety. Treat the hub as an operational service: every tool call, context lookup, policy decision, and downstream response should produce structured telemetry that can be traced across the full workflow.
Telemetry model for MCP operations
Start by defining a consistent event schema for all MCP servers and adapters. Each request should include a correlation ID, actor identity, client application, target tool, operation name, environment, repository, commit SHA, pipeline ID, and authorization result. For long-running actions such as integration tests, image builds, security scans, and progressive deployments, emit lifecycle events such as requested, accepted, running, succeeded, failed, and cancelled. These events should be sent to a centralized logging platform and linked to metrics and traces.
- Logs: capture structured JSON records for MCP requests, tool responses, policy decisions, retries, and errors.
- Metrics: track request volume, latency, error rate, retry count, queue depth, token usage, downstream timeout rate, and policy denial rate.
- Traces: connect the model request to MCP routing, adapter execution, CI/CD API calls, deployment events, and observability lookups.
- Events: publish domain-specific records for build creation, test completion, artifact promotion, rollback, and incident correlation.
Dashboards should separate platform health from workflow health. Platform views show MCP gateway latency, server availability, adapter failures, cache performance, and rate-limit pressure. Workflow views show pipeline success rate, mean time to deploy, failed stage distribution, flaky test frequency, rollback count, and approval wait time. This separation helps teams distinguish a broken integration from a failing application release.
Audit trails and compliance evidence
Auditing should be immutable, queryable, and tied to real identities rather than anonymous model sessions. Record who initiated a request, which model or automation client made the tool call, what context was provided, which permissions were evaluated, and what downstream action was taken. Sensitive values such as secrets, tokens, environment variables, customer data, and proprietary source snippets should be redacted before storage. For regulated environments, write audit events to append-only storage or a security information and event management platform with retention policies aligned to compliance needs.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Repair Windows errors before they cause bigger problemsFix Now →| Audit item | Example fields | Use in operations |
|---|---|---|
| Tool invocation | actor, tool, operation, repository, environment | Reconstruct automated actions during incidents |
| Policy decision | role, scope, rule, decision, denial message | Validate least-privilege access controls |
| Deployment action | artifact, version, cluster, namespace, rollout status | Trace release changes to production impact |
| Context retrieval | source, document type, commit, ticket, dashboard | Verify which information influenced automation |
Failure handling patterns
Failures should be handled explicitly at the MCP layer instead of being passed through as opaque errors. Classify failures as authentication errors, authorization denials, validation errors, rate limits, timeouts, downstream service outages, conflicting state, and unsafe requested actions. Return clear machine-readable errors so the calling agent or workflow engine can decide whether to retry, request approval, fall back to read-only diagnostics, or stop the pipeline.
Use bounded retries with exponential backoff for transient API failures, but avoid retrying destructive operations unless they are idempotent. For deployments, require idempotency keys and state checks before repeating an action. Circuit breakers should isolate failing adapters so one unstable tool does not degrade the whole hub. Queue-based execution can absorb bursts from large monorepos or release trains, while dead-letter queues preserve failed jobs for later inspection.
Rank #4

- Adjustable Depth: 23-40'' adjustable depth is used for servers and network equipment, ensuring enough space for AV equipment, components, and cabling, while allowing you to access ports and equipment from multiple sides.
- Strong Load Capacity: Ground-Mounted Load Capacity: 500 lbs, Wall-Mounted Load Capacity: 150 lbs. The av rack is made of carbon steel for better weldability performance and can help save space while meeting your need to place multiple devices.
- User-friendly Design: Ergonomic design makes the open frame av rack easier to use. The additional top panel is able to place other items with more available space. Roller design moves anywhere and anytime, is convenient, and is more energy-saving.
- Complete Accessories: We provide the accessories you need, including 2 x Pallets, 145 x M5*10 Cross Head Screws, 4 x Casters, 4 x M10*50 Expansion Screws,10 x M6*12 Cage Nuts, 1 x Grounding Wire, 1 x User Manual.
- Wide Application: The server rack wall mount maximizes the use of available space, suitable for retail venues, classrooms, offices, and other places where space is limited.
Production MCP Hubs should also support safe degradation. If the observability backend is unavailable, allow read-only repository queries but block automated production deployment decisions that depend on live health signals. If a CI provider is degraded, expose current status and prevent duplicate pipeline creation. If policy evaluation fails, default to denial for write operations. Pair these controls with alerting that pages the owning team when error rates, policy failures, or deployment rollback events cross defined thresholds.
Production Deployment and Maintenance Best Practices
Running an MCP Hub in production requires the same discipline applied to critical CI/CD infrastructure: high availability, controlled rollout, strict change management, and continuous validation. The hub should be deployed as a stateless control-plane service where possible, with persistent state moved into managed databases, secret stores, artifact registries, and audit backends. This makes horizontal scaling straightforward and reduces recovery time when a node fails. Place the hub close to the systems it coordinates, such as source control, runners, deployment APIs, and observability platforms, while keeping clear network boundaries between development, staging, and production environments.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchA common production topology uses mulle MCP Hub instances behind an internal load balancer, with separate MCP servers for source control, CI orchestration, deployment, incident management, and telemetry. Each server should have narrowly scoped credentials and independent lifecycle management. For example, a Git MCP server may only read pull request metadata and changed files, while a deployment MCP server can trigger releases only through approved deployment APIs. Avoid bundling every integration into one large service; smaller, domain-specific servers are easier to test, rotate, scale, and isolate during incidents.
Deployment practices
- Use progressive delivery: roll out new hub versions with canary deployments, blue-green environments, or phased traffic shifting. Validate tool schemas, permission mappings, and workflow behavior before full promotion.
- Pin integration versions: lock MCP server versions, API clients, container images, and pipeline templates. Upgrade intentionally rather than relying on floating tags or implicit dependency updates.
- Separate environments: maintain distinct development, staging, and production hubs or tenant partitions. Test new tools and prompts against non-production repositories and deployment targets first.
- Automate configuration: manage connectors, policies, routing rules, and environment mappings through infrastructure as code. Store reviewed configuration in version control and apply it through audited pipelines.
Maintenance should focus on predictable behavior under changing toolchains. CI providers, repository platforms, cloud APIs, and observability systems frequently update authentication models, rate limits, pagination behavior, and webhook payloads. Add contract tests for each MCP server so schema changes are detected before they affect production workflows. These tests should verify authentication, authorization, read and write operations, error responses, timeout handling, and idempotency. For deployment integrations, include dry-run tests that confirm target selection, release metadata, rollback references, and approval gates without changing live workloads.
Operational teams should define service objectives for the hub, such as request latency, tool invocation success rate, workflow completion rate, and audit delivery lag. Alerting should distinguish between hub failures, downstream tool failures, policy denials, and user input errors. If a build provider is unavailable, the hub should return a clear failure state rather than retrying indefinitely or triggering duplicate jobs. Use bounded retries, circuit breakers, queue limits, and dead-letter handling for asynchronous actions. Every mutating operation, including pipeline triggers, environment promotions, secret rotations, and rollback requests, should carry a correlation ID that appears in logs, audit records, and downstream systems.
Security and lifecycle maintenance
- Rotate credentials regularly: use short-lived tokens where supported and automate rotation through a central secret manager.
- Review permissions: schedule access reviews for MCP servers, service accounts, repositories, environments, and deployment targets.
- Harden runtime environments: run containers as non-root users, apply network egress controls, restrict metadata service access, and scan images before deployment.
- Back up critical state: protect policy configuration, audit indexes, workflow definitions, and connector metadata with tested restore procedures.
Finally, treat the MCP Hub as a product owned by a platform team, not as a one-off integration layer. Publish supported tool catalogs, schema documentation, onboarding steps, incident procedures, and deprecation timelines. Track usage by team, repository, workflow type, and integration so capacity planning and cleanup decisions are based on evidence. With disciplined deployment, clear ownership, and continuous validation, the hub becomes a dependable control layer for DevOps automation rather than another fragile dependency in the delivery path.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Frequently Asked Questions
How is an MCP Hub different from a traditional DevOps integration platform?
An MCP Hub exposes tools, pipeline data, repository metadata, deployment state, and observability signals through a standardized Model Context Protocol interface. Instead of building one-off integrations between every system, teams create MCP servers that provide controlled access to specific capabilities such as reading build logs, triggering deployments, or querying incidents. This makes it easier for AI agents, automation services, and internal developer portals to work with the same governed context layer.
Which DevOps tools should be connected first when building an MCP Hub?
Start with the systems that carry the highest workflow value: source control, CI/CD pipelines, artifact registries, issue trackers, deployment platforms, and observability tools. For many teams, that means GitHub or GitLab, Jenkins or GitHub Actions, Jira, Kubernetes, Argo CD, Docker registries, Prometheus, Grafana, and an incident platform such as PagerDuty. Connect read-only capabilities first, then add controlled write actions such as rerunning a failed job or promoting a release.
How do you prevent an MCP Hub from becoming a security risk?
Use strong identity, short-lived credentials, scoped permissions, and policy-based access control for every MCP server and client. Separate read operations from write operations, require approval for destructive actions, and log every tool invocation with the user, agent, request, target system, and result. Secrets should stay in a vault or cloud secret manager, not inside prompts, configuration files, or pipeline logs.
Can an MCP Hub safely automate production deployments?
Yes, but production actions should be guarded by environment-specific policies, approval gates, rollout controls, and rollback procedures. The hub can gather release context, check test results, inspect change tickets, verify observability health, and trigger deployments only when required conditions are met. High-risk actions such as database migrations, traffic shifts, and cluster-wide changes should require human approval or a separate privileged workflow.
What should be monitored after the MCP Hub goes live?
Track MCP server availability, tool invocation latency, authentication failures, denied actions, rate limits, downstream API errors, and automation success rates. Audit logs should be searchable by user, agent, repository, environment, and action so teams can investigate incidents quickly. It is also useful to monitor prompt-driven automation outcomes, such as failed remediation attempts or repeated pipeline reruns, to catch unsafe or inefficient behavior early.
Bottom Line
Building an MCP Hub gives DevOps teams a unified, governed layer for connecting repositories, CI/CD pipelines, observability tools, deployment targets, and automation workflows. The strongest implementations start with clear architecture boundaries, secure tool access, well-defined context contracts, and production-ready monitoring from day one.
Start small by integrating a few high-value workflows such as pipeline diagnostics, deployment approvals, incident triage, or release summaries, then expand as trust and usage grow. Treat the hub like critical platform infrastructure: version it, audit it, secure it, and continuously refine it around the needs of developers, operators, and delivery teams.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

