Free tools Windows power users keep installed
One-click scans. No signup required.
Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Continuous code quality depends on catching issues early, consistently, and close to where developers already work. Static analysis, automated review, security scanning, style enforcement, and CI/CD quality gates help teams reduce defects, standardize practices, and keep fast-moving codebases maintainable.
Modern engineering teams can choose from tools that focus on different parts of the quality workflow: deep code analysis, pull request feedback, vulnerability detection, test coverage, formatting rules, or developer productivity metrics. The right choice often depends on language support, repository hosting, compliance needs, team size, and how tightly the tool fits into existing delivery pipelines.

This guide compares seven continuous code quality and automated code review tools, highlighting where each is strongest, where it may fall short, and which teams are most likely to benefit from it.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Clear out junk files and repair common Windows errors3Scan for outdated or missing drivers - takes under a minuteWhy Continuous Code Quality Matters
Continuous code quality turns review from a late-stage cleanup activity into a routine engineering practice. Instead of waiting for a release branch, security audit, or production incident to expose defects, teams run automated checks on every commit, pull request, and build. Static analysis, linting, dependency scanning, test coverage checks, and policy enforcement create fast feedback loops that help developers fix issues while the context is still fresh.
#1 Best Overall
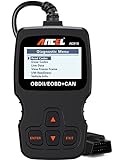
- CEL Doctor: The ANCEL AD310 is one of the best-selling OBD II scanners on the market and is recommended by Scotty Kilmer, a YouTuber and auto mechanic. It can easily determine the cause of the check engine light coming on. After repairing the vehicle's problems, it can quickly read and clear diagnostic trouble codes of emission system, read live data & hard memory data, view freeze frame, I/M monitor readiness and collect vehicle information
- Sturdy and Compact: Equipped with a 2.5 foot cable made of very thick, flexible insulation. It is important to have a sturdy scanner as it can easily fall to the ground when working in a car. The AD310 OBD2 scanner is a well-constructed mechanic tool with a sleek design. It weighs 12 ounces and measures 8.9 x 6.9 x 1.4 inches. Thanks to its compact design and light weight, transporting the device is not a problem. The buttons are clearly labelled and the screen is large and displays results clearly
- Accurate Fast and Easy to Use: The AD310 scanner can help you or your mechanic understand if your car is in good condition, provides exceptionally accurate and fast results, reads and clears engine trouble emission codes in seconds after you fixed the problem. This device will let you know immediately and fix the problem right away without any car knowledge. No need for batteries or a charger, get power directly from the OBDII Data Link Connector in your vehicle
- OBDII Protocols and Car Compatibility: Many cheap scan tools do not really support all OBD2 protocols. AD310 scanner as it can support all OBDII protocols such as KWP2000, J1850 VPW, ISO9141, J1850 PWM and CAN. This device also has extensive vehicle compatibility with 1996 US-based, 2000 EU-based and Asian cars, light trucks, SUVs, as well as newer OBD2 and CAN vehicles both domestic and foreign. Pls confirm with our customer service whether it is compatible with your vehicle before purchasing
- Home Necessity and Worthy to Own: This is an excellent code reader to travel or home with as it weighs less and it is compact in design. You can easily slide it in your backpack as you head to the garage, or put it on the dashboard, this will be a great fit for you. The AD310 is not only portable, but also accurate and fast in performance. Moreover, it covers various car brands and is suitable for people who just need a code reader to check their car
This matters because modern software changes constantly. A single application may include backend services, frontend frameworks, infrastructure-as-code, open source packages, containers, and deployment pipelines. Manual review alone cannot reliably catch every SQL injection risk, hardcoded secret, unused dependency, formatting drift, flaky test pattern, or performance anti-pattern across that surface area. Automated code review tools provide a consistent baseline, so human reviewers can focus on design, maintainability, domain behavior, and trade-offs instead of repetitive style and syntax issues.
Benefits for engineering teams
- Earlier defect detection: Issues found during pull requests are usually cheaper to fix than issues discovered during QA, staging, or production monitoring.
- Consistent standards: Shared rules for formatting, complexity, naming, test coverage, and secure coding reduce subjective review comments and uneven enforcement across teams.
- Reduced technical debt: Complexity thresholds, duplication checks, and maintainability ratings help teams prevent gradual decay in large or long-lived codebases.
- Stronger security posture: SAST, secret detection, dependency vulnerability checks, and license scanning catch common risks before code reaches production.
- Faster pull request cycles: Automated comments and status checks give developers immediate feedback, shortening the time between code submission and merge.
Continuous quality also supports scaling. In a small team, senior engineers may personally review most changes and informally teach standards. As the organization grows, that approach becomes harder to sustain. Different squads may adopt different practices, new contributors may miss established conventions, and reviewers may become bottlenecks. Tools such as CodeClimate, Codacy, DeepSource, Snyk Code, GitHub Advanced Security, Qodana, and Semgrep help encode quality expectations into repeatable checks that work across repositories and teams.
The business impact is practical: fewer regressions, more predictable releases, and less time spent on avoidable rework. Code quality checks also create measurable signals for engineering leaders, such as vulnerability counts, code smells, duplication rates, coverage trends, and pull request health. These metrics are not a replacement for engineering judgment, but they provide useful visibility into risk and improvement over time. When integrated into CI/CD pipelines, automated review becomes part of the delivery path, helping teams ship quickly without letting quality depend on memory, luck, or heroic manual effort.
Recommended Free Tools
Key Features to Look for in Automated Code Review Tools
Automated code review tools vary widely in scope. Some focus on linting and formatting, while others combine static analysis, dependency scanning, secret detection, test coverage, architecture rules, and pull request annotations. The best choice depends on your stack, release cadence, compliance needs, and how much feedback developers should receive before code reaches the main branch.
Static analysis depth and language coverage
A strong tool should understand the languages, frameworks, and build systems your team uses every day. Basic syntax checks are useful, but mature platforms detect null pointer risks, unsafe type usage, dead code, overly complex methods, duplicated , insecure API calls, and resource leaks. For polyglot teams, broad language support matters: JavaScript, TypeScript, Python, Java, C#, Go, PHP, Ruby, Kotlin, Swift, C, and C++ are common requirements. Teams working with infrastructure-as-code should also look for Terraform, Kubernetes, Dockerfile, and YAML analysis.
Pull request feedback and developer experience
The most effective tools meet developers where code review already happens. Look for integrations with GitHub, GitLab, Bitbucket, and Azure DevOps that add inline comments, quality gates, status checks, and merge-blocking policies directly to pull requests. Feedback should be precise enough to act on quickly, with file names, line numbers, severity levels, and remediation guidance. Excessive false positives lead to alert fatigue, so rule tuning, suppression workflows, and baseline support are essential for established codebases.
- Inline annotations: Shows issues next to the changed code instead of in a separate dashboard only.
- Quality gates: Blocks merges when coverage drops, vulnerabilities appear, or critical defects are introduced.
- Incremental analysis: Focuses on new and changed code so legacy problems do not overwhelm the team.
- Clear severity ratings: Helps reviewers distinguish formatting preferences from defects and security risks.
Security, compliance, and dependency checks
Modern code quality is closely tied to application security. Automated review tools should identify hardcoded secrets, vulnerable dependencies, unsafe cryptography, injection risks, path traversal, insecure deserialization, and permission misconfigurations. Software composition analysis is especially valuable for teams using open source packages because it maps dependencies to known CVEs, license obligations, and available upgrade paths. Regulated organizations may also need audit trails, policy reporting, role-based access controls, and evidence that checks ran before release.
Rank #2
CI/CD integration and automation controls
Code quality checks should run consistently across local development, pull requests, and CI/CD pipelines. Tools that provide command-line interfaces, container images, REST APIs, webhooks, and native pipeline integrations are easier to standardize across repositories. Support for Jenkins, GitHub Actions, GitLab CI, CircleCI, Azure Pipelines, Buildkite, and Kubernetes-based runners can reduce implementation friction. Teams should also evaluate runtime performance, caching, parallel execution, and whether the tool can analyze monorepos without slowing every build.
| Feature | What to Evaluate | Best for |
|---|---|---|
| Rule customization | Custom rules, severity tuning, suppression controls | Teams with internal coding standards |
| Security scanning | SAST, secrets, dependencies, license checks | Security-conscious and regulated teams |
| PR integration | Inline comments, merge checks, reviewer-friendly output | Teams using trunk-based or pull request workflows |
| Reporting | Trends, technical debt, coverage, compliance exports | Engineering managers and platform teams |
Finally, consider administration and adoption. A useful tool should support centralized policies without preventing teams from tailoring rules to their services. Dashboards should show trends such as defect density, coverage movement, unresolved vulnerabilities, and maintainability ratings. Pricing model also matters: per developer, per repository, per line of code, and enterprise licensing can create very different costs at scale. The right platform improves review quality without turning every pull request into a long negotiation over noisy findings.
7 Continuous Code Quality and Automated Code Review Tools
The best automated code review tools reduce manual review burden while making quality checks repeatable across every pull request, branch, and release pipeline. The seven tools below cover static analysis, security scanning, style enforcement, maintainability scoring, and CI/CD integration for teams working across different languages and repository platforms.
1. CodeClimate Quality
CodeClimate Quality focuses on maintainability, technical debt, duplication, complexity, and style issues. It is especially useful for engineering managers and teams that want an accessible code health score and pull request feedback without heavy setup. CodeClimate works well for web application teams using languages such as Ruby, JavaScript, TypeScript, Python, PHP, and Go. Its strength is clear reporting for maintainability trends, though teams needing deep enterprise governance or extensive custom rules may prefer a broader platform.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
2. Codacy
Codacy provides automated code review for style, security, complexity, coverage, duplication, and compliance-related checks. It supports dozens of languages and integrates with GitHub, GitLab, and Bitbucket. Codacy is a good option for teams that want quick onboarding, pull request annotations, and standardized rules across repositories. It also includes security scanning and coverage tracking, making it useful for startups and mid-sized engineering teams that need one platform for several quality signals.
3. GitHub Advanced Security
GitHub Advanced Security is a natural choice for teams already using GitHub Enterprise. It includes CodeQL-powered code scanning, secret scanning, dependency review, and security alerts. Its strongest use case is application security embedded directly into the developer workflow, with findings shown in pull requests and repository security views. It is less of a general maintainability platform than CodeClimate, but it is excellent for teams prioritizing vulnerability detection, supply chain security, and native GitHub integration.
4. Snyk Code
Snyk Code is a developer-focused static application security testing tool designed to identify vulnerabilities in source code. It is part of the broader Snyk platform, which also covers open source dependencies, containers, and infrastructure as code. Snyk Code is well suited for teams adopting DevSecOps practices and shifting security checks earlier in development. It provides actionable remediation guidance and integrates with common repositories, IDEs, and CI/CD pipelines.
Rank #3

- OE-Level diagnostics on your smart device
- FREE Software updates - No subscriptions, no fees – EVER
- Full bi-directional control, live actuation test
- Supports 23 vehicle reset/relearn functions, including throttle matching, ABS bleeding, TPMS reset, etc.
- Live data mapping and freeze frame capturing
5. DeepSource
DeepSource analyzes code for bugs, anti-patterns, style violations, security issues, and performance concerns. It supports languages such as Python, Go, JavaScript, TypeScript, Java, Ruby, and Rust. One of its notable strengths is automatic issue fixing for selected problems, which can save time on repetitive cleanup. DeepSource is a practical fit for teams that want fast pull request feedback, repository-level quality tracking, and a developer-friendly interface without maintaining extensive custom infrastructure.
6. ESLint, Prettier, and language-native linters
Not every team needs a full platform for every quality check. ESLint, Prettier, Ruff, Pylint, Checkstyle, Stylelint, and similar language-specific tools remain essential for enforcing style, formatting, and common coding rules close to the developer environment. They are highly configurable, fast to run in CI, and easy to apply as pre-commit hooks. These tools are often paired with broader platforms such as Semgrep, GitHub Advanced Security, or Snyk to provide both local enforcement and organization-level reporting.
7. Semgrep
Semgrep scans source code with customizable rules to find security and quality issues, and it can run in pull requests and CI pipelines. Its rule-based approach is a practical fit for teams that want targeted checks and fast feedback across supported languages and repositories.
| Tool | Primary Strength | Best Fit |
|---|---|---|
| CodeClimate Quality | Maintainability and technical debt reporting | Product teams tracking code health over time |
| Codacy | Automated PR review across many languages | Teams wanting quick setup and broad checks |
| GitHub Advanced Security | Code scanning, secrets, dependency security | GitHub Enterprise teams focused on AppSec |
| Snyk Code | Developer-first security analysis | DevSecOps teams shifting security left |
| DeepSource | Static analysis with automated fixes | Teams seeking fast feedback and cleanup automation |
| Linters and formatters | Style, formatting, and local enforcement | Any team standardizing everyday coding practices |
| Semgrep | Customizable code scanning for security and quality | Teams wanting targeted checks in pull requests and CI |
Tool-by-Tool Comparison: Strengths, Limitations, and Best Fit
Each code quality tool approaches automated review from a different angle. Some focus on maintainability and technical debt, others on security, dependency risk, or pull request feedback. The right choice depends on your language stack, hosting model, compliance needs, and how much customization your team wants in the review process.
| Tool | Strengths | Limitations | Best Fit |
|---|---|---|---|
| Code Climate | Clear maintainability metrics, test coverage tracking, GitHub pull request annotations, and easy visibility into technical debt trends. | Less security-focused than dedicated SAST tools, and deeper customization may be limited compared with self-managed platforms. | Product teams that want lightweight maintainability monitoring and readable feedback for developers and managers. |
| Codacy | Automated style checks, security patterns, duplication analysis, coverage reporting, and integrations with GitHub, GitLab, and Bitbucket. | Rule results can vary by language ecosystem, and teams may need time to configure standards consistently across projects. | Engineering groups looking for fast SaaS-based automated reviews with flexible repository integrations. |
| DeepSource | Strong static analysis, autofix suggestions, issue categorization, secrets detection, and support for modern developer workflows. | Language coverage is more selective than some older platforms, so teams should verify support for all critical services. | Teams that want actionable pull request feedback with automated fixes for common quality and security issues. |
| GitHub CodeQL | Powerful semantic code analysis, native GitHub integration, custom query support, and strong security vulnerability detection. | Best experience is inside GitHub, and writing custom CodeQL queries requires specialized knowledge. | Security-conscious teams using GitHub Actions that need advanced application security scanning in CI. |
| Snyk Code | Developer-friendly security scanning, fast feedback, IDE integrations, and connection to Snyk’s dependency and container security tools. | Primary emphasis is security rather than general style, duplication, or maintainability governance. | Teams prioritizing secure development practices and wanting one platform for code, dependencies, containers, and IaC. |
| ESLint | Highly configurable JavaScript and TypeScript linting, large plugin ecosystem, autofix support, and easy CI enforcement. | Focused on the JavaScript ecosystem and does not provide broad cross-language quality management by itself. | Frontend, Node.js, and TypeScript teams that need precise style, correctness, and framework-specific rules. |
| Semgrep | Customizable rules for code security and quality scanning in pull requests and CI. | Teams need to select and maintain rules that match their languages and coding standards. | Teams wanting targeted, fast code checks integrated into development workflows. |
Code Climate and Codacy are practical choices for teams that prefer hosted tools with fast pull request feedback and simpler dashboards, while Semgrep suits teams that want targeted, customizable code checks in their existing workflows.
For security-heavy workflows, GitHub CodeQL and Snyk Code stand out. CodeQL is especially effective for deep semantic analysis and custom vulnerability research, while Snyk Code is better suited to teams that want developer-friendly security checks alongside dependency and container scanning. These tools can complement general quality platforms rather than replace them.
DeepSource sits between general quality automation and developer productivity, with useful autofix capabilities and practical issue grouping. ESLint, while narrower in scope, remains essential for JavaScript and TypeScript teams because it enforces local conventions before code reaches CI. In many engineering environments, the best setup is layered: ESLint or similar linters for language-specific standards, Codacy or Semgrep for repository-level checks, and CodeQL or Snyk for security-focused analysis.
Rank #4
- [Diagnose Like a Pro] BlueDriver Pro Next-Gen is a professional OBD2 scanner and diagnostic tool that helps you scan, understand, and clear vehicle trouble codes with confidence. Turn your phone into a powerful car diagnostic scanner—no guesswork, no unnecessary repairs.
- [Read and Clear More Codes Than Ever] Read and clear more codes than basic car code readers. Access enhanced diagnostics for Check Engine, ABS, SRS, Airbag, TPMS, Transmission, and more on supported vehicles, including expanded coverage on newer model years.
- [Verified Fixes and Real-Time Data] Get unlimited, technician-verified repair reports matched to your VIN, with definitions, causes, and confirmed fixes. Monitor live vehicle data as you drive, view freeze frames, check smog readiness, and analyze Mode 6 test results.
- [Expanded Make & Model Coverage] Optimized for today’s vehicles with strong support for GM, Ford, Stellantis (RAM, Jeep, Chrysler), Toyota, Honda, Nissan, Mazda, Subaru, Hyundai, Mercedes-Benz, BMW, and VW. Enhanced communication on select 2024+ Nissan and Mazda models (see compatibility chart).
- [Gas Vehicles 1996+ & Select Light-Duty Trucks] Works with all gas-powered vehicles made in 1996 or newer, plus select light-duty trucks and diesels, including F-250, RAM 2500, Silverado, and Sierra. Built for daily drivers, family vehicles, and real-world truck use.
How to Integrate Code Quality Checks into CI/CD Workflows
Integrating code quality checks into CI/CD turns static analysis, formatting, security scanning, and test coverage from occasional cleanup tasks into repeatable release safeguards. The goal is to give developers fast feedback while preventing risky code from reaching shared branches, staging, or production. A practical setup usually combines lightweight checks on every pull request with deeper analysis during merge, nightly, or release pipelines.
Start by deciding which checks should run at each stage of the delivery process. Pre-commit hooks are useful for fast formatting and linting with tools such as ESLint, Prettier, Black, or Checkstyle. Pull request pipelines should run automated code review, unit tests, dependency checks, and static analysis through platforms such as Codacy, Code Climate, DeepSource, Semgrep, or GitHub Advanced Security. Main branch and release pipelines can run slower tasks, including full test suites, container scanning, software composition analysis, and compliance reports.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →A practical CI/CD rollout pattern
- Define quality gates: Set measurable thresholds for issues such as critical vulnerabilities, duplicated code, test coverage, maintainability ratings, and new code defects.
- Start with non-blocking reports: Run tools in advisory mode for one or two sprints so teams can review findings, tune rules, and remove noisy checks.
- Enforce on new code first: Block pull requests only for issues introduced by the current change. This avoids forcing teams to fix years of legacy debt before shipping small updates.
- Make results visible in pull requests: Configure inline comments, status checks, and annotations so developers can act without leaving GitHub, GitLab, Bitbucket, or Azure DevOps.
- Escalate gradually: Once the signal is reliable, make critical security findings, failed tests, broken builds, and severe maintainability regressions merge-blocking.
CI configuration should keep feedback fast. Run quick linters, type checks, and targeted tests first, then stop the pipeline early if they fail. Use dependency caching for package managers such as npm, Maven, Gradle, pip, or NuGet to reduce build time. For larger repositories, split checks by language, service, or directory so unrelated teams are not waiting on the entire codebase. Monorepos often benefit from path-based pipeline triggers that run only the tools needed for changed components.
| Pipeline stage | Common checks | Typical enforcement |
|---|---|---|
| Pre-commit | Formatting, linting, secret detection | Local warning or blocked commit |
| Pull request | Static analysis, unit tests, coverage, dependency scanning | Required status checks |
| Main branch | Full test suite, security scans, code quality gates | Failed build blocks promotion |
| Release | Container scanning, license checks, compliance artifacts | Release approval requirement |
Teams should also assign ownership for code quality findings. Route alerts to the developers responsible for the changed files, publish dashboards for engineering managers, and create a triage process for false positives. Suppression should require a short justification, especially for security and reliability rules. Over time, review trends such as recurring rule violations, slow pipelines, and ignored warnings to adjust standards. The best CI/CD integration is not the one with the most checks; it is the one that consistently catches meaningful problems early without slowing delivery to a crawl.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Choosing the Right Tool for Your Team
The best code quality tool is the one your team will actually use consistently. A platform with deep rule customization, security scanning, and enterprise dashboards may be unnecessary for a small product team that mainly needs fast pull request feedback. Likewise, a lightweight linter may not be enough for an organization managing dozens of services, regulated data, and mulle programming languages. Start by mapping the tool to your delivery model: repository hosting, CI/CD system, language stack, compliance needs, release cadence, and the amount of time developers can spend maintaining quality rules.
Match the tool to your main quality goal
- For broad static analysis and maintainability: Code Climate, Codacy, and DeepSource are strong choices when teams want maintainability feedback, duplication checks, coverage tracking, and repository-level quality checks.
- For pull request automation: Codacy, Code Climate, and DeepSource work well when teams want inline comments, trend reporting, and automated feedback before code is merged.
- For security-focused engineering: Snyk Code is better suited when dependency risk, vulnerability discovery, and secure coding patterns are central requirements.
- For style consistency and local enforcement: ESLint, Prettier, Checkstyle, RuboCop, and similar linters remain valuable when teams need fast feedback directly in editors, pre-commit hooks, and CI jobs.
- For AI-assisted review: GitHub Copilot code review features and similar assistants can help flag suspicious changes, suggest improvements, and reduce reviewer fatigue, but they should complement deterministic scanners rather than replace them.
Language support should be one of the first filters. A JavaScript-heavy team may get excellent results from ESLint, Prettier, and DeepSource, while a Java, C#, or C++ organization may need stronger enterprise static analysis and deeper IDE integration. Polyglot teams should favor tools with broad language coverage, unified reporting, and configurable rules per repository. If each team uses a different scanner with no shared reporting, engineering leaders may struggle to see systemic issues such as declining coverage, repeated security findings, or services with high technical debt.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Evaluate workflow fit before feature depth
Integration quality often matters more than the number of rules advertised. Check whether the tool works cleanly with GitHub, GitLab, Bitbucket, Azure DevOps, Jenkins, CircleCI, or your existing pipeline runner. A good fit should support branch and pull request analysis, status checks, merge blocking, baseline comparisons, and clear ownership of findings. Developers should be able to understand a failed check without leaving the pull request, and teams should be able to tune noisy rules quickly. Excessive false positives can lead to ignored warnings, disabled checks, or rushed exceptions.
Best Value

- 【Diagnose Check Engine Light in Seconds – No Mechanic Needed】The FOXWELL NT301 OBD2 scanner instantly reads & clears engine fault codes (DTCs) with one click. Simply plug into the 16-pin DLC port, turn ignition on, and get accurate results within seconds—No prior car knowledge required. Save hundreds on dealership fees by knowing exactly what’s wrong before you visit a shop. The #1 choice car scanner for DIYers and car owners who want to take control of their vehicle’s health
- 【Clear & Reset CEL with Confidence】Unlike cheap code readers that just erase codes temporarily, NT301 works like all professional vehicle code readers: It clears the check engine light only after you’ve fixed the underlying issue. If the problem isn’t fully repaired, the fault code will reappear. So you’ll never get a false pass. Use the foxwell scanner to verify your repair work and drive with peace of mind
- 【Sm-og Check Helper – Know Your Pass/Fail Status Before the Test】With dedicated one-click I/M readiness hotkeys and a simple Red-Yellow-Green LED indicator, you’ll instantly know if your vehicle is ready for annual testing. Built-in speaker provides clear audio feedback. No guesswork—just confidence before you head to the test center. One less thing to worry about when inspection day comes
- 【Advanced OBDII Modes – O- 2 Sensor & EVAP Testing】NT301 go beyond basic code reading with enhanced OBD2 modes. Run an EVAP system check to assess fuel tank condition, and use the O- 2 sensor test to optimize air-fuel ratio, boosting fuel economy, cutting em- issions, and saving you money at the pump. The code reader for cars and trucks is like having a mini em-issions lab in your glove box
- 【Live Data Graphing – Spot Engine Issues in Real Time】View and log live sensor data in easy-to-read graphs with this OBD2 scanner diagnostic tool. Monitor ox- ygen sensors, fuel trims, coolant temperature, RPM, and more to spot suspicious values instantly. This obd scanner gives you professional-grade insight without the pro price tag—a feature you won’t find on basic $20 car code readers
| Team situation | Selection priority | Typical fit |
|---|---|---|
| Small startup shipping quickly | Low setup effort, fast pull request feedback | Codacy, DeepSource, ESLint, Prettier |
| Enterprise with many repositories | Governance, quality gates, reporting, permissions | Code Climate, Codacy, DeepSource |
| Security-sensitive product team | Vulnerability detection and secure coding checks | Snyk Code plus dependency scanning |
| Highly customized engineering standards | Rule configuration and policy control | Semgrep, language-native linters |
Cost and administration should also be reviewed early. Some tools are priced per developer, some per repository, and others by lines of code or enterprise tier. Include the hidden cost of maintaining rule sets, triaging findings, training developers, and supporting exceptions. For most teams, a practical approach is to pilot two tools on the same repositories for several weeks. Compare setup time, signal quality, developer sentiment, CI runtime impact, and the percentage of findings that result in real fixes. Choose the tool that improves review quality without slowing delivery unnecessarily.
Frequently Asked Questions
What is the difference between static analysis and automated code review?
Static analysis scans source code without running it to find bugs, security issues, complexity, duplication, and style violations. Automated code review is broader: it can include static analysis, pull request comments, dependency scanning, test coverage checks, formatting enforcement, and CI/CD quality gates. In practice, many teams use static analysis as one part of an automated review workflow.
Which code quality tool is best for a team using GitHub Actions?
GitHub-native teams often start with GitHub CodeQL for security analysis because it integrates directly with repositories, pull requests, and security alerts. Snyk, Codacy, DeepSource, and Code Climate also work well with GitHub Actions through marketplace actions or CLI steps. The best choice depends on whether your priority is security scanning, maintainability metrics, style enforcement, or consolidated quality reporting.
Can automated code review tools replace human code reviews?
No, these tools are best used to remove repetitive review work, not replace engineering judgment. They can catch common bugs, risky dependencies, formatting problems, test coverage drops, and policy violations before a reviewer spends time on the pull request. Human reviewers are still needed for architecture, product behavior, readability, edge cases, and maintainability tradeoffs.
How should we choose between Snyk, CodeQL, Codacy, DeepSource, Code Climate, Qodana, and Semgrep?
Choose Snyk when dependency, container, and open-source vulnerability scanning are central concerns, and choose CodeQL when GitHub-based security analysis is the main need. Codacy, DeepSource, and Code Climate are strong for pull request feedback and maintainability workflows, while Qodana is a natural fit for teams already using JetBrains IDEs and Kotlin, Java, or JVM-heavy stacks. Semgrep suits teams that want targeted, customizable code checks in pull requests and CI.
How strict should code quality checks be in CI/CD pipelines?
Start with non-blocking checks so the team can see recurring issues without slowing delivery. After the rules are tuned and false positives are reduced, make high-confidence checks blocking, such as critical security findings, severe bugs, failed tests, and major coverage drops. Many teams also apply stricter gates only to new or changed code so legacy issues do not block every deployment.
Bottom Line
Continuous code quality works best when automated review, static analysis, security scanning, and style enforcement are built directly into the developer workflow. The right tool depends on your stack, team size, compliance needs, and how tightly you want quality gates integrated into pull requests and CI/CD pipelines.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallStart by matching each tool’s strengths to your biggest quality risks, then trial one or two options on an active repository. Measure signal quality, developer adoption, false positives, and deployment friction before standardizing across the organization.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

